
Phishing Campaign Uses Invisible Unicode Characters to Hide Finance Lures
Summary
Microsoft says an active finance-themed phishing campaign used invisible Unicode characters to evade email filters, reaching up to 2.37 million messages daily. Defender blocked over 99% using other signals.
Key points
- Attackers inserted invisible Unicode tag characters into finance-related words, splitting terms such as “funding” to evade keyword-based email filters.
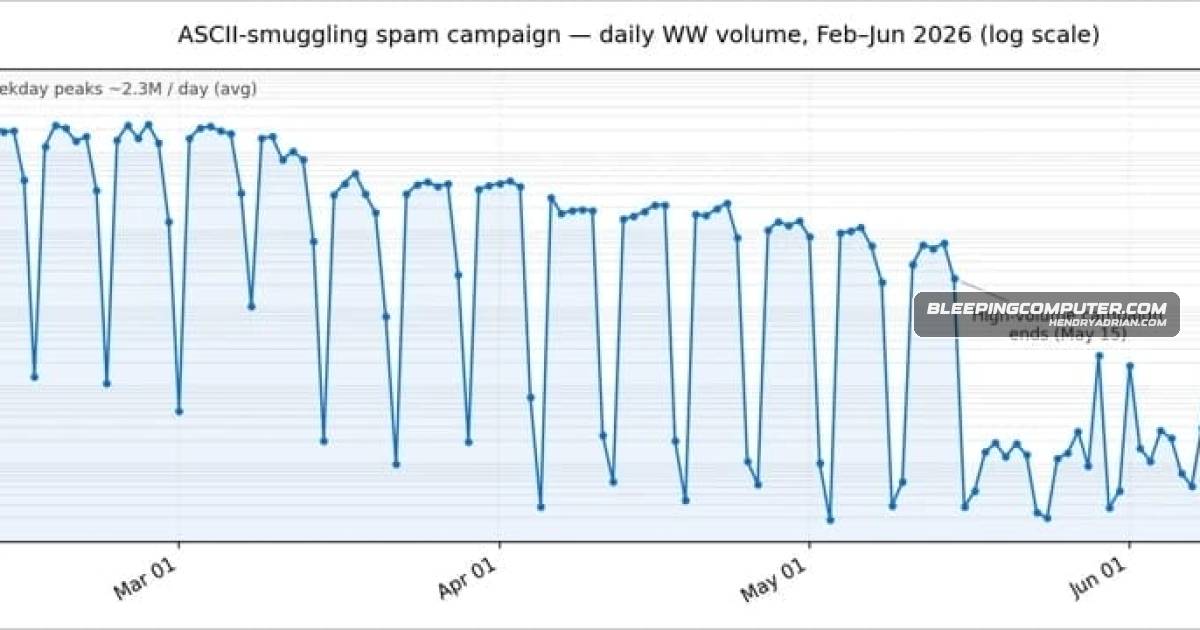
- The campaign peaked at up to 2.37 million daily messages; Microsoft says the technique’s high-volume phase declined after May 15, 2026, but the campaign remains active.
- Microsoft identified 148 finance-themed sender domains associated with about 96% of messages flagged by new Defender for Office 365 hunting logic for Unicode-tag signatures.
- Defender blocked over 99% of the messages using other signals, including sender, IP, domain, and reputation checks.
- Microsoft recommends normalizing or stripping invisible Unicode code points before keyword, regex, or signature detection—and before passing email content to AI assistants.
Article Details
- Event Type
- Phishing campaign using invisible Unicode characters to evade email security filters
- Impact
- Microsoft observed a finance-themed campaign that peaked at up to 2.37 million messages per day. The technique split lure words with invisible Unicode tag characters to evade keyword-based filtering; Defender still blocked over 99% of the messages using other signals. The messages were delivered through infrastructure associated with the legitimate ActiveCampaign email-marketing platform.