
BigBear 2.0 Phishing Service Bypassed MFA at 258 Organizations
Summary
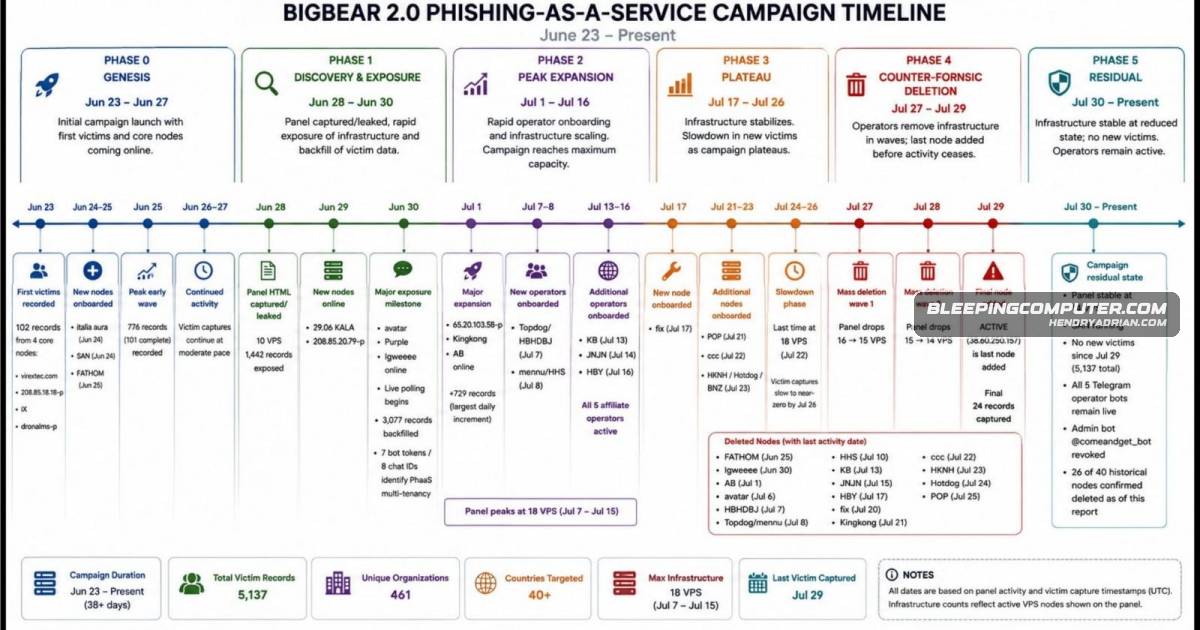
CloudSEK found BigBear 2.0 used an Evilginx2-based AiTM framework to bypass MFA at 258 organizations and steal more than 5,000 Microsoft 365 credentials. The researchers said the operation was still active, though its phishing infrastructure had been offline for nearly
Key points
- CloudSEK reported 258 distinct organizations had at least one completed MFA-bypass compromise; 461 appeared in the broader targeting dataset.
- The researchers said the panel exfiltrated 5,137 credential records, including 1,032 plaintext passwords and 4,148 session cookies.
- BigBear 2.0 used an Evilginx2-based adversary-in-the-middle framework to capture credentials and authenticated session cookies for account hijacking.
- CloudSEK found 42 VPS nodes and at least five affiliate operators receiving stolen credentials through live Telegram exfiltration bots.
- The service used custom JavaScript to interfere with FIDO2/WebAuthn and geo-matched residential proxies across 69 countries.
- CloudSEK said it notified law enforcement and affected organizations. At the time of reporting, the administration panel remained online, while the phishing infrastructure had been offline for nearly three weeks.
- Recommended steps for potentially affected organizations included resetting exposed passwords, revoking sessions and tokens, and requiring re-authentication for privileged accounts.
Article Details
- Attack Vectors
- BigBear 2.0 used an Evilginx2-based adversary-in-the-middle proxy to intercept Microsoft 365 credentials and authenticated session cookies during victims' authentication, including MFA.
- Custom JavaScript interfered with FIDO2/WebAuthn browser functionality, steering targets toward weaker authentication methods.
- Geo-matched residential proxies were used to make authentication activity appear consistent with victims' locations.
- Captured credentials and session cookies were replayed through an API to hijack authenticated sessions.
- Defensive Notes
- Reset exposed passwords, revoke active sessions, refresh tokens, and force re-authentication for high-privileged accounts.
- Enforce phishing-resistant FIDO2/WebAuthn authentication.
- Use Conditional Access policies requiring managed devices rather than relying on geolocation signals.
MITRE ATT&CK
T1056.003 · Web Portal CaptureThe phishing framework captured credentials, including passwords and MFA, through its authentication proxy.T1539 · Steal Web Session CookieThe operation captured Microsoft 365 session cookies and replayed them to hijack authenticated sessions.T1557.003 · DHCP SpoofingBigBear 2.0 used an Evilginx2-based adversary-in-the-middle proxy to intercept credentials and authenticated session cookies.
Products
Tools
BigBear 2.0BigBear 2.0 is a phishing-as-a-service framework that bypassed MFA at 258 organizations and stole over 5,000 Microsoft 365 credentials using an Evilginx2-based adversary-in-the-middle setup.Evilginx2BigBear 2.0 is a phishing-as-a-service framework that bypassed MFA at 258 organizations and stole over 5,000 Microsoft 365 credentials using an Evilginx2-based adversary-in-the-middle setup.