
Trezor Says Brevo Breach Fueled Phishing Targeting 347,000 Users
Summary
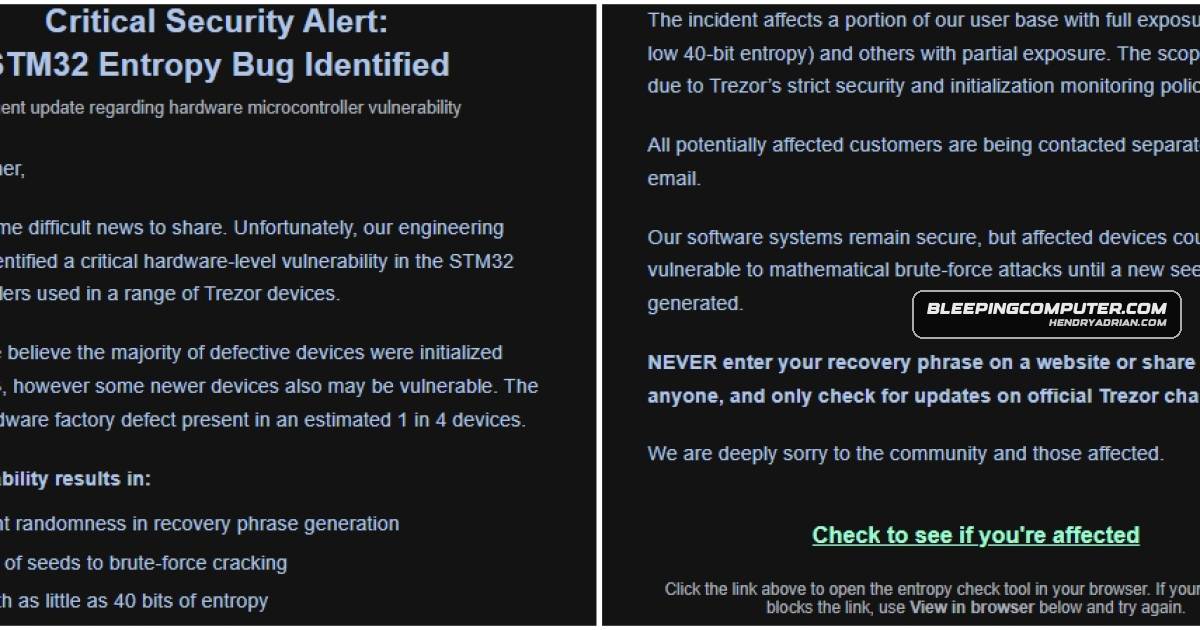
Trezor says attackers used access to email provider Brevo to target 347,000 newsletter addresses with phishing emails; about 2,500 users clicked a link seeking wallet backup information before Trezor disabled it.
Key points
- Trezor attributed the phishing campaign to an unauthorized actor who accessed Brevo, its third-party newsletter provider.
- The emails targeted roughly 347,000 addresses on Trezor’s opt-in newsletter list.
- The messages impersonated a critical security alert about STM32 microcontrollers and linked to an app that requested wallet backup information.
- Trezor said about 2,500 users clicked the link before it took down the domain within 20 minutes.
- Trezor said no other Trezor systems were affected by the Brevo incident and that it suspended its Brevo account.
- The article also notes earlier Trezor customer-data breaches involving its support portal and ShipMonk, its logistics provider.
Article Details
- Victim Organization
- Trezor
- Incident Type
- Phishing campaign using email sent through a breached third-party provider; the emails attempted to steal wallet backup information.
- Incident Date
- 2026-09-09
- Data Types Exposed
- Email addresses
- Affected Records
- Approximately 347,000 email addresses were targeted; approximately 2,500 users clicked the malicious link. The article does not report confirmed theft of wallet backup information.
- Operational Impact
- Trezor suspended its Brevo account, and the phishing domain was taken down within 20 minutes. Trezor said no other Trezor system was touched.
- Ransom Or Extortion
- BleepingComputer reported that ShipMonk received extortion emails from ShinyHunters following a separate breach. The article does not report an extortion demand tied to the phishing campaign against Trezor.
- Claim Status
- confirmed
MITRE ATT&CK
Threat Actors
Vendors
BrevoTrezor said phishing emails tied to a breach at Brevo targeted 347,000 email addresses and tricked 2,500 users into clicking a malicious link that tried to steal wallet backup information.ShipMonkThe company also linked the campaign to earlier third-party breaches, including ShipMonk and a previous support portal intrusion, highlighting repeated exposure of customer data.
Products
Countries
BrazilThe company said that the incident also affected customers in Brazil, Colombia, Italy, Portugal, Sweden, and the United Kingdom who received orders between May 10 and August 8, 2026.ColombiaThe company said that the incident also affected customers in Brazil, Colombia, Italy, Portugal, Sweden, and the United Kingdom who received orders between May 10 and August 8, 2026.ItalyThe company said that the incident also affected customers in Brazil, Colombia, Italy, Portugal, Sweden, and the United Kingdom who received orders between May 10 and August 8, 2026.PortugalThe company said that the incident also affected customers in Brazil, Colombia, Italy, Portugal, Sweden, and the United Kingdom who received orders between May 10 and August 8, 2026.SwedenThe company said that the incident also affected customers in Brazil, Colombia, Italy, Portugal, Sweden, and the United Kingdom who received orders between May 10 and August 8, 2026.United KingdomThe company said that the incident also affected customers in Brazil, Colombia, Italy, Portugal, Sweden, and the United Kingdom who received orders between May 10 and August 8, 2026.