
Cyberattack on Stadler Rail Exposes Supplier Data-Exchange Platform
Summary
Stadler Rail said criminals accessed a data-exchange platform with a supplier in a mid-July 2026 cyberattack. The company said its IT systems were unharmed, no sensitive or personal data was stolen, and it refused a 10 million-franc ransom demand.
Key points
- The incident occurred in mid-July 2026 and involved access to a data-exchange platform Stadler Rail used with a supplier.
- Stadler Rail said its IT systems were not affected and no sensitive or personal data was stolen.
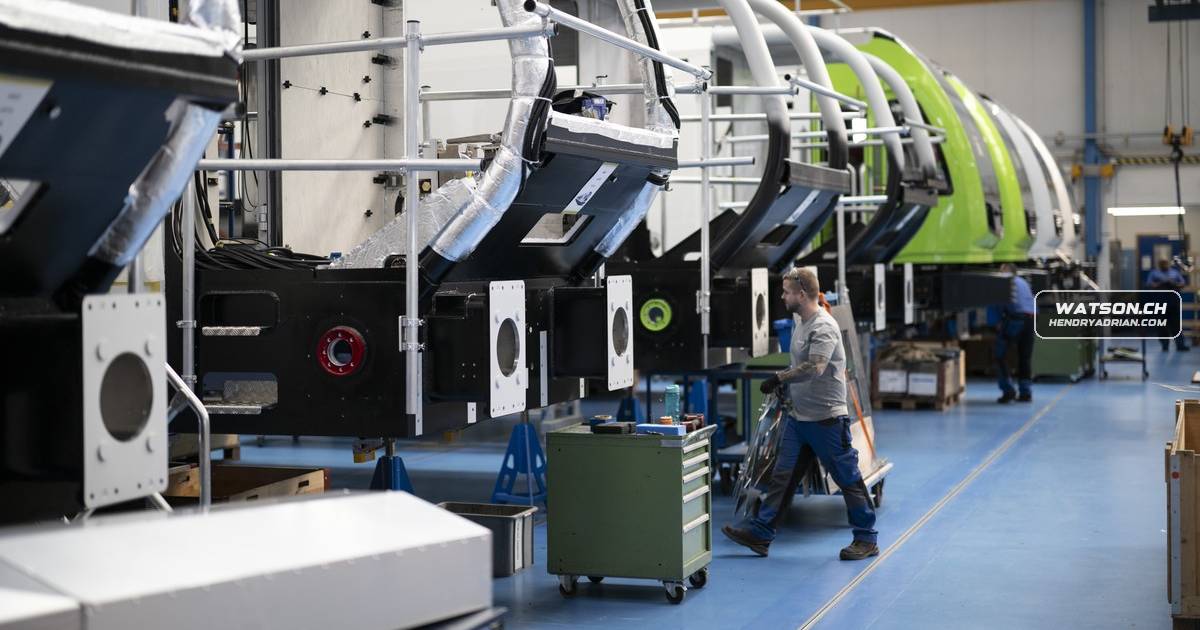
- The company said worldwide production is continuing normally.
- Stadler Rail said it refused a 10 million-franc ransom demand from the Everest Group.
- The company said it filed a criminal complaint.
Article Details
- Victim Organization
- Stadler Rail
- Incident Type
- Cyberattack involving unauthorized access to a data-exchange platform shared with a supplier
- Incident Date
- 2026-07-15
- Operational Impact
- The company said its IT systems remained unaffected and production continued normally worldwide.
- Ransom Or Extortion
- Everest Group demanded CHF 10 million; Stadler Rail said it did not pay.
- Claim Status
- confirmed