
Koyasan University Reports Ransomware Infection of Administrative Servers
Summary
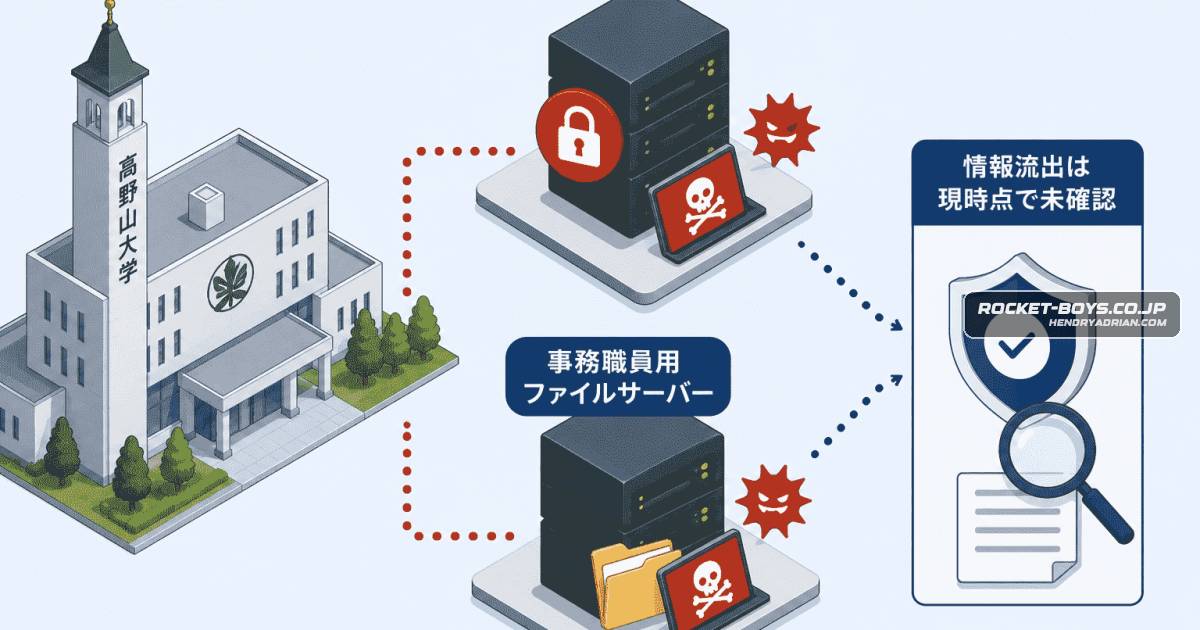
Koyasan University said ransomware affected its administrative Active Directory server and part of an administrative staff file server. No data leak has been confirmed; student and teaching systems remain unaffected.
Key points
- The university detected problems on some administrative servers on June 9, 2026, and an investigation identified a ransomware attack on June 26.
- The affected systems include an administrative Active Directory server and part of a file server used by administrative staff.
- The university has isolated the affected servers and is investigating the scope of impact while preparing a secure recovery environment.
- As of July 22, the university had not confirmed external leakage of personal or confidential information.
- The student portal, learning support system, teaching and research networks, and associated activities were reported unaffected; administrative services continued.
- The university is rebuilding and strengthening the security of the administrative server identified as the intrusion starting point and is increasing network monitoring.
- The entry point, affected file scope, ransomware variant, and responsible group have not been disclosed.
Article Details
- Victim Organization
- 高野山大学
- Incident Type
- Ransomware infection affecting an Active Directory server and part of an administrative staff file server.
- Disclosure Date
- 2026-07-22
- Operational Impact
- Administrative servers were isolated from the network and are undergoing recovery and investigation. The student portal, teaching support system, lecture and research networks, educational and research activities, and counter services were reported unaffected or continued as usual.
- Ransom Or Extortion
- No ransom demand or extortion activity is reported. The ransomware type and attack group were not disclosed.
- Claim Status
- confirmed