
Kyushu Denshi Details Ransomware Attack on Taiwan Subsidiary
Summary
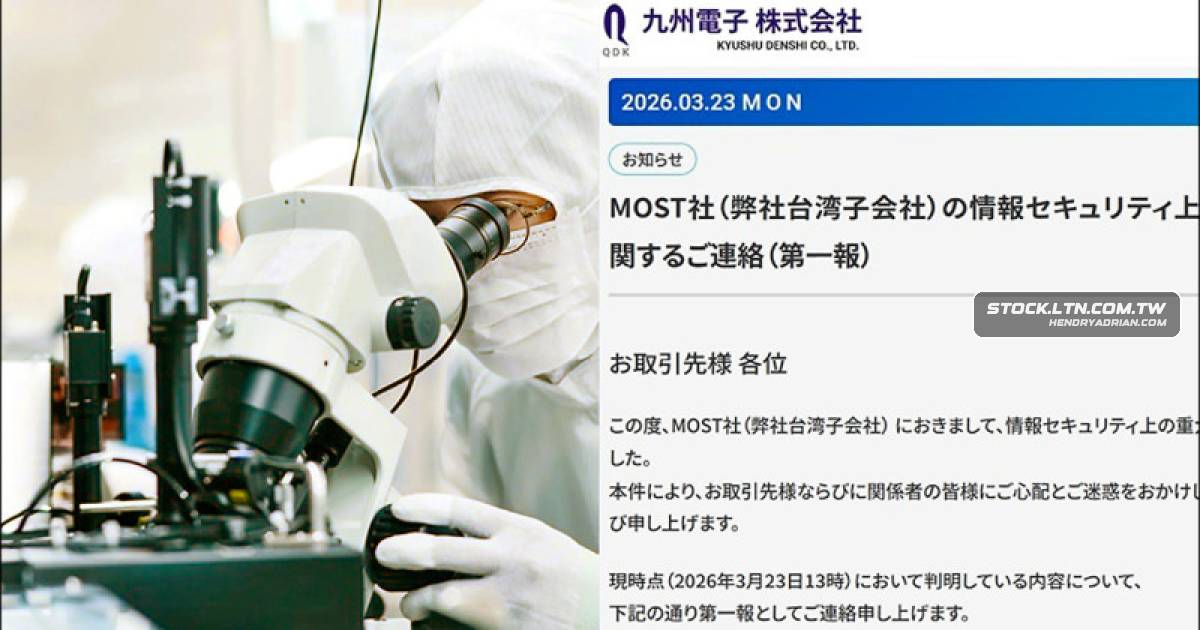
Kyushu Denshi reported that ransomware at its Taiwan subsidiary disrupted email, order processing and shipping. It said the attack did not spread to its Japan headquarters and that it detected no signs of data exfiltration.
Key points
- The company said unauthorized access to subsidiary MOST’s internal systems began on March 21 and was later confirmed as a ransomware attack.
- The incident affected email, order processing and shipping.
- Kyushu Denshi said the attack did not spread to its Japan headquarters and it detected no unusual communications indicating possible data leakage.
- The company isolated affected systems, investigated and later strengthened endpoint protection, account authentication and password management.
- A security expert speculated that email may have been the initial entry point, but the article does not report a confirmed access method.
- Kyushu Denshi disclosed the incident through three staged updates, which the article presents as an uncommon example of transparency in the region’s manufacturing sector.
Article Details
- Victim Organization
- MOST
- Incident Type
- Ransomware attack
- Incident Date
- 2026-03-21
- Operational Impact
- Email, order-taking, and shipping processes were affected. Kyushu Denshi reported no lateral spread to its Japan headquarters and no detected anomalous communications that could indicate data exfiltration.
- Ransom Or Extortion
- Not disclosed
- Claim Status
- confirmed