
BigBear 2.0 PhaaS Operation Targeted Organizations in More Than 40 Countries
Summary
CloudSEK identified a Microsoft 365 phishing operation targeting organizations in more than 40 countries. An infrastructure analysis linked its indicators to additional domains and IPs, while researchers caution that some flagged entities may be benign.
Key points
- CloudSEK reported that BigBear 2.0 targeted hundreds of organizations across more than 40 countries.
- The investigation exposed an attacker admin panel, an affiliate network, phishing infrastructure, and thousands of stolen credentials and session cookies.
- The operation used adversary-in-the-middle phishing to hijack sessions, including sessions authenticated with MFA.
- Researchers analyzed 38 network indicators and identified 1,048 additional email-connected domains; one was confirmed malicious.
- The researchers also identified eight additional IP addresses, four confirmed malicious, and found that 81 potentially victim-owned IPs communicated with 18 indicator IPs.
- The article says the findings are a snapshot of the full research and recommends further investigation because some entities labeled malicious may prove harmless.
Article Details
- Event Type
- Discovery of a global Microsoft 365 phishing-as-a-service operation dubbed “BigBear 2.0.”
- Impact
- The operation targeted hundreds of organizations across 40+ countries. Researchers reported thousands of stolen credentials and session cookies, and described AiTM attacks capable of hijacking sessions despite MFA.
Indicators of compromise
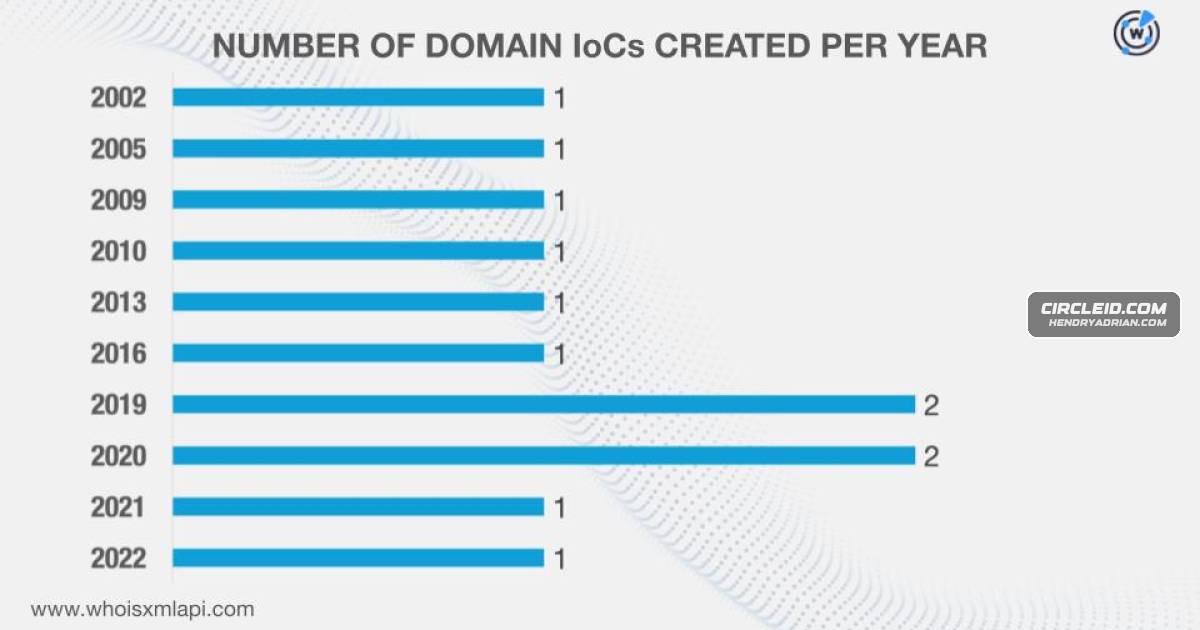
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | futureoneenterprises[.]com | The article reports that this domain had figured in phishing campaigns observed on 22 July 2026. |
| DOMAIN | haliotisbar[.]com | Listed as a BigBear 2.0 domain IOC. |
| DOMAIN | kgsscans[.]com | Listed as a BigBear 2.0 domain IOC. |
| DOMAIN | konceptenterprises[.]com | Listed as a BigBear 2.0 domain IOC. |
| DOMAIN | michaelmarcotte[.]com | Listed as a BigBear 2.0 domain IOC and as the apex domain associated with suspicious campaign subdomains. |
| DOMAIN | planisteradmin[.]com | Listed as a BigBear 2.0 domain IOC. |
| HOSTNAME | management[.]michaelmarcotte[.]com | Identified as the sole subdomain IOC; researchers said it resembled infrastructure associated with credential phishing or fake admin-panel staging. |
| IPV4 | 107[.]191[.]46[.]14 | Listed as a BigBear 2.0 IP IOC. |
| IPV4 | 199[.]247[.]10[.]14 | Listed as a BigBear 2.0 IP IOC. |
| IPV4 | 65[.]20[.]103[.]58 | Listed as a BigBear 2.0 IP IOC. |
| IPV4 | 70[.]34[.]244[.]122 | Listed as a BigBear 2.0 IP IOC. |
| IPV4 | 95[.]179[.]233[.]79 | Listed as a BigBear 2.0 IP IOC. |