
Marutaka Kogyo Reports VPN-Intrusion Ransomware Attack and Possible Exposure of 1.5 GB of Data
Summary
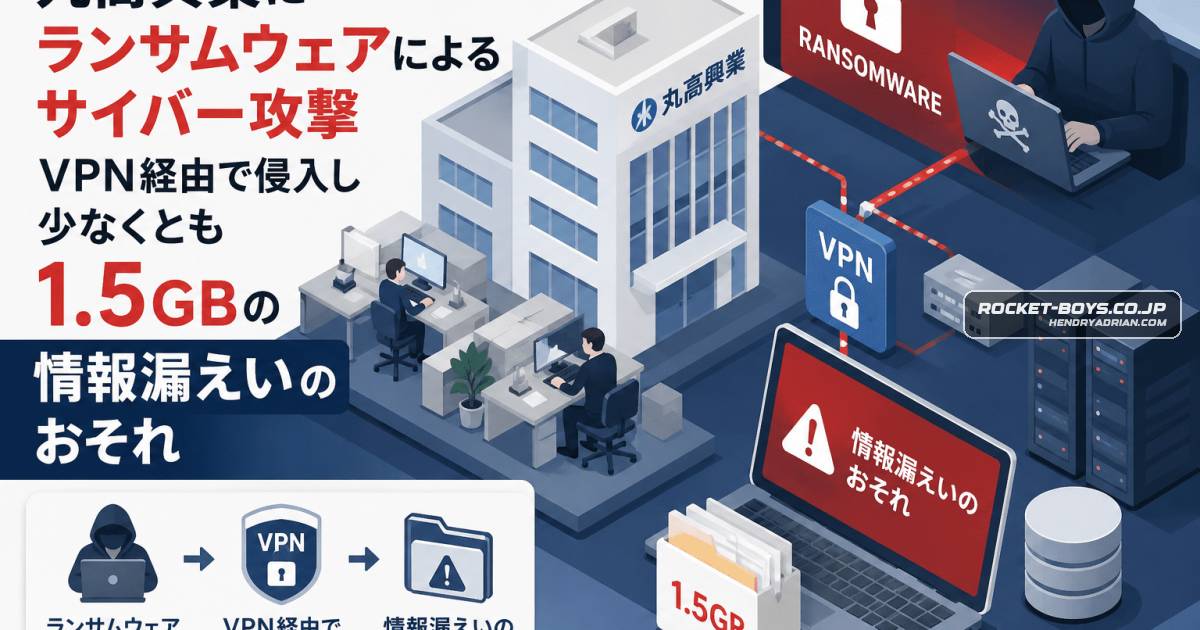
Marutaka Kogyo says attackers entered via VPN, created an unauthorized administrator account, encrypted server data and deleted some logs. Forensics found at least 1.5 GB may have leaked; actual exfiltration remains unconfirmed.
Key points
- The company disclosed findings on July 29, 2026, about an attack discovered on March 11.
- Investigators confirmed intrusion through a VPN device and access to multiple servers using an unauthorized administrator account.
- Attackers encrypted server data and deleted some system logs, limiting investigators’ ability to determine what was accessed or removed.
- Forensics indicated at least 1.5 GB of data may have been exposed; actual external transfer and misuse have not been confirmed.
- Potentially affected data included business and contact details, addresses, phone numbers, email addresses, and order histories. The number of affected people was not disclosed.
- Marutaka Kogyo replaced VPN equipment and PCs, rebuilt its network, reset accounts and passwords, and moved its sales management system and data to the cloud.
- The VPN product, exploited vulnerability, compromised credentials, and attacker identity have not been disclosed.
Article Details
- Victim Organization
- 丸高興業株式会社
- Incident Type
- Ransomware attack involving VPN-mediated network intrusion, creation of an unauthorized administrator account, access to multiple servers, data encryption, and deletion of some system logs.
- Incident Date
- 2026-03-11
- Disclosure Date
- 2026-07-29
- Data Types Exposed
- Company names
- Department names
- Contact names
- Addresses, including delivery and direct-shipment addresses
- Telephone numbers
- Fax numbers
- Email addresses
- Order and transaction histories
- Other information registered in the sales management system
- Affected Records
- Not disclosed
- Affected Data Size
- At least 1.5 GB may have been exposed; confirmed external transfer was not established.
- Operational Impact
- Data on multiple servers was encrypted, and some system logs were deleted. The initial disclosure reported possible delays to order processing and inquiry handling. The company isolated affected servers, rebuilt its internal network, replaced all company PCs and the VPN equipment, reset accounts, and migrated its sales management system and data to the cloud.
- Ransom Or Extortion
- No ransom demand, leak-site listing, or sample-data publication was reported.
- Claim Status
- confirmed