Plex2Shell Exploitation Deploys Crypto Miners and a Linux Proxy Backdoor
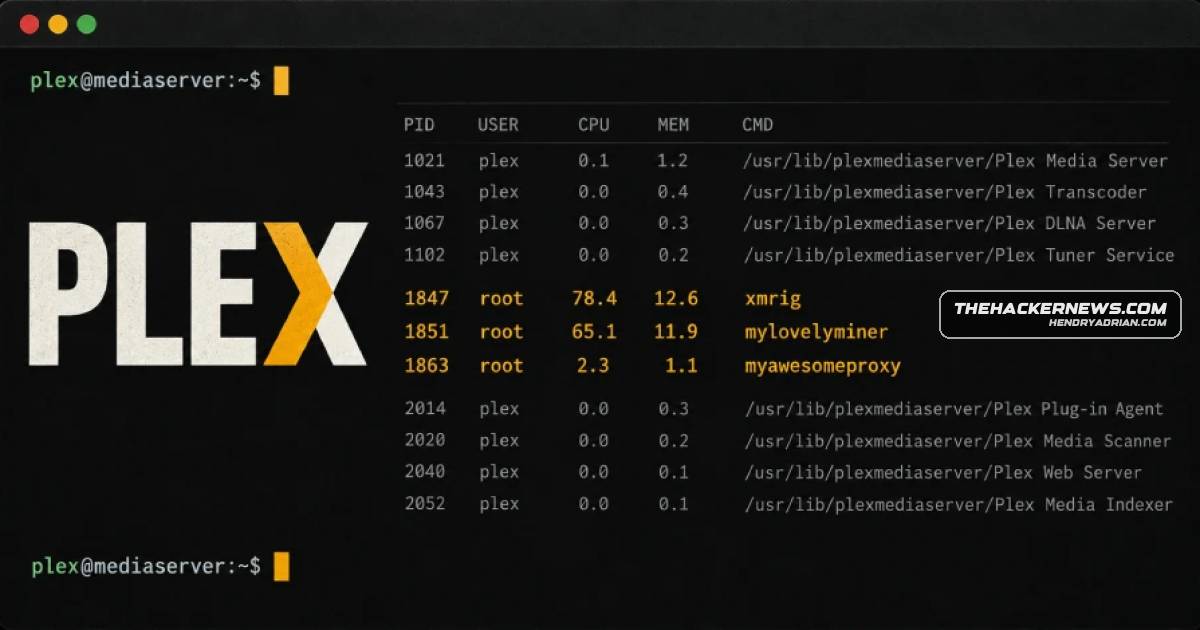
Summary
Attackers reportedly exploited the Plex2Shell vulnerability chain to deploy a crypto miner and Linux proxy backdoor. Plex patched the flaws in August; exploitation attempts were observed after technical details went public in October.
Key points
- The Plex2Shell chain reportedly combines four vulnerabilities to achieve unauthenticated remote code execution on susceptible Plex Media Server instances.
- Plex patched the vulnerabilities in Media Server 1.43.3.10861, released August 3, 2026.
- Exploitation attempts were recorded October 16, 2026, a day after technical details became public.
- Observed payloads included a cryptocurrency miner and a Linux backdoor/reverse proxy named "myawesomeproxy."
- The XMRig miner, identified as "mylovelyminer," used ota[.]proxystream[.]st as its mining server.
- Reddit users reported instances compromised with the same miner, but the article says it is unclear whether those cases involved Plex2Shell.
- Users are advised to update Plex installations; the article says it is unclear whether these flaws were included in an earlier Plex security alert.
Article Details
- Event Type
- Active exploitation of Plex2Shell vulnerabilities in Plex Media Server to deploy cryptocurrency-mining and Linux reverse-proxy/backdoor payloads.
- Impact
- Susceptible Plex Media Server instances were compromised, with attacks deploying a cryptocurrency miner and a Linux backdoor/reverse proxy. The article reports that the vulnerabilities were patched in Plex Media Server 1.43.3.10861; the extent of compromise is unknown.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| HOSTNAME | global[.]relay[.]proxystream[.]st | Subdomain flagged by Bitsight in connection with the AISURU DDoS and proxyware botnet. |
| HOSTNAME | ota[.]proxystream[.]st | Mining server specified by the deployed XMRig miner. |
| IPV4 | 217[.]60[.]194[.]116 | Remote server from which attackers delivered a cryptocurrency-miner payload. |
MITRE ATT&CK
CVE
People
Malware
myawesomeproxyFurthermore, the vulnerabilities have been exploited to deliver an artifact named "myawesomeproxy," which, according to VirusTotal, is a stealthy Linux backdoor and reverse proxy. Running the program displays the belowmylovelyminerAlso deployed concurrently is an XMRig miner process identified as "mylovelyminer" with its mining server pointing to "ota.proxystream[.]st." Notably, another subdomain associated with the same domain,