
Gig Works Says Intruder May Have Been Able to View Personal Data
Summary
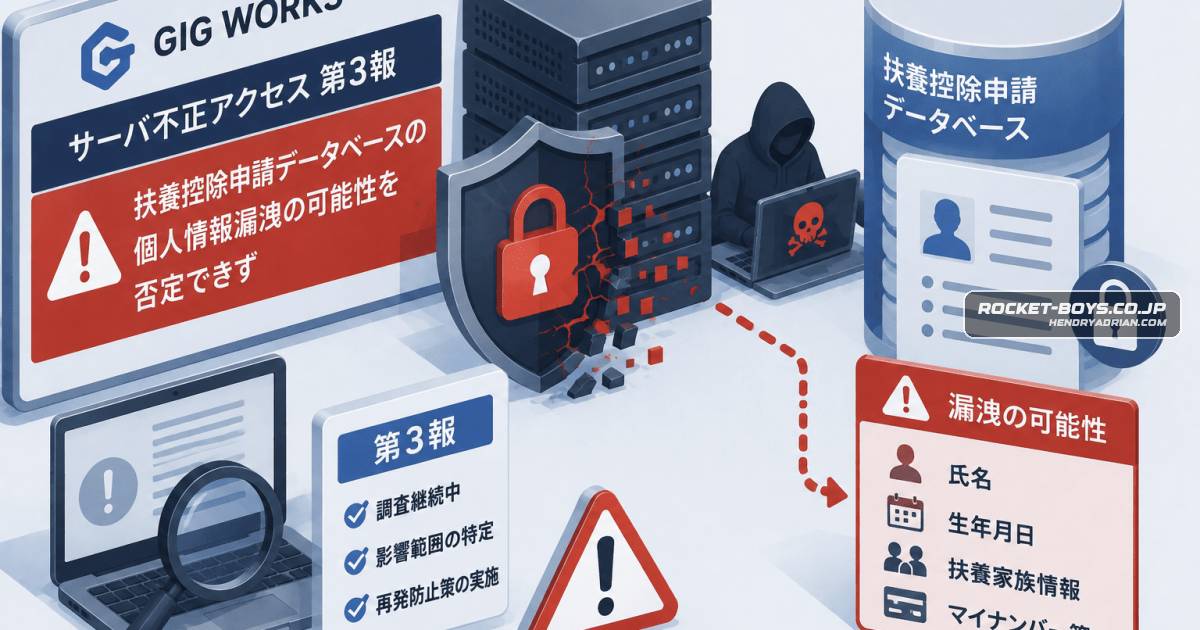
Gig Works says investigators found no evidence that personal data files were removed, but cannot rule out brief viewing of records in a dependent-deduction database. It is notifying potentially affected people and has strengthened security.
Key points
- Gig Works disclosed its third update on August 10, 2026, about unauthorized access first identified on December 19, 2025.
- A forensic investigation found no traces of personal-data files being taken externally or written to external media.
- The company cannot rule out that an attacker briefly could view data in the dependent-deduction application database.
- Potentially exposed data includes names, contact details, birth dates, salary and tax information, dependent-allowance application details, and bank account information.
- The number of potentially affected people is not stated; Gig Works says it will contact them in sequence. No related misuse of personal information has been identified so far.
- The company says it isolated affected servers, introduced abnormal-access detection, strengthened device monitoring, reviewed access permissions and authentication, and is consulting security specialists.
Article Details
- Victim Organization
- ギグワークス株式会社
- Incident Type
- Unauthorized access to company servers, including a dependent deduction application database server; possible brief visual access to personal information cannot be ruled out.
- Incident Date
- 2025-12-19
- Disclosure Date
- 2026-08-10
- Data Types Exposed
- Names
- Addresses
- Telephone numbers
- Email addresses
- Dates of birth
- Salary and tax-related information
- Dependent deduction application information
- Bank account information
- Affected Records
- Not disclosed
- Affected Data Size
- Not disclosed
- Operational Impact
- Affected servers were isolated from the network. The company reports implementing abnormal-access detection, strengthening equipment monitoring, reviewing access permissions and authentication methods, and working with security specialists. No misuse of personal information attributable to the incident has been identified.
- Ransom Or Extortion
- None reported
- Claim Status
- unknown