
Spaggiari Confirms June Intrusion Affecting School Forms Service; Ransomware Claims Disputed
Summary
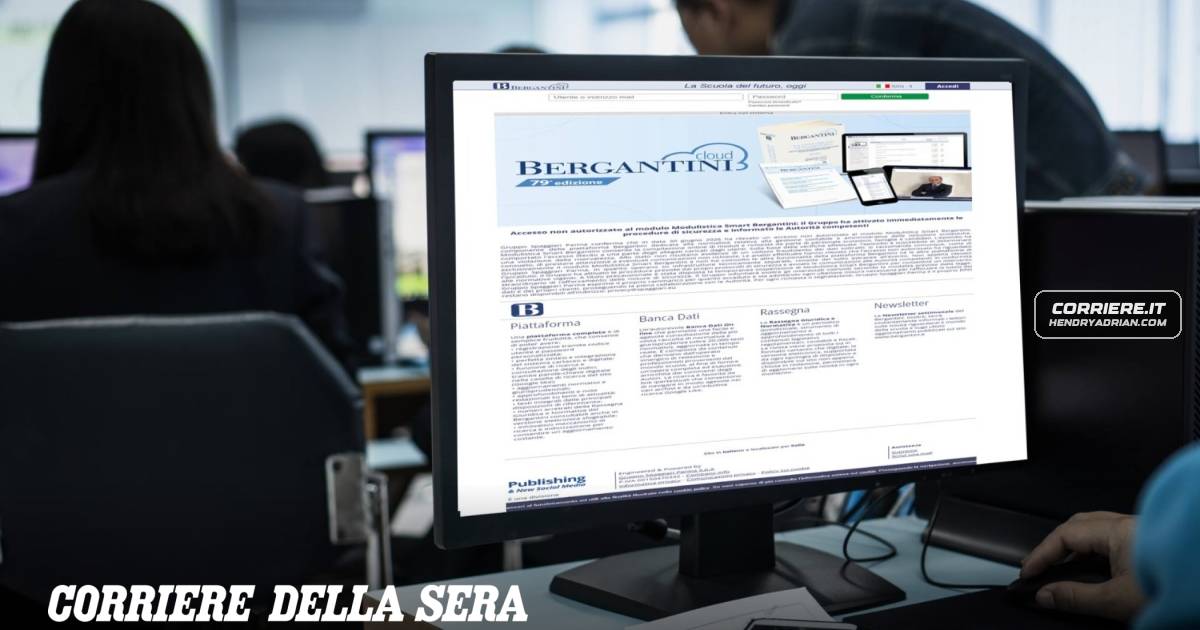
Spaggiari says a June 30 intrusion exposed some attachments uploaded to its Bergantini forms service. The ClasseViva register was unaffected; a cybercrime group’s ransomware and 6.1 TB theft claims are disputed.
Key points
- Spaggiari says the incident occurred on June 30 and affected Modulistica Smart, a component of its Bergantini platform—not the ClasseViva register or other school-management systems.
- The company reports unauthorized access to some user-uploaded attachments and says the incident may have breached confidentiality.
- The xplOitrs group claimed responsibility on August 20. Reports of ransomware, a 6.1 TB theft and an extortion deadline were not confirmed; the group reportedly disputed the scale and extortion claims.
- No sample of the allegedly stolen material had been published, and Spaggiari said it had found no evidence of fraudulent use of the data.
- Spaggiari notified Italy’s data-protection authority and cybersecurity agency and reported the incident to law enforcement.
- The forms service was suspended for checks and improvements. The company advised users to change their credentials and watch for unsolicited communications.
Article Details
- Victim Organization
- Gruppo Spaggiari Parma S.p.A.
- Incident Type
- Unauthorized access to some user-uploaded attachments in the Modulistica Smart component of the Bergantini platform. The company said the electronic class register and its other school-management systems were not affected.
- Incident Date
- 2026-06-30
- Disclosure Date
- 2026-08-21
- Data Types Exposed
- Some attachments uploaded by users to online forms and requests; their contents are not specified by the company.
- Cyber-intelligence sources reportedly alleged that the stolen material included identity documents, contact and personal information, and student medical information; these details were not confirmed by the company.
- Affected Records
- Not disclosed
- Affected Data Size
- Cyber-intelligence sources reported a claim of 6.1 TB, but the amount was disputed and not confirmed; no sample was released.
- Operational Impact
- Modulistica Smart was suspended for checks and improvements. The company said its other services remained operational and the electronic class register was not affected.
- Ransom Or Extortion
- Some reports alleged a ransom demand and an ultimatum reportedly expiring around 2026-08-27. The group’s account reportedly denied the claimed theft volume and that the group engaged in extortion; the company did not confirm a ransom demand.
- Claim Status
- confirmed
Threat Actors
Vendors
Products
BergantiniL'azienda, che è titolare del registro elettronico più usato in Italia, ClasseViva, specifica: «Evento noto, risale al 30 giugno, ed è limitato al software Bergantini per i moduli.ClasseVivaL'azienda, che è titolare del registro elettronico più usato in Italia, ClasseViva, specifica: «Evento noto, risale al 30 giugno, ed è limitato al software Bergantini per i moduli.Modulistica Smartil focus sulle modalità dell’attacco e i dati sottratti: «Il perimetro interessato è il componente Modulistica Smart della piattaforma Bergantini, utilizzato per la compilazione e la trasmissione online di moduli e