
Audit Flags Cybersecurity Gaps After Ransomware Disrupted Punjab Cancer Centre
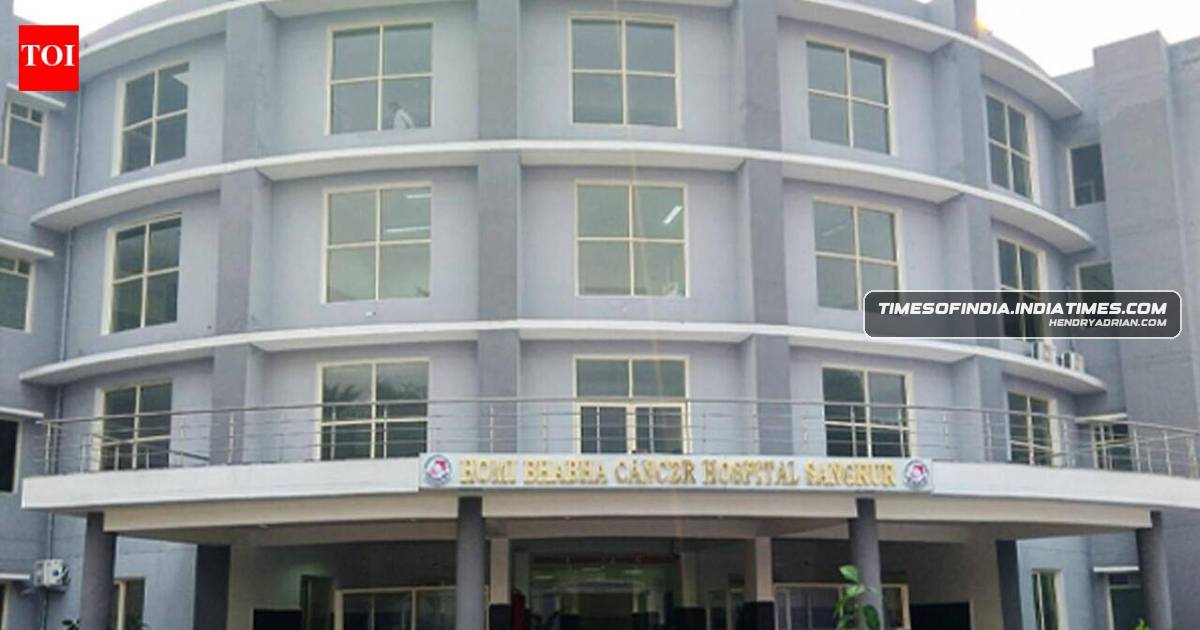
Summary
A Dec. 2024 Interlock ransomware incident disrupted IT systems at Homi Bhabha Cancer Hospital Research Centre. A CAG audit flagged the absence of root-cause analysis and recurrence-prevention measures; about 95% of services were restored by Dec. 12.
Key points
- The hospital experienced an Interlock ransomware incident on Dec. 2, 2024, and its computer systems stopped functioning.
- The incident was escalated to local authorities and the Computer and Information Security Advisory Group on the day it was discovered.
- About 95% of IT services had been restored by Dec. 12, 2024; the remaining 5% was still being restored.
- The centre told auditors that it had not conducted a root-cause analysis or implemented measures to prevent recurrence; the actual cause was not identified.
- In June 2025, the centre said its response time and root-cause analysis protocols needed improvement and that security measures, including MFA, were being provisioned.
- CAG recommended stronger password management, MFA, current security patches, and regular monitoring of IT security processes.
Article Details
- Victim Organization
- Homi Bhabha Cancer Hospital Research Centre
- Incident Type
- Ransomware attack that disrupted the hospital's IT systems
- Incident Date
- 2024-12-02
- Data Types Exposed
- Highly sensitive information, according to the ransomware pop-up message; specific data types were not reported
- Operational Impact
- Computer systems stopped functioning. Approximately 95% of IT services had been restored by 2024-12-12; the remaining 5% was still to be restored.
- Ransom Or Extortion
- The ransomware pop-up claimed that highly sensitive information had been compromised and possessed, and warned of consequences without immediate action. No specific ransom demand or payment was reported.
- Claim Status
- confirmed