Microsoft-led operation disrupts EvilTokens phishing service that compromised over 12,000 inboxes
Summary
Microsoft and partner organizations disrupted EvilTokens, a phishing service that compromised more than 12,000 inboxes across over 10,000 organizations. The service used an AI chatbot to analyze mailbox contents and help plan fraud. Authorities arrested two men on suspicion of involvement; both were released on bail while the investigation continues.
Key points
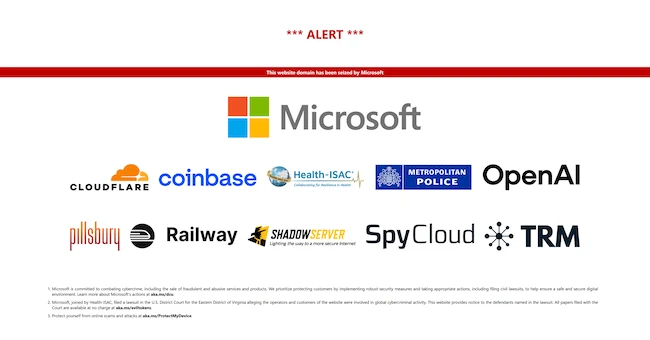
- With authorization from the US District Court for the Eastern District of Virginia, Microsoft and partners seized 50 websites and disabled more than 150 domains tied to EvilTokens.
- Victims were tricked into entering authentication codes on Microsoft’s legitimate sign-in page, giving criminals account access without victims revealing their passwords.
- The service’s AI chatbot could summarize and translate emails, identify financial conversations and trusted contacts, and help draft impersonation messages.
- Microsoft said access could persist after a password reset unless associated sessions and tokens were also revoked.
- Microsoft notified affected customers, helped remediate compromised accounts, and shared intelligence for further investigation.
- On September 11, 2026, London police arrested two men, aged 32 and 38, on suspicion of offenses connected to the alleged operation; both were released on bail while the investigation continues.
- Microsoft said the infrastructure had been disrupted but warned that the model of combining compromised accounts and AI-assisted analysis could continue.
Tags
PhishingEmail Account CompromiseAI-Assisted CybercrimeFinancial FraudLaw Enforcement Disruption