
Mistertemp' Group Confirms Unauthorized Access to Personal Data
Summary
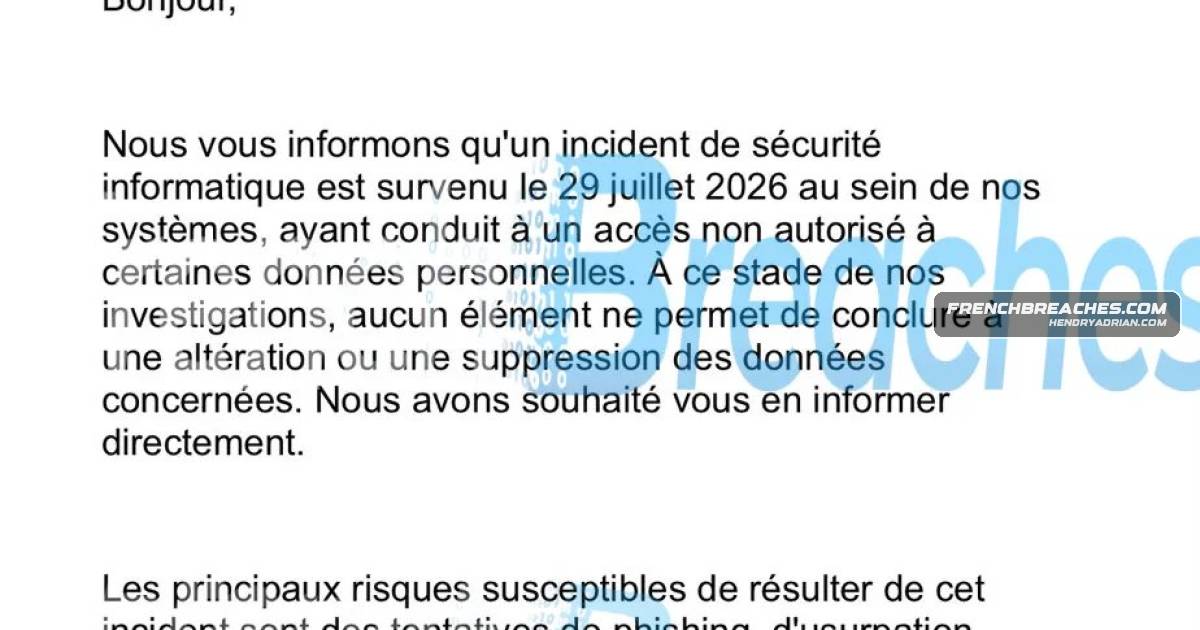
Mistertemp' group says unauthorized access on July 29, 2026, may have exposed names, contact details and nationality. It reports no affected passwords or banking data, has fixed the vulnerability, and continues investigating.
Key points
- Mistertemp' group says the incident occurred in its systems on July 29, 2026; the number of affected people and duration of access remain unknown.
- Data that may have been accessed includes names, email addresses, phone numbers and nationality.
- The company says banking data, passwords and identity documents were not affected; it has found no evidence of data alteration or deletion.
- Mistertemp' warns of possible phishing, limited identity misuse and fraudulent solicitation, but says it had identified no fraudulent use of the data at the time of its notification.
- The group says it contained the incident, fixed the vulnerability, strengthened monitoring and is continuing technical investigations with specialists.
- Mistertemp' says it notified France's CNIL and filed a criminal complaint.
Article Details
- Victim Organization
- Mistertemp' group
- Incident Type
- Unauthorized access to personal data following a cybersecurity incident; the technical origin was not specified.
- Incident Date
- 2026-07-29
- Data Types Exposed
- Names
- First names
- Email addresses
- Phone numbers
- Nationality
- Affected Records
- Not disclosed
- Affected Data Size
- Not disclosed
- Operational Impact
- The incident was contained, the identified vulnerability was corrected, and system monitoring was strengthened. The source reports no evidence at that stage of data alteration or deletion. Investigations remained ongoing.
- Ransom Or Extortion
- None reported
- Claim Status
- confirmed