
Hack of Daniel’s Hosting Took More Than 7,500 Tor Services Offline
Summary
A March 10, 2020 hack of Daniel Winzen’s Tor hosting service took more than 7,500 hidden services offline. Winzen said attackers deleted its databases and advised users to treat data as leaked and passwords as compromised.
Key points
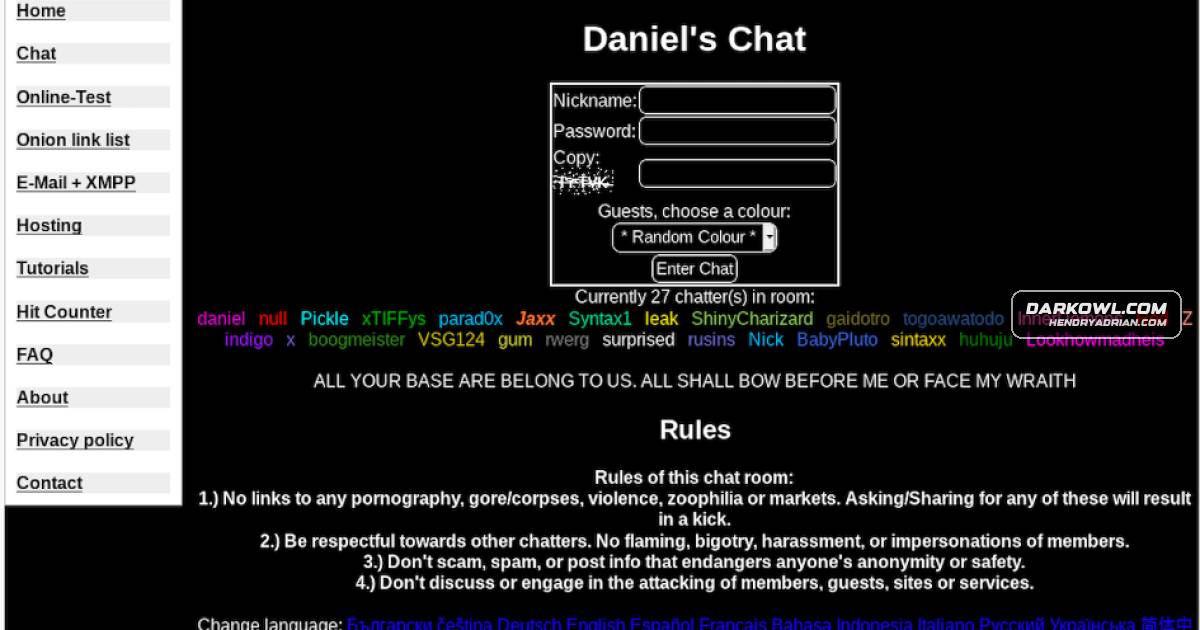
- On March 10, attackers took control of Daniel’s chat administrator account, removed users and staff, and the chat later displayed a database connection error.
- A chat user said Daniel’s administrator password had been brute-forced, reportedly based on confirmation obtained through Daniel’s friend; the article does not independently establish the method.
- Winzen announced that attackers deleted the hosting platform’s databases and told users to consider their data leaked and passwords compromised. The article reports that database backups were unavailable.
- DarkOwl recorded 9,006 domains or subdomains associated with the hosting service as of March 9, 2020; 7,555 were recorded as online during the first two weeks of March.
- By April 1, DarkOwl had identified about 1,200 associated hidden services as back or still online. Winzen said he did not intend to restart the hosting project at that time.
- The attackers’ identities were not established. The article describes proposed links to Kiwi Farms as extremely weak and circumstantial, and GhostSec did not claim responsibility.
Article Details
- Victim Organization
- Daniel's Hosting
- Incident Type
- Unauthorized takeover of Daniel's Chat administrator account, followed by deletion of hosting-related databases and disruption of hosted services.
- Incident Date
- 2020-03-10
- Data Types Exposed
- User data
- Passwords
- SQL database contents
- Operational Impact
- Daniel stated that the hosting platform's databases had been deleted and advised users to consider their data leaked and passwords compromised. More than 7,500 hidden services were recorded as online during the first two weeks of March and were subsequently taken offline; the article does not establish that all were permanently lost.
- Ransom Or Extortion
- None reported.
- Claim Status
- confirmed
MITRE ATT&CK
People
Daniel WinzenOperator of Daniel's Hosting and the account owner whose administrator password was reportedly brute-forced.Sebastian Dante AlexanderIdentified in the article as the person using the moniker Sebastian and as the leader of GhostSec; the article does not attribute the March 10 attack to him.
Threat Actors
@nullMoniker of the person who took control of Daniel's Chat during the incident and claimed to have downloaded chat data; their identity and the full scope of access were not established.@PickleGuest account promoted to administrator during the incident and characterized by the article as an accomplice; identity and precise role were not established.GhostSecNamed in a March 3 warning in Daniel's Chat; the user Sebastian claimed the group had taken control of Daniel's Discord servers. The article says GhostSec did not claim responsibility for the March 10 attack.