
Twitch Browser Extension Exposes OAuth Tokens for 30,000+ Users
Summary
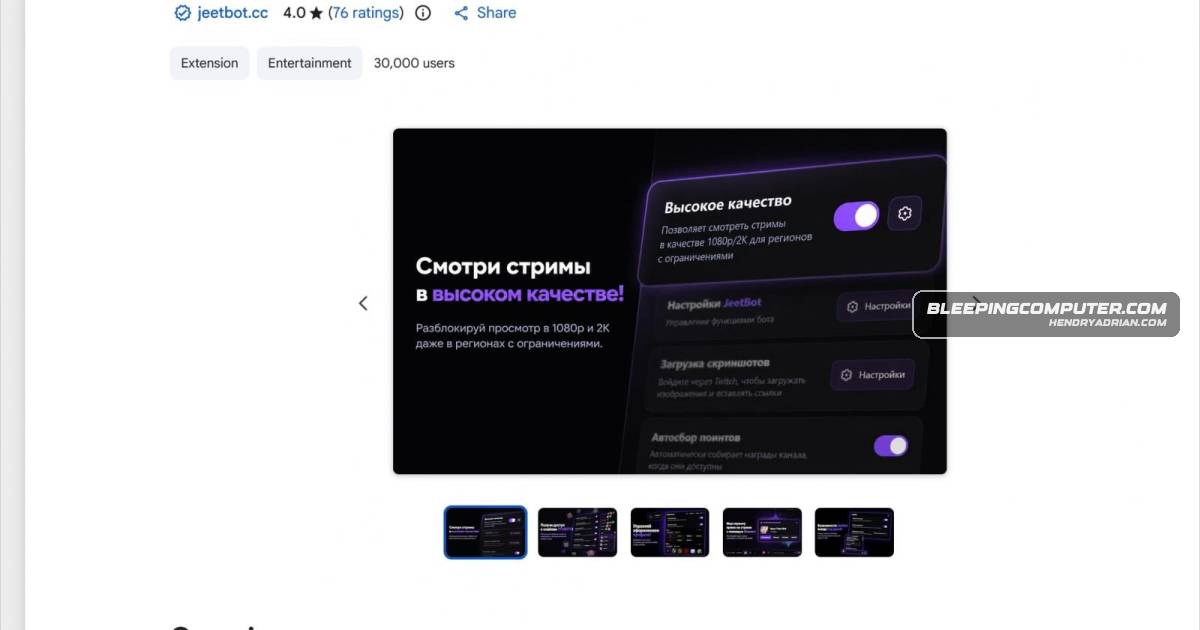
Socket says the Twitch Enhanced Viewer | JeetBot extension sends users’ OAuth tokens through JeetBot-operated proxies, where they are logged in cleartext. It had over 30,000 installs; users were advised to remove it and re-authenticate.
Key points
- The extension was available in the official Chrome and Firefox stores and had more than 30,000 installs.
- Socket found that it extracts Twitch OAuth tokens from authorization headers and sends them through JeetBot-operated proxy servers.
- In current versions, tokens are added as an auth= URL parameter to redirected video playlist requests, exposing them in proxy request logs.
- The behavior reportedly applies to every Twitch channel watched except ten Russian-language channels hardcoded into the extension.
- Socket says earlier versions used more explicit token-transmission mechanisms; the Firefox listing reportedly acknowledged that previous behavior.
- At publication, the extension remained listed in both stores, and JeetBot had not responded to BleepingComputer’s inquiry.
- Socket advised users to remove the extension, disconnect Twitch sessions, and re-authenticate; developers were advised not to route authentication tokens through third-party servers.
Article Details
- Victim Organization
- Twitch users
- Incident Type
- Browser extension credential theft and OAuth token exposure
- Data Types Exposed
- Twitch OAuth session tokens
- Operational Impact
- Tokens from users watching Twitch channels are sent through proxy servers and logged in cleartext; users were advised to remove the extension, disconnect Twitch sessions, and re-authenticate.
- Claim Status
- confirmed