
DarkOwl Finds SolarWinds Vulnerability Listings and Product Files on the Darknet
Summary
DarkOwl reports finding SolarWinds vulnerability discussions and product files on darknet forums and unsecured FTP servers, with much of the activity dating to late 2019 and early 2020.
Key points
- DarkOwl says it found SolarWinds and Orion vulnerability and zero-day references across darknet marketplaces and forums.
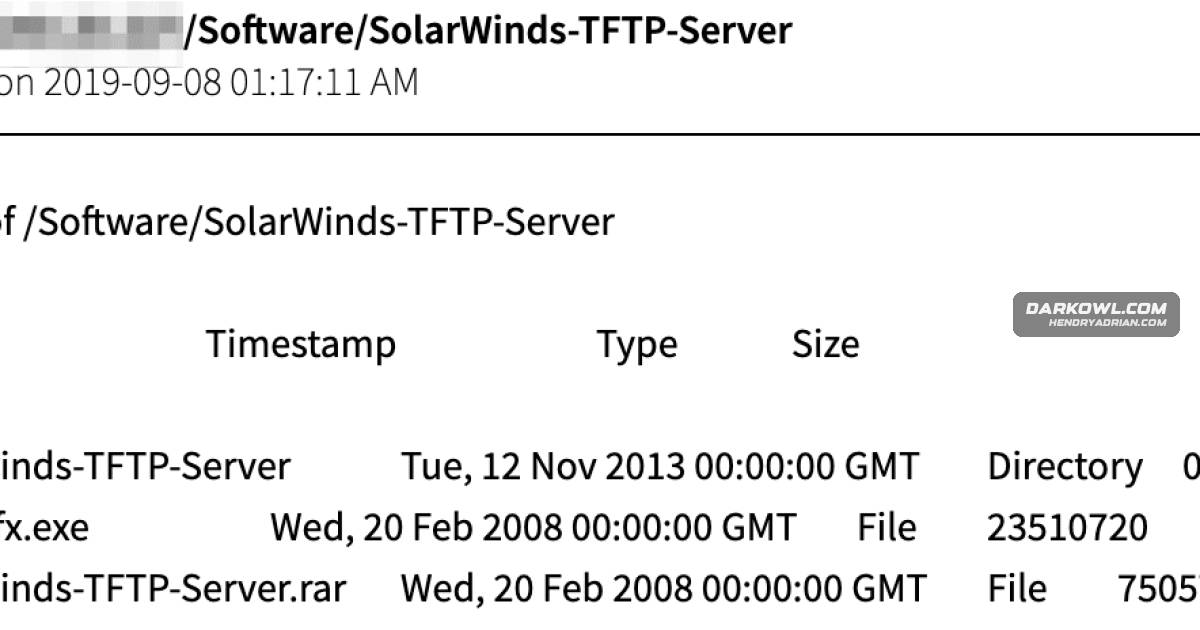
- The company reports collecting SolarWinds documentation and application executables from unsecured FTP servers in late 2019.
- DarkOwl traced the FTP servers’ IP address to Russian ISP Severen-Telecom.
- DarkOwl says one zero-day marketplace contained 98 documents mentioning SolarWinds vulnerabilities since February 2020.
- The article also notes forum interest in SolarWinds Security Event Manager and reports of cracked copies shared as recently as July 2020.
- DarkOwl cites a public report that SolarWinds credentials were exposed in a GitHub repository beginning in June 2018.
Article Details
- Event Type
- Darknet research report on SolarWinds-related vulnerabilities, leaked product files, and interest in SolarWinds exploits and software.
- Impact
- DarkOwl reported finding SolarWinds and Orion vulnerability and zero-day discussions on darknet marketplaces and forums, plus SolarWinds product documentation and executables on unsecured FTP servers collected in late 2019. The report says the servers also held Microsoft’s dotnetfx.exe and were traced to JSC “Severen-Telecom” in Saint Petersburg, Russia. It also cites cracked SolarWinds Security Event Manager software and a public GitHub repository reportedly exposing SolarWinds credentials. The report describes these findings as potential links and evidence of targeting; it does not establish that the FTP servers or credential exposure were part of the nation-state attack.
People
Vendors
Products
dotnetfx.exeThe FTP servers contained not only SolarWinds-specific server files, but also Microsoft’s dotnetfx.exe file, a critical executable for installing operating system updates.OrionWe uncovered an extensive amount of content containing SolarWinds and Orion-specific vulnerabilities and zero-days across darknet exploit marketplaces and discussion forums, many of which could be devastating ifSolarWinds Security Event Managersecurity applications and intrusion detection systems, with shares of ‘cracked’ versions of SolarWinds Security Event Manager application as recently as July 2020 (pictured below).