Placeholder Domain Used in Developer Docs Now Serves ClickFix Attacks
Summary
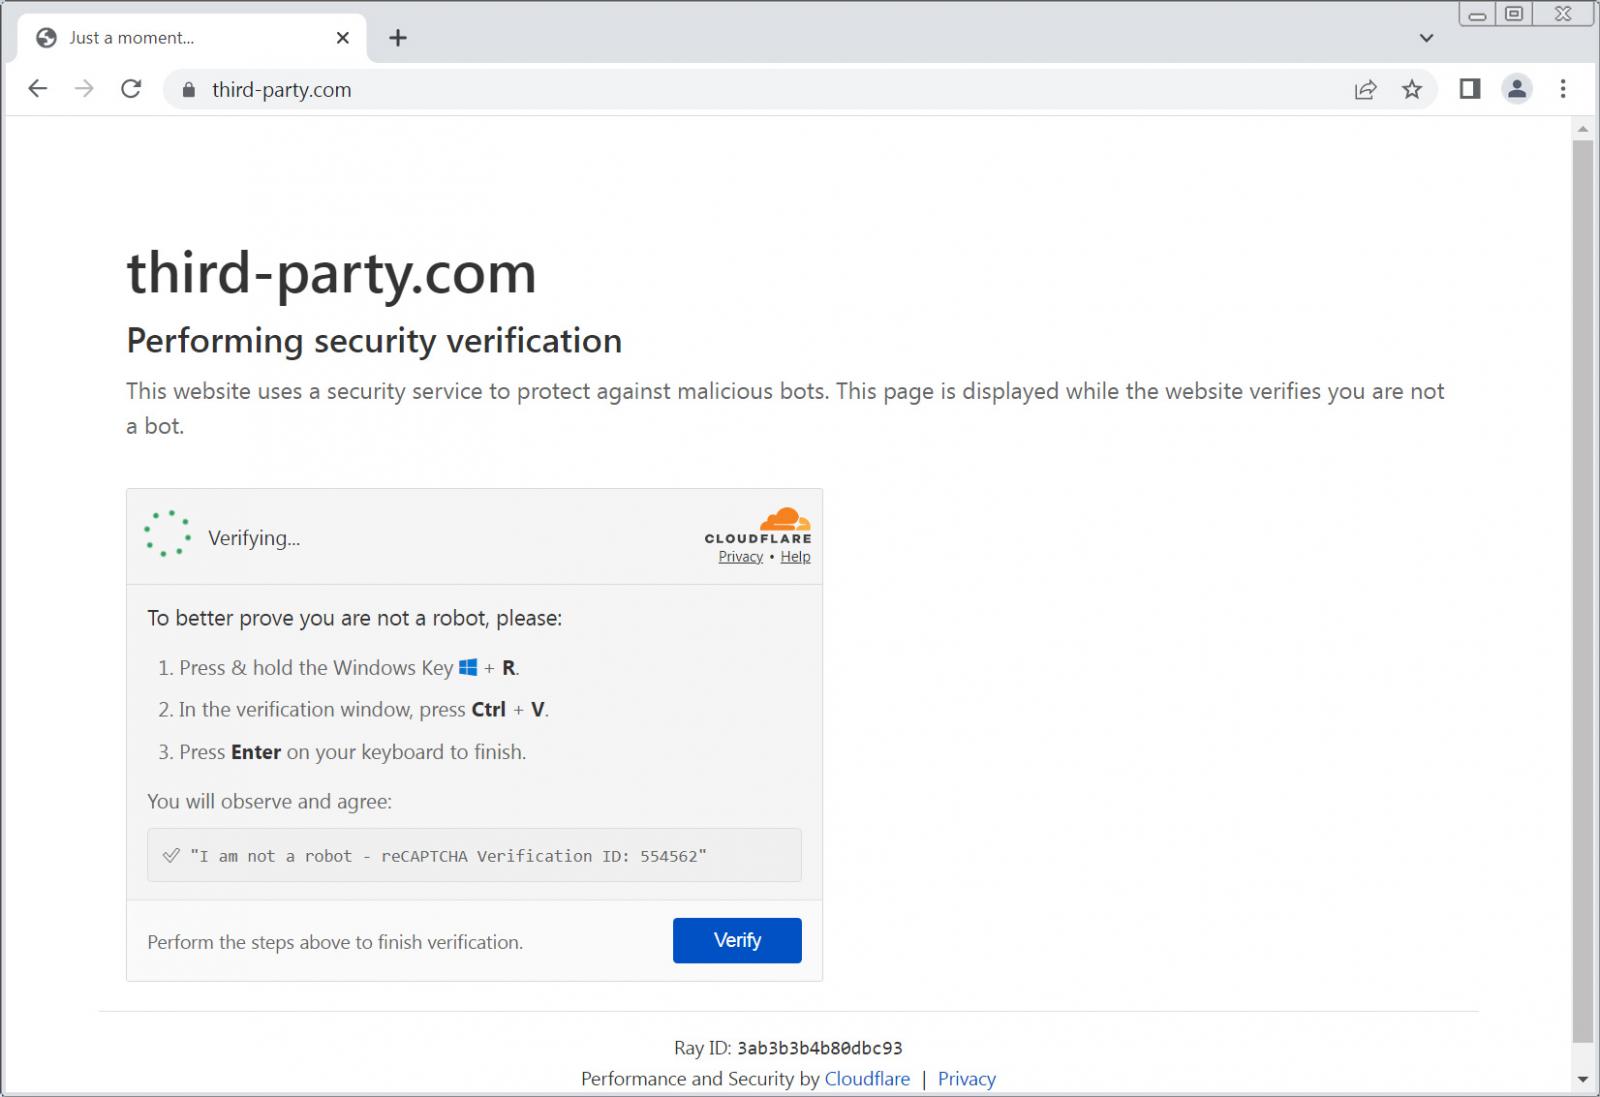
third-party.com, long used as a placeholder in developer documentation, is serving a fake Cloudflare verification page that targets Windows users with a ClickFix attack. The page copies a PowerShell command to the clipboard and instructs users to run it; the command downloads and executes a script. The payload host no longer resolved during BleepingComputer’s testing, and there are no reports that the attack has been executed through copied references.
Key points
- The real third-party.com domain is serving a fake Cloudflare verification page, despite its long use as a placeholder in developer documentation and code examples.
- Clicking the fake verification prompt copies a malicious PowerShell command to the clipboard and tells users to run it through the Windows Run dialog.
- The command reconstructs a URL to download and execute a PowerShell script; a Hybrid Analysis report showed the script downloading an archive and attempting to launch draw.io.exe.
- The attack targets Windows users; visitors using macOS or Linux are shown an unsupported-operating-system error instead of the payload instructions.
- The payload host no longer resolved when BleepingComputer tested it, and the referenced archive was unavailable, so the payload’s purpose could not be determined.
- There are no reports that copied third-party.com references have led to attacks on developers’ devices or applications; the domain remains live and could be used with a new payload.
- The domain was registered in 1996, but BleepingComputer could not determine when or how control of it changed.
Tags
ClickFixSocial EngineeringPowerShellWindowsMalicious DomainDeveloper Security
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | elxxvvx[.]xyz | Payload host used by the PowerShell command; it no longer resolved during BleepingComputer’s testing. |
| DOMAIN | third-party[.]com | Placeholder domain currently serving the fake Cloudflare verification page. |
| URL | hxxps[:]//elxxvvx[.]xyz/update2[.]zip | Archive URL the downloaded PowerShell script was configured to retrieve. |