How Stolen Cloud Keys and API Tokens Circulate in Criminal Markets
Summary
DarkOwl describes how cloud keys and API tokens are exposed in repositories or stolen by malware, then traded across darknet forums and Telegram. The article gives examples of offers and alleged uses, while noting some details are unclear.
Key points
- The article focuses on server-side credentials such as AWS and Azure keys, Django secret keys, and API tokens, rather than username-password combinations.
- Keys may be exposed in public code repositories or unprotected storage, then found through automated scanning.
- Infostealers can capture keys and session tokens from infected devices; the article also describes malware advertised as validating harvested AWS keys.
- DarkOwl observed key and cloud-access offers on darknet forums and Telegram, including an alleged $80,000 offer for AWS root keys tied to a U.S. company.
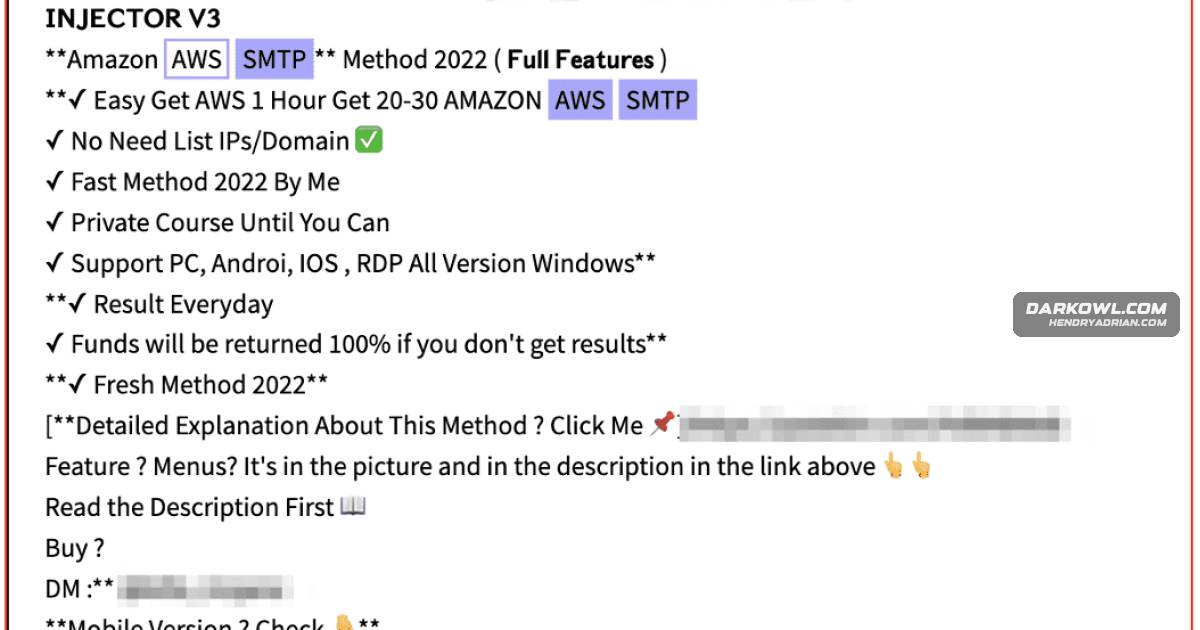
- Some offers are associated with claimed access to cloud panels or services; the article says the details of one advertised AWS method were unclear because it was not purchased.
Article Details
- Topic
- The darknet economy of server-side access credentials, including how keys and tokens are stolen, circulated, and sold.
Malware
EternityInfostealers such as Redline, Jester, and Eternity – often installed onto victim devices via malicious email campaigns – covertly log and exfiltrate sensitive data from the victim’s device to cause additional harm.Git ScannerFor reference, in early 2022, we observed another example of a “Git Scanner” malware is included from the exploit forum for $4K USD to $8K USD depending on the features of the software.JesterInfostealers such as Redline, Jester, and Eternity – often installed onto victim devices via malicious email campaigns – covertly log and exfiltrate sensitive data from the victim’s device to cause additional harm.Laravel MonsterDarkOwl identified malware called Laravel Monster that is advertised as an “all-in-one grabber” that exfiltrates AWS keys “and more” offered on a popular Russian-speaking forum.RedLineInfostealers such as Redline, Jester, and Eternity – often installed onto victim devices via malicious email campaigns – covertly log and exfiltrate sensitive data from the victim’s device to cause additional harm.TeamTNT_AWS_Stealersecurity researchers have identified similar information stealer malware in the wild, such as TeamTNT_AWS_Stealer that specifically targets virtual/cloud platforms to exfiltrate sensitive AWS keys on Kubernetes
Vendors
AmazonAmazon Web Service (AWS) Key Management Service (AWS KMS) Access Keys: ‘poweruser’ and administrator encryption keys for the managing Amazon-hosted services.GoogleGoogle Key Management System (KMS) Customer Managed Encryption Keys (CMEK): project-id’s and private keys for service accounts on the Google Cloud Platform (GCP)
Products
AWSIn this blog, we review how sensitive, server-side access credential data – such as AWS private/secret keys, Django secret keys, and API tokens – are captured, circulated, and sold across darknet marketplaces andAzure Key VaultAzure Keys & Secrets: Credential data stored inside Azure Key Vault (KV). Data includes database connection strings, account keys, passwords, and JSON Web keys.Djangothis blog, we review how sensitive, server-side access credential data – such as AWS private/secret keys, Django secret keys, and API tokens – are captured, circulated, and sold across darknet marketplaces and criminalDockerthat specifically targets virtual/cloud platforms to exfiltrate sensitive AWS keys on Kubernetes and Docker clusters adjacent to the compromised container.GitHubCommercial application developers have been guilty of copying and pasting keys in organizational Github repositories that are publicly accessible via automated web scrapers.GitLabSome threat actors offer zero-days on malware-centric Telegram channels and darknet discussion forums that facilitate the scanning of Gitlab and Github.Google Cloud PlatformGoogle Key Management System (KMS) Customer Managed Encryption Keys (CMEK): project-id’s and private keys for service accounts on the Google Cloud Platform (GCP)Kubernetesthat specifically targets virtual/cloud platforms to exfiltrate sensitive AWS keys on Kubernetes and Docker clusters adjacent to the compromised container.