
Huntress ITDR Adds Cloud and On-Premises Disablement for Synced Identities
Summary
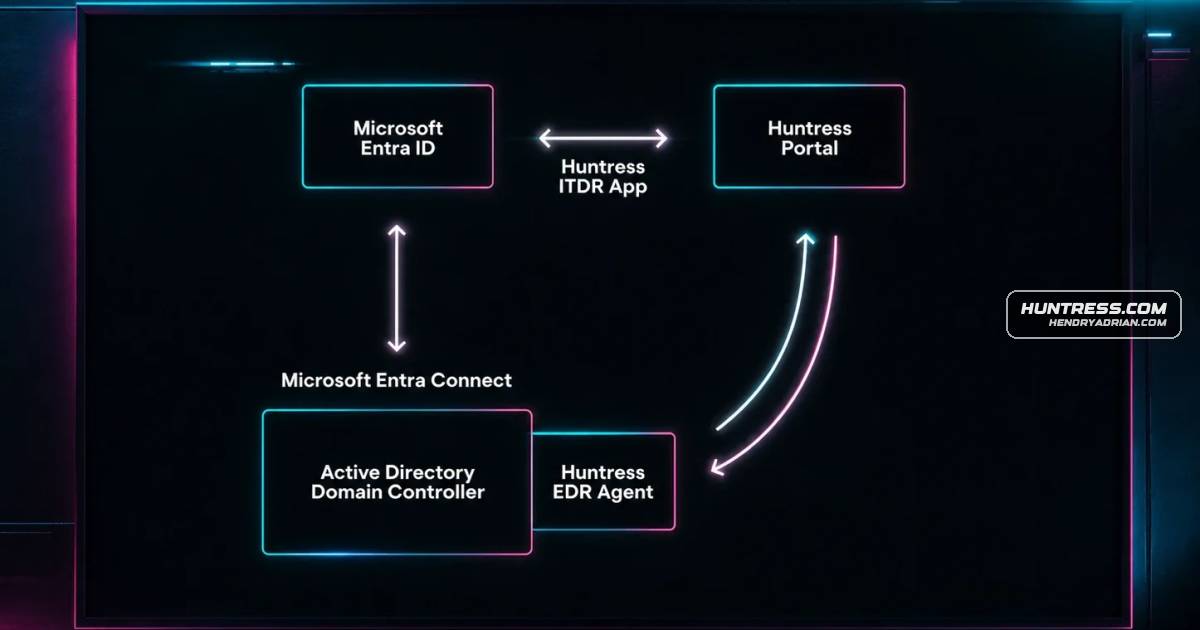
Huntress Managed ITDR can now disable and re-enable AD-synced identities in Microsoft 365 and on-premises Active Directory through an agent on domain controllers, preventing directory sync from re-enabling compromised accounts.
Key points
- The feature is available to organizations running Huntress agent v0.14.22 or later on domain controllers.
- Huntress says cloud-only disablement could be reversed by on-premises Active Directory synchronization, leaving compromised credentials usable.
- The service can perform automatic, analyst-driven, partner-triggered, and manual portal disablement; it also supports re-enablement.
- Partners receive an escalation message if an attempt fails because agents are missing or misconfigured.
- Disabling a synced identity cuts off the user from AD-integrated systems; identity exclusion features can provide exceptions.
Article Details
- Event Type
- Product capability announcement: Huntress Managed ITDR added identity disablement and re-enablement for Active Directory-synced identities.
- Impact
- The feature enables simultaneous disablement at cloud and on-premises Active Directory layers through the Huntress agent, helping prevent synchronization from re-enabling a compromised identity and supporting containment. It is available for organizations running Huntress agent v0.14.22 or later on domain controllers. Disabling an identity cuts off access to AD-integrated systems.
Vendors
Products
Huntress Managed ITDRWe’re excited to announce that one of the most requested features for Huntress Managed ITDR is now live: identity disablement and re-enablement for Active Directory (AD) synced identities, also known as hybridMicrosoft 365 Apps for EnterpriseThis update closes a significant gap in our containment and remediation capabilities—and it brings protection parity to the 47%+ of identities using AD sync in their Microsoft 365 configurations.Microsoft Active DirectoryHomeBlogClosing the Gap: Managed ITDR Now Supports Identity Disablement for Active Directory Synced IdentitiesMicrosoft Entra ConnectBut for organizations using Microsoft Entra Connect, disabling a cloud identity wasn’t enough.