
AuditTeam Claims Ransomware Attack Disrupted Ukraine’s Wise IT
Summary
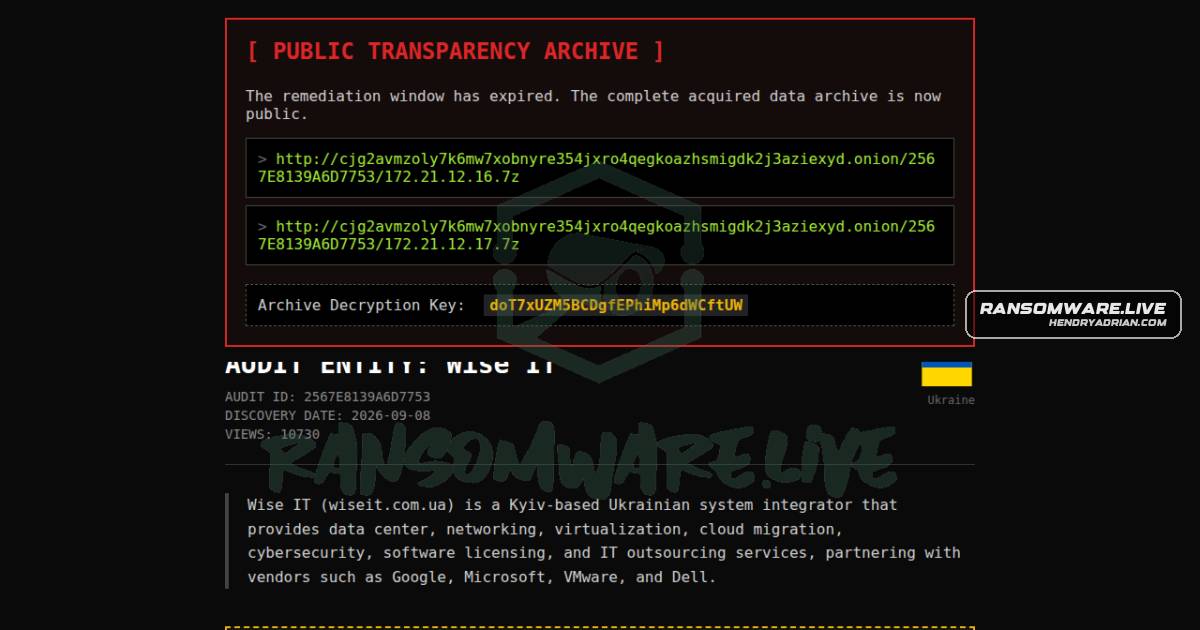
A ransomware.live record says AuditTeam targeted Kyiv-based Wise IT and disrupted its IT services. The post attributes the information to the group’s public claims and says it could not confirm their accuracy.
Key points
- The record identifies Wise IT, a Kyiv-based Ukrainian system integrator, as the alleged victim.
- AuditTeam is named as the ransomware actor; the post attributes the claim to the group and says it could not confirm it.
- The reported impact is disruption to Wise IT’s IT services.
- The record lists September 16, 2026, as the discovery date and September 8, 2026, as the publication date.
Article Details
- Victim
- Wise IT
- Victim Domain
- wiseit.com.ua
- Claim Date
- 2026-09-08
- Encryption Status
- Unknown
- Exfiltration Status
- Unknown
- Ransom Demand
- Unknown
- Leak Status
- A public claim by AuditTeam is reported; the source does not confirm a leak or publication of victim data.