
AuditTeam Claims to Have Targeted Russian Organization buben
Summary
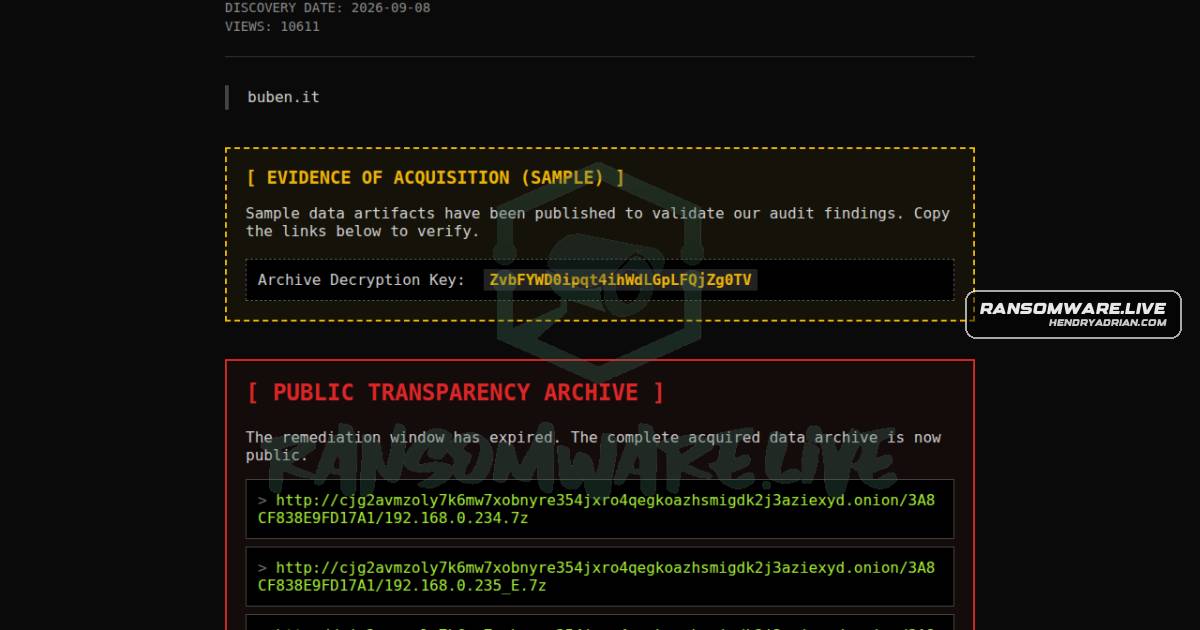
AuditTeam claims it compromised systems linked to buben[.]it and issued extortion demands. The ransomware.live post identifies buben in Russia and says the claims are unconfirmed.
Key points
- The ransomware group AuditTeam claims to have targeted buben in Russia.
- The group alleges it compromised systems linked to buben[.]it and deployed extortion demands.
- The post lists September 16, 2026, as the discovery date and September 8, 2026, as the publication date.
- The post says the claims are based on public statements by AuditTeam and have not been confirmed.
Article Details
- Victim
- buben
- Victim Domain
- buben.it
- Claim Date
- 2026-09-08
- Encryption Status
- Unknown; the source does not report whether systems were encrypted.
- Exfiltration Status
- Unknown; the source does not report whether data was exfiltrated.
- Ransom Demand
- The source says extortion demands were claimed, but reports no amount.
- Leak Status
- A ransomware-group claim was reported; the source says the claim's accuracy could not be confirmed.