
DarkOwl Finds More Exposed Plain-Text Passwords and Widespread Password Reuse
Summary
DarkOwl’s year-over-year analysis found more exposed credentials in its darknet dataset, including a rise in plain-text passwords. It also found common weak patterns and password reuse among 45% of matched work and personal accounts.
Key points
- DarkOwl reported 10.07 billion exposed email addresses in its dataset, up from 8.68 billion the prior year; more than half appeared with an associated password.
- Plain-text email-and-password combinations rose from 4.29 billion to 5.16 billion, while combinations with hashed passwords remained near 521 million.
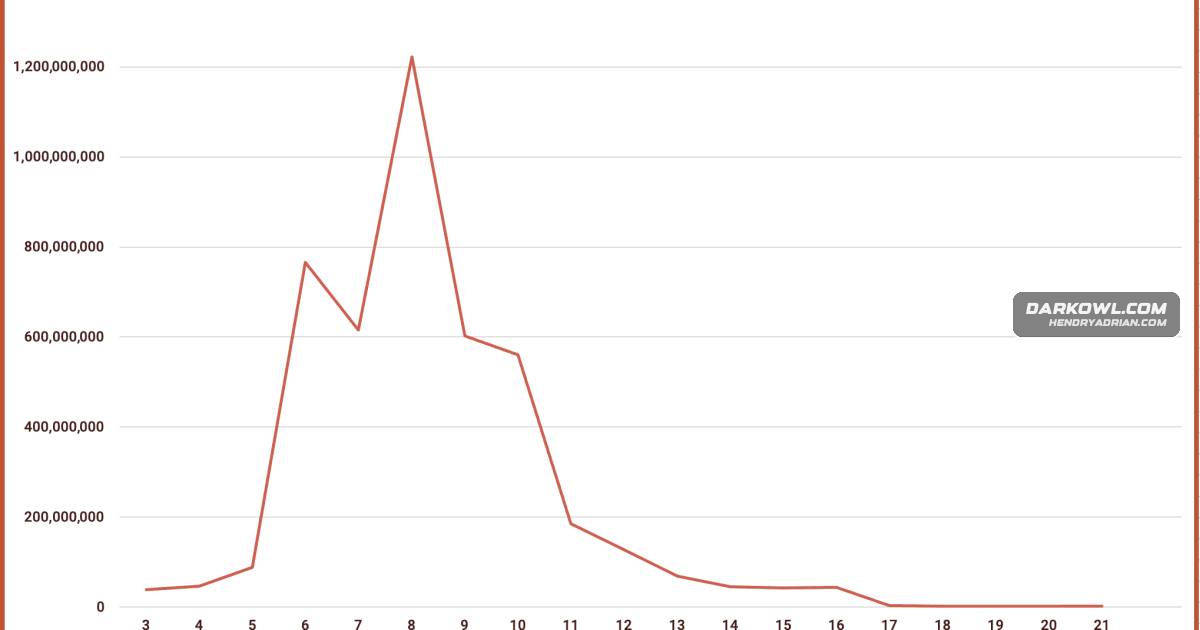
- Eight-character passwords were the most common length among the plain-text passwords analyzed.
- The company reported increases in passwords using “123456,” “123456789,” “qwerty,” and the literal word “password.”
- DarkOwl counted 643.5 million passwords meeting its definition of strong, slightly up from the previous year.
- In its analysis of matched company and commercial email accounts, 45% shared the same password; DarkOwl said this was likely an underestimate.
Article Details
- Publisher
- DarkOwl
- Report Period
- 2022–2023; published 2023-05-05
- Scope
- Password trends and exposed credentials in DarkOwl's darknet data.
- Key Statistics
- DarkOwl detected 10,069,116,483 compromised email addresses, up from 8,680,000,000 in 2022 (a reported 16% increase).
- 5,681,306,514 email-and-password combinations were detected, up from 5,460,000,000 the prior year.
- 5,160,309,835 exposed email addresses had associated plaintext passwords, up from 4,285,451,030.
- 45% of matched work and personal accounts reused the same password; the article characterizes this as a likely underestimate.
- The analysis detected 35,085,849 instances of linked email addresses appearing with the same password.
- Recommendations
- Implement more rigorous password policies, including multi-factor authentication.
- Use digits and special characters in passwords to help defend against password crackers.