
Emperador Claims Electrolux Data Theft and Threatens to Leak 41 GB
Summary
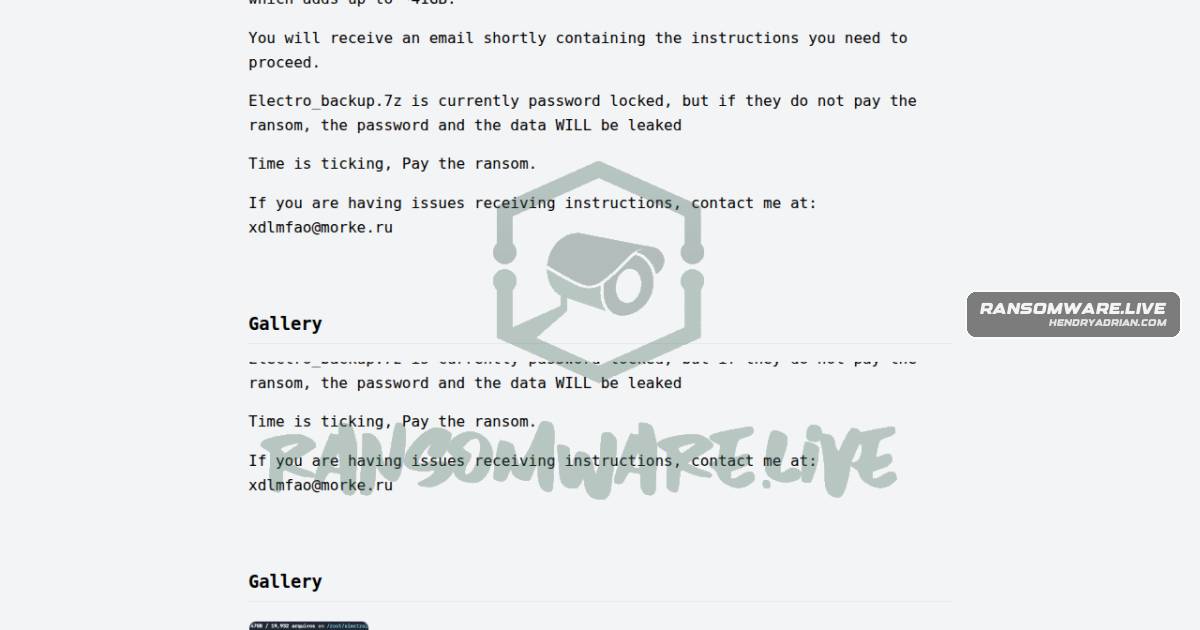
The ransomware group emperador claims it accessed Electrolux’s Azure database in Sweden and exfiltrated about 41 GB. It threatens to leak a password-protected archive unless paid; the report says the claims are unconfirmed.
Key points
- The claim names Electrolux, a manufacturing company, as the victim and Sweden as the location.
- Actor emperador claims it accessed the company’s Azure database and exported approximately 41 GB of data.
- The actor threatens to release the password and data for the password-protected archive Electro_backup.7z if ransom is not paid.
- The actor said ransom instructions would be sent by email.
- The claim was listed as discovered on September 19, 2026; the report says it could not confirm the actor’s claims.
Article Details
- Victim
- Electrolux
- Claim Date
- 2026-09-19
- Encryption Status
- Unknown; the group claim describes data access and exfiltration, not encryption of victim systems.
- Exfiltration Status
- Claimed by emperador; unconfirmed by the source.
- Exfiltrated Data
- The group claimed it exported all data from an Azure database and threatened to leak the password and data from the password-protected archive Electro_backup.7z. The claim is unconfirmed.
- Exfiltrated Size
- Approximately 41 GB, according to the group claim.
- Ransom Demand
- Payment was demanded; no amount was stated.
- Leak Status
- Threatened; the group said it would release the archive password and data if payment was not made. No completed leak is reported.