CL0P’s MOVEit Campaign Hit Hundreds of Organizations, DarkOwl Analysis Finds
Summary
DarkOwl reports on CL0P’s MOVEit campaign and says rising DarkSonar signals appeared before many affected organizations’ attacks. The article also outlines victim and data-release figures and risks to organizations through third parties.
Key points
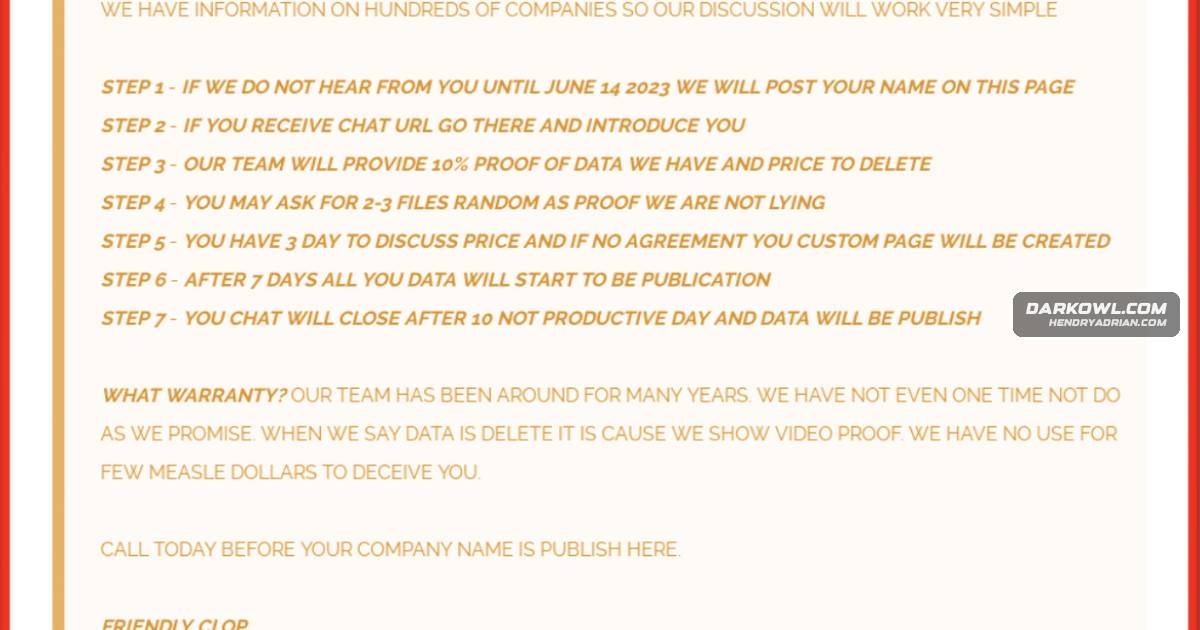
- CL0P exploited a zero-day in MOVEit Transfer and used stolen data for extortion.
- By July 24, 2023, CL0P had listed 187 victim names; the article says the total number of successfully compromised organizations was unclear.
- As of July 24, the group had removed 11 victims from its leak site, posted full data for 21, and released partial data for 65.
- DarkOwl’s analysis of 140 company domains found an elevated DarkSonar signal in the four months before an attack for 60% of all companies, or 67% of those with email exposure.
- DarkOwl said signals were trending upward for 84% of all companies and 94% of those with email exposure; it noted that further analysis was needed.
- The article describes risks to third parties whose sensitive information may be held by MOVEit users or affected vendors.
Article Details
- Event Type
- CL0P ransomware and extortion campaign exploiting a zero-day vulnerability in MOVEit Transfer.
- Impact
- The campaign resulted in large-scale data theft and extortion. CL0P listed hundreds of victim organizations, released full or partial data for some, and threatened to publish stolen data unless victims paid. The article reports that finance was the most impacted industry in DarkOwl’s victim assessment.