
AuditTeam Claims Ransomware Attack on Italian Organization st***co
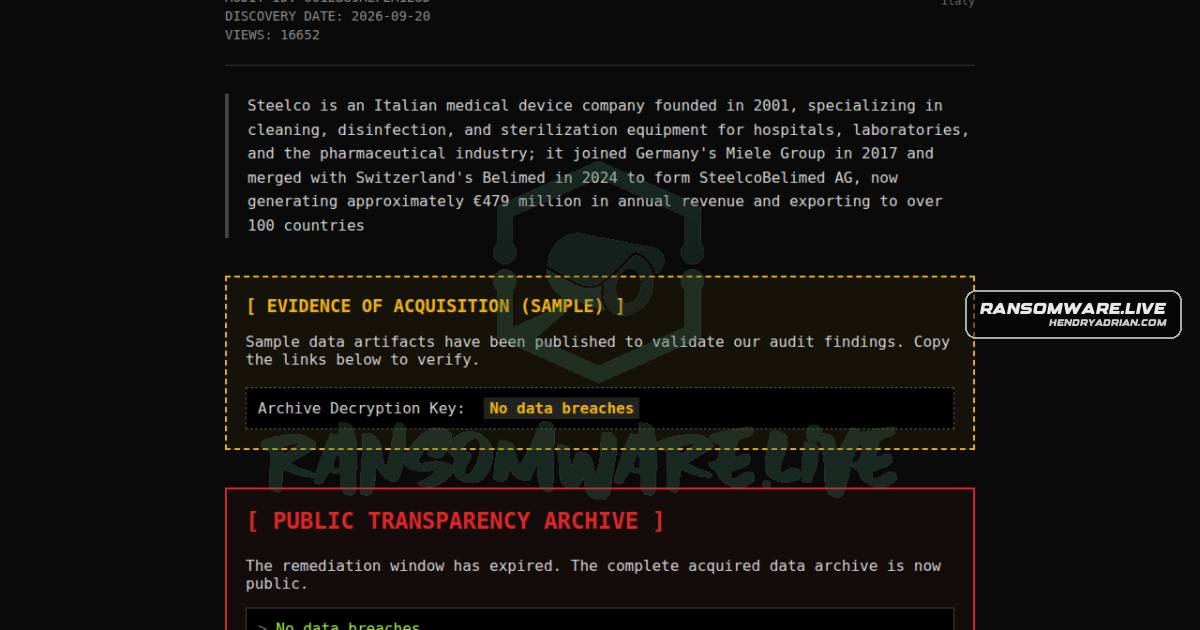
Summary
AuditTeam claims it encrypted data at Italian organization st***co and demanded payment for decryption, with a threat of data theft. The report is based on the group’s public claims and has not been independently confirmed.
Key points
- The ransomware group AuditTeam claims it targeted st***co in Italy.
- The claim alleges data encryption, a demand for payment to decrypt it, and a threat of data theft.
- The record lists September 20, 2026, as the discovery date and publication date.
- The report says the claims could not be confirmed and invites an official statement from the organization.
Article Details
- Victim
- st***co
- Victim Domain
- Unknown
- Claim Date
- 2026-09-20
- Encryption Status
- Claimed by AuditTeam; unverified by the source and not confirmed by the victim.
- Encrypted Size
- Unknown
- Exfiltration Status
- A threat of data theft is reported; actual exfiltration is not confirmed.
- Exfiltrated Data
- Unknown
- Exfiltrated Size
- Unknown
- Ransom Demand
- Payment for decryption was reportedly demanded; amount not disclosed.
- Leak Status
- Unknown