Ransomware Trends in 2023: Rising Profits, Multi-Extortion and Evolving Tactics
Summary
DarkOwl’s 2023 overview describes rising ransomware profits, expanding multi-extortion, data theft, stealthier encryption practices and increasingly organized groups, while warning that broader attack surfaces may sustain activity.
Key points
- The article says January 2023 had 33 reported ransomware incidents, a record for that month, and that 2023 was on track to be the most active year by reported incidents.
- Some reviews estimated ransomware actors had made about $450 million by June 2023, with roughly $900 million projected for the year if the pace continued.
- The overview describes double, triple and quadruple extortion, including threats to sell stolen data, launch DDoS attacks or contact victims’ partners and customers.
- It reports that attackers are targeting sensitive documents, including building layouts and critical-infrastructure materials, in addition to personal information.
- The article discusses tools and groups combining information stealers or remote access trojans with ransomware, and names RedEnergy and FIN8 as examples.
- Some actors are using intermittent encryption or forgoing encryption, which the article says can reduce resource costs and help evade security tools.
- The article anticipates continued group recruitment and sharing of tactics, automation, and expansion toward Linux, IoT and container environments.
Article Details
- Publisher
- DarkOwl
- Report Period
- 2022–2023; published 2023-08-15
- Scope
- Ransomware trends, extortion methods, and threat-group tactics
- Key Statistics
- January 2023 had 33 reported ransomware incidents, described as the highest number ever reported for that month.
- Some reviews estimated ransomware actors had made approximately $450 million through June 2023.
- Those reviews projected approximately $900 million in 2023 if the attack rate continued through the second half of the year; this was a conditional estimate.
- Recommendations
- Maintain up-to-date system backups to support data restoration and business continuity.
- Strengthen public-private partnerships to share threat intelligence and indicators of compromise.
- Raise awareness and improve protection against ransomware in critical infrastructure, academic, technology, and government sectors.
MITRE ATT&CK
Threat Actors
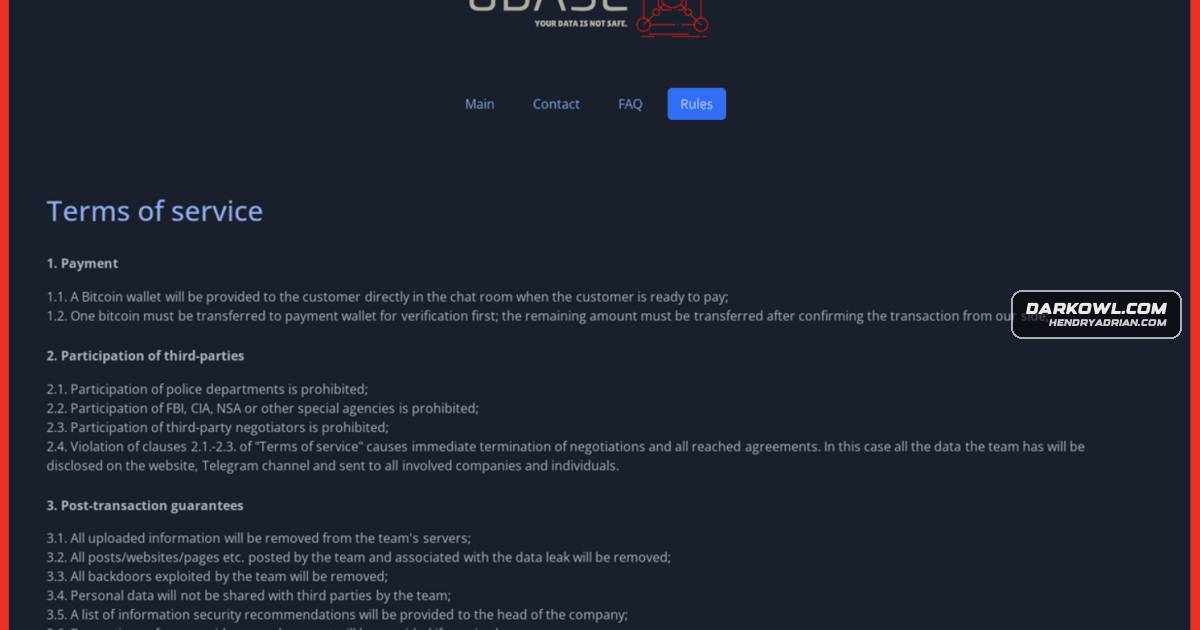
8baseRansomware group described as operating a double-extortion campaign and listing victims.Cl0pRansomware group described as a prolific double-extortion operator that penetrated hundreds of organizations in 2023.ContiRansomware group whose 2022 leak revealed its organized operations and internal processes.FIN8Financially motivated cybercrime group reported to be using ransomware variants.KarakurtGroup described as emerging from Conti and commonly operating without encryption, focusing on extortion.
Malware
RedEnergyRedEnergy, a new Stealer-as-a-Ransomware technology, steals information from various web browsers while also facilitating ransomware activities.ShadowVaultA June 2023 post on criminal market XSS details the use of ShadowVault stealer, which specifically targets Mac operating systems and can be used in Chrome, Edge, Brave, and other browsers: White RabbitA Club IO post from September 2022, detailing FIN8’s possession of White Rabbit ransomware:
Products
Countries
Industries
AcademicCritical infrastructure, academic, technology, and government sectors must all raise awareness and assist in protection from ongoing ransomware campaigns.Critical infrastructureafter blueprints, sensitive documents of physical layouts for buildings, and those related to critical infrastructure and key resources (CI/KR).GasThe entities behind RedEnergy use publicly available LinkedIn pages to target the oil, gas, and telecom sectors.Governmentevolving, and it is imperative to pay attention to its trends and try to get cyber practitioners, government, law enforcement (LE), Computer Emergency Response Teams (CERTs), and more collective bodies to takeOilThe entities behind RedEnergy use publicly available LinkedIn pages to target the oil, gas, and telecom sectors.TechnologyThis is in addition to technology trends like cloud computing and the IOT space increasing access points and increasing the overall attack surface area, allowing malicious actors more opportunities to enter a network.TelecommunicationsThe entities behind RedEnergy use publicly available LinkedIn pages to target the oil, gas, and telecom sectors.