
August Cybersecurity Roundup Covers Threat Campaigns, Ransomware and Policy
Summary
A monthly roundup highlights reports on cyber campaigns, ransomware exploiting a Veeam vulnerability, AI-themed Facebook ad credential theft, Android RATs, a cryptocurrency heist warning, a new CISA catalog entry and a US cyber workforce strategy.
Key points
- The US announced a National Cyber Workforce and Education Strategy aimed at addressing cybersecurity workforce needs through education and training.
- Researchers linked the Space Pirates actor to attacks against at least 16 organizations in Russia and Serbia, reporting espionage, theft of confidential information and use of Deed RAT.
- The Cuba ransomware group was reported exploiting CVE-2023-27532 in Veeam software; analysis found the ransomware stops if Russian language packs or a Russian keyboard are detected.
- Fraudulent Facebook ads promoting AI-themed business tools led users to a site that stole cookies, browser information and access tokens; Meta took down the false pages after a Trend Micro alert.
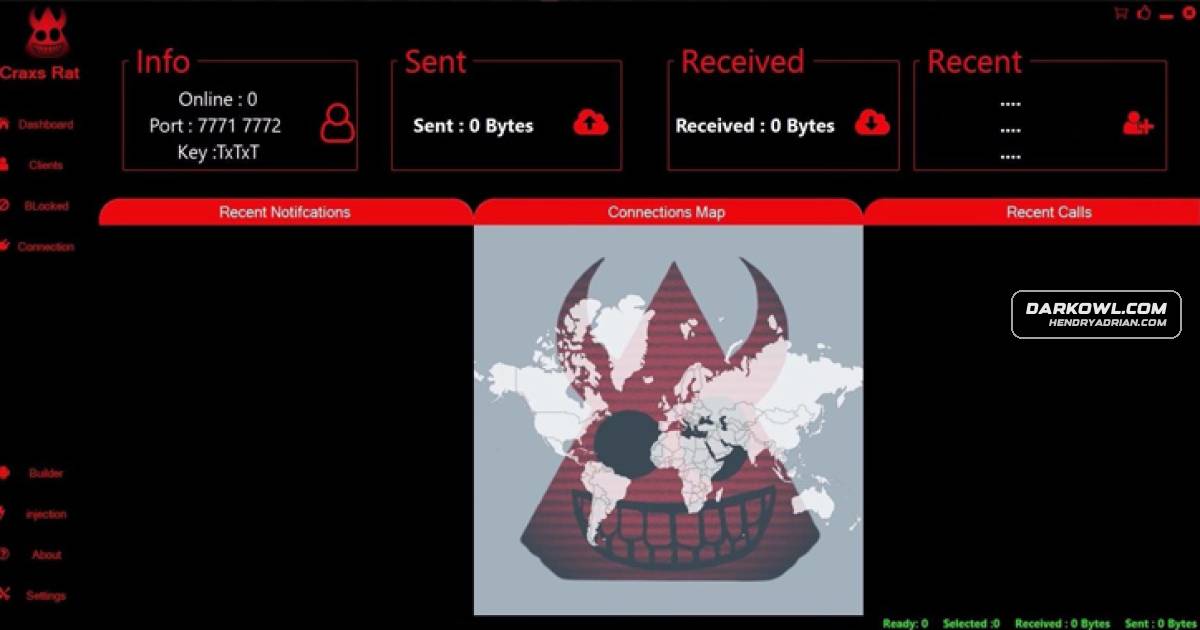
- A report attributed Android RATs including CypherRAT and CraxsRAT to Syrian actor EVLF, who reportedly sold them since 2022 and said he would shut down in August.
- The FBI warned that North Korea-linked individuals could attempt to convert cryptocurrency valued at more than $40 million, attributing the blockchain activity to TraderTraitor, also known as Jade Sleet.
- CISA added CVE-2023-24489, an improper access control vulnerability in Citrix Content Collaboration ShareFile, to its Known Exploited Vulnerabilities catalog.
Article Details
- Event Type
- Monthly cybersecurity threat-intelligence news roundup
- Impact
- The roundup reports on cyber workforce initiatives, espionage and ransomware activity, credential and data theft, Android RATs, a cryptocurrency heist, and a newly cataloged exploited vulnerability. The reported consequences include attacks on organizations in Russia and Serbia, theft of business-account credentials and browser data, and potential conversion of more than $40 million in cryptocurrency.
CVE
Threat Actors
Cuba ransomware groupReportedly actively exploited CVE-2023-27532; the article says its ransomware terminates if Russian language packs or a Russian keyboard are detected.EVLFSyrian threat actor reportedly identified as the author of CypherRAT and CraxsRAT, which he sold on a marketplace.Jade SleetThe FBI attributed the reported blockchain activity involving cryptocurrency valued at over $40 million to TraderTraitor, also known as Jade Sleet.Space PiratesThreat actor linked to attacks against at least 16 organizations in Russia and Serbia, reportedly harvesting PST email archives and conducting espionage and theft of confidential information.
Malware
CraxsRAT5. Syrian Threat Actor EVLF Unmasked as Creator of CypherRAT and CraxsRAT Android Malware – The Hacker NewsCypherRAT5. Syrian Threat Actor EVLF Unmasked as Creator of CypherRAT and CraxsRAT Android Malware – The Hacker NewsDeed RATin Russia and Serbia over the past year, has been harvesting PST email archives and making use of Deed RAT – showing that they are adding new cyber weapons to their TTPs but their main goals are still espionageRedLineCommunity researchers compared this latest campaign to the spring 2023 RedLine stealer campaign.
Vendors
CitrixCVE-2023-24489 Citrix Content Collaboration ShareFile Improper Access Control Vulnerability has been added.MetaTrendMicro discovered the false Facebook pages and alerted Meta, who took the pages down.TrendMicroTrendMicro discovered the false Facebook pages and alerted Meta, who took the pages down.Veeam3. Cuba ransomware group observed exploiting high-severity Veeam bug – SC Media
Products
Countries
North KoreaThe US FBI issued a statement indicating that individuals linked with North Korea could make efforts to convert pilfered cryptocurrency valued at over $40 million into actual funds.Russia2. Researchers Expose Space Pirates’ Cyber Campaign Across Russia and Serbia – The Hacker NewsSerbia2. Researchers Expose Space Pirates’ Cyber Campaign Across Russia and Serbia – The Hacker News