What Bulletproof Hosting Is and How It Supports Cybercriminal Operations
Summary
Bulletproof hosting providers tolerate illicit activity and may evade takedowns through lenient jurisdictions, shell companies, and infrastructure moves. The article explains their role in cybercrime and cites Cloudzy and DarkOwl observations as examples.
Key points
- Bulletproof hosting providers are described as allowing content and activity that traditional hosts may restrict, including fraud, spam, and other illicit operations.
- The article says providers may ignore abuse reports and takedown requests, shift IP ranges, or warn customers about enforcement actions.
- Providers may operate in jurisdictions with lenient cyber laws or limited extradition, and may accept cryptocurrency payments.
- The article describes Cloudzy as infrastructure used by nation-state actors, ransomware affiliates, and initial access brokers; researchers estimated 40–60% of its activity was malicious.
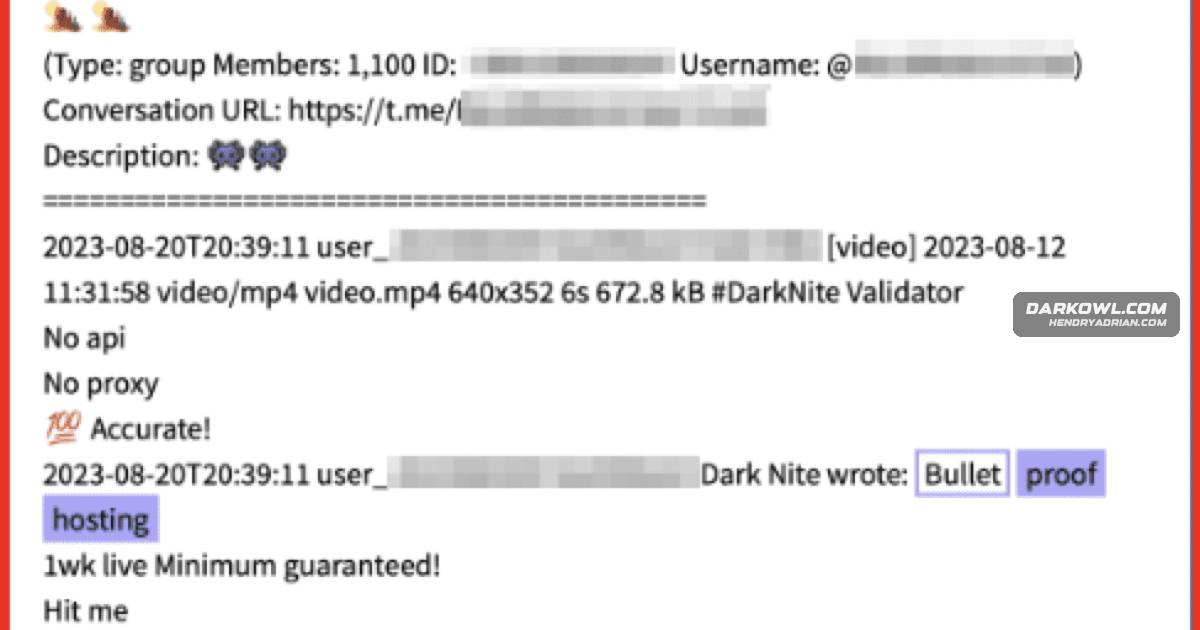
- DarkOwl analysts observed demand for reliable, low-cost hosting with uptime guarantees and protection from both DDoS attacks and law enforcement.
- The article says blacklisting an entire IP block is one way to combat material hosted by bulletproof providers.
Article Details
- Topic
- Bullet-proof hosting and its role in enabling cybercrime
Vendors
CloudzyIn August of 2023, researchers in the cyber threat field broke the news that Cloudzy, a New York company actually run out of Tehran, Iran, was providing infrastructure to both nation state and criminal cyber actors.CrazyRDPActors on discord discuss the merits of having either a virtual private server (VPS) or dedicated BPH, and name CrazyRDP and Privatealps as bonafide BPH.PrivatealpsActors on discord discuss the merits of having either a virtual private server (VPS) or dedicated BPH, and name CrazyRDP and Privatealps as bonafide BPH.
Countries
BulgariaLocations that commonly allow for and host BPH include: China, Romania, Bulgaria, Estonia, Panama, and the Seychelles, among others.ChinaLocations that commonly allow for and host BPH include: China, Romania, Bulgaria, Estonia, Panama, and the Seychelles, among others.EstoniaLocations that commonly allow for and host BPH include: China, Romania, Bulgaria, Estonia, Panama, and the Seychelles, among others.IranIn August of 2023, researchers in the cyber threat field broke the news that Cloudzy, a New York company actually run out of Tehran, Iran, was providing infrastructure to both nation state and criminal cyber actors.PanamaLocations that commonly allow for and host BPH include: China, Romania, Bulgaria, Estonia, Panama, and the Seychelles, among others.RomaniaLocations that commonly allow for and host BPH include: China, Romania, Bulgaria, Estonia, Panama, and the Seychelles, among others.SeychellesLocations that commonly allow for and host BPH include: China, Romania, Bulgaria, Estonia, Panama, and the Seychelles, among others.