September Threat Intelligence Roundup Covers MGM Attack, Malware Campaigns and Marketplace Takedown
Summary
A September roundup summarizes the claimed ALPHV/BlackCat attack on MGM, malware and credential-theft campaigns, GhostSec’s release of alleged surveillance-tool code, a Snatch ransomware warning, and a Finnish dark-web marketplace takedown.
Key points
- ALPHV/BlackCat claimed responsibility for the MGM incident, which disrupted services at resorts and hotels; DarkOwl said no new data was listed on the gang’s site at that time.
- The roundup reported that ShroudedSnooper deployed HTTPSnoop and PipeSnoop malware at Middle Eastern telecom providers; attribution and motive were unknown.
- A payment-card-skimming campaign expanded from Asia-Pacific to Latin and North America, targeting ecommerce sites and point-of-sale providers.
- GhostSec released source code it said came from Iran’s FANAP, including facial recognition, GPS tracking, and license-plate recognition capabilities.
- A Vietnamese cybercrime group reportedly used compromised LinkedIn accounts and Duckport malware to steal information and target Facebook business accounts.
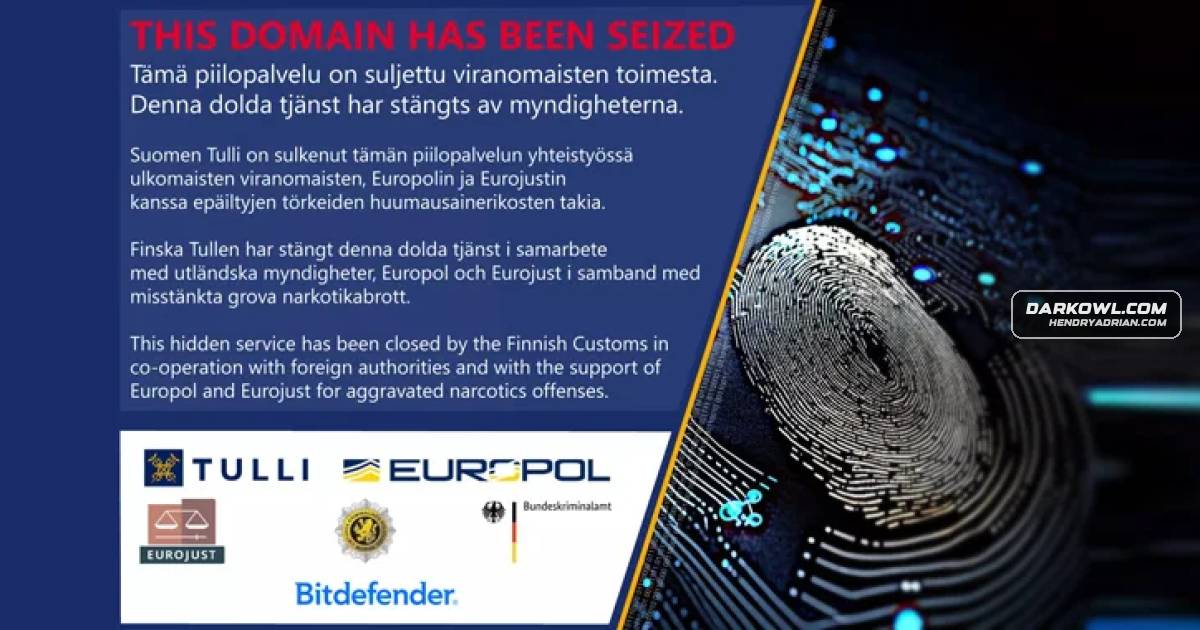
- Finnish authorities and international partners announced the takedown of the PIILOPUOTI dark-web narcotics marketplace.
- The FBI and CISA warned that Snatch ransomware can force Windows systems into safe mode before encryption and targets critical infrastructure sectors.
Article Details
- Event Type
- Monthly roundup of reported cyber incidents, including ransomware claims, malware deployments, payment-card skimming, source-code disclosure, account compromise, a law-enforcement marketplace takedown, and ransomware activity.
- Impact
- Reported effects included outages to MGM resort and hotel services; compromise of telecom providers; theft of payment-card data and social-media credentials and cookies; disclosure of source code for an alleged Iranian surveillance tool; and the takedown of a dark-web drug marketplace. The article also describes ransomware targeting critical infrastructure and other sectors.
MITRE ATT&CK
Threat Actors
ALPHVNamed as part of the ransomware group that claimed responsibility for the MGM incident; the article gives the group name as ALPHV/Blackcat.BlackCatNamed alongside ALPHV as part of the ransomware group that claimed responsibility for the MGM incident.GhostSecHacktivist group reported to have revealed source code from Iran's FANAP group.Scattered SpiderReportedly also involved in the MGM incident; the article says the group teamed up with ALPHV in early 2023 and hit Caesars Entertainment.ShroudedSnooperThreat actor group reported to have installed HTTPSnoop and PipeSnoop malware at Middle Eastern telecom providers.
Malware
DuckportAfter compromising LinkedIn accounts, the Vietnamese cyber group is using Duckport malware to perform information stealing ops, and then moving to other social media platforms such as Facebook, continuing to stealHTTPSnoop2. Hackers backdoor telecom providers with new HTTPSnoop malware – Bleeping ComputerPipeSnoopThreat actor group “ShroudedSnooper” has installed HTTPSnoop and PipeSnoop malware throughout Middle Eastern telecom providers.Snatch7. FBI, CISA Issue Joint Warning on ‘Snatch’ Ransomware-as-a-Service – Dark Reading
Countries
FinlandLaw enforcement in Finland, including Finnish customs, announced the takedown of illegal dark web narcotic marketplace, Polopuoti on September 20.GermanyThe drugs came from abroad into Finland, and this was a joint operation that also involved parties from Germany, Romania, and Lithuania.IranHacktivist group GhostSec revealed the source code from Iran’s FANAP group, a technology conglomerate that has ties to the financial, government, and technology sectors in Iran.LithuaniaThe drugs came from abroad into Finland, and this was a joint operation that also involved parties from Germany, Romania, and Lithuania.RomaniaThe drugs came from abroad into Finland, and this was a joint operation that also involved parties from Germany, Romania, and Lithuania.
Industries
DefenseThe Snatch group is targeting CI/KR, including IT and agricultural firms, and the defense industrial base.financialHacktivist group GhostSec revealed the source code from Iran’s FANAP group, a technology conglomerate that has ties to the financial, government, and technology sectors in Iran.GovernmentHacktivist group GhostSec revealed the source code from Iran’s FANAP group, a technology conglomerate that has ties to the financial, government, and technology sectors in Iran.TechnologyHacktivist group GhostSec revealed the source code from Iran’s FANAP group, a technology conglomerate that has ties to the financial, government, and technology sectors in Iran.