Uganda Agriculture Ministry Allegedly Suffers Data Breach
Summary
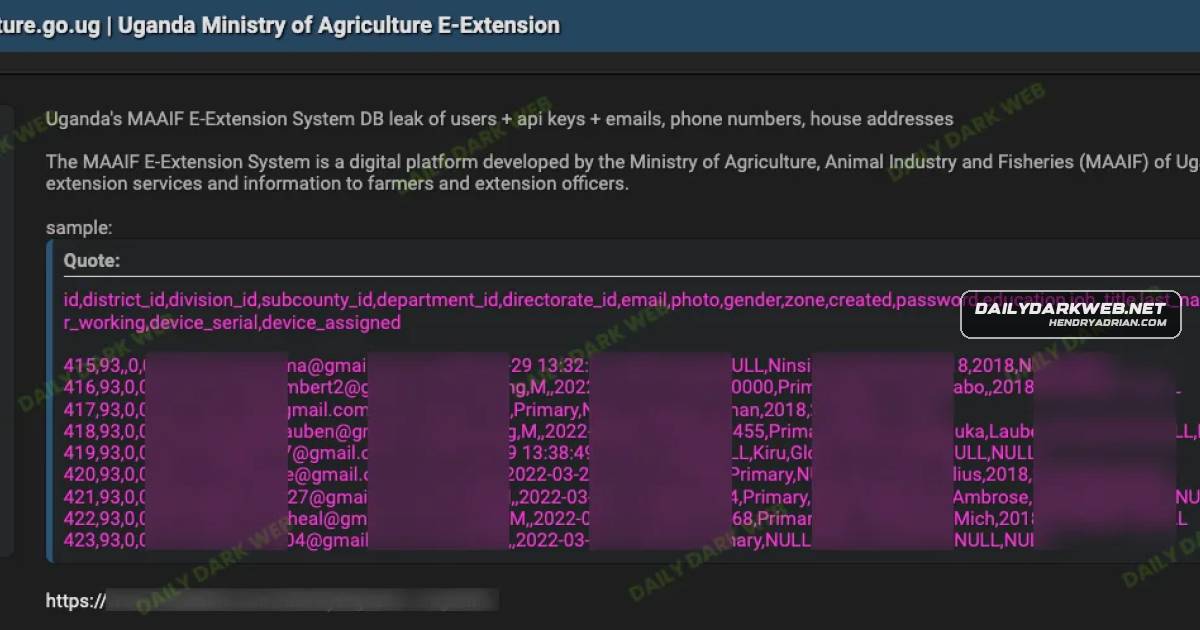
MAAIF, Uganda’s Ministry of Agriculture, allegedly suffered a data breach involving a database with users’ personal information and system credentials, including passwords, API keys and bearer tokens.
Key points
- The alleged breach involves MAAIF’s E-Extension platform, which serves farmers and extension officers.
- The reported database contains names, email addresses, phone numbers, home addresses and job titles.
- Exposed information reportedly includes passwords, API keys, bearer tokens and gateway configurations.
- The source describes the breach and exposed data as alleged; it provides no details on the attack method or remediation.
Article Details
- Victim Organization
- Ministry of Agriculture, Animal Industry and Fisheries (MAAIF)
- Incident Type
- Alleged data breach involving a leaked database
- Data Types Exposed
- First and last names
- Email addresses
- Phone numbers
- House addresses
- Passwords
- Job titles
- API keys
- Bearer tokens
- Gateway configurations
- Claim Status
- alleged