
Beelzebub Ransomware Actor Claims Rewrite and Seeks New Operators
Summary
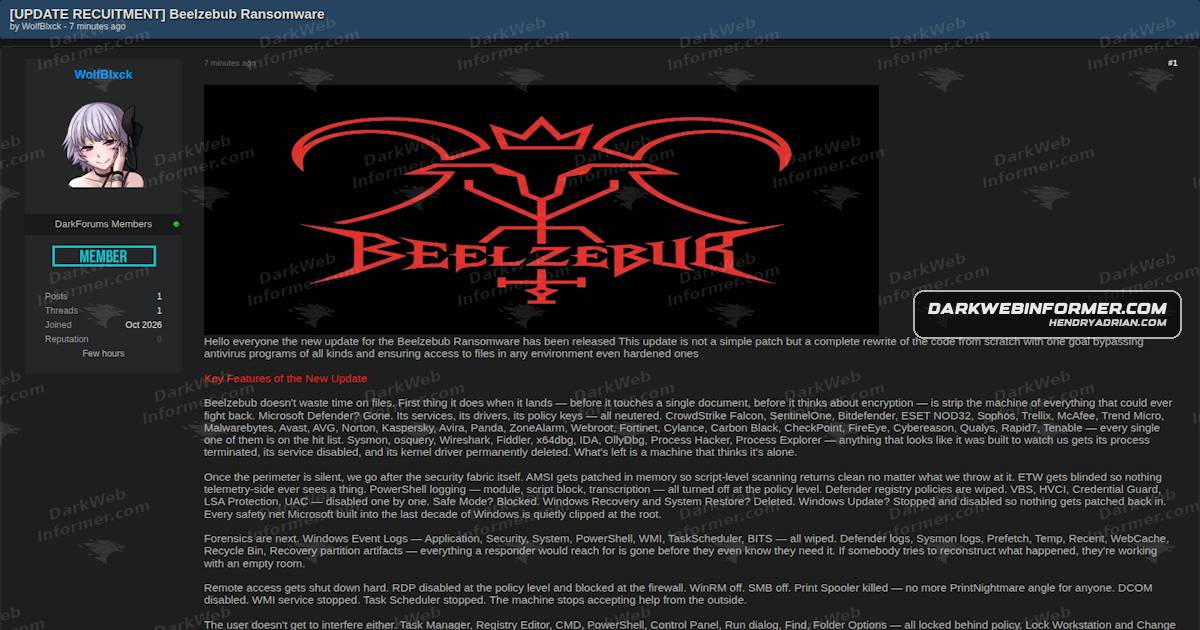
An actor using the handle WolfBlxck claims Beelzebub ransomware has been rewritten with expanded defense-evasion features and is recruiting a developer, penetration tester, and negotiator. The claims and capabilities are unverified.
Key points
- Screenshots document the actor's recruitment and update post, but do not independently verify its claims.
- The actor claims the rewrite can interfere with security tools, suppress telemetry, erase forensic artifacts, disable recovery features, and spread through removable media and network shares.
- The recruitment post seeks a developer, penetration tester, and negotiator.
- Proposed target categories include healthcare, education, small and medium-sized businesses, and local cloud providers.
- No malware hash, attacker-controlled domain, or attacker-controlled IP address was visible in the supplied screenshots.
Article Details
- Event Type
- A ransomware operator using the handle WolfBlxck announced a claimed rewrite of Beelzebub and recruitment for developer, penetration tester, and negotiator roles.
- Impact
- The post claims the rewritten ransomware would disrupt endpoint defenses, suppress telemetry, remove forensic artifacts, interfere with recovery, persist, and propagate through removable media and network shares. Hospitals, schools and universities, SMBs, and local cloud providers were listed as proposed targets. These capabilities and recruitment claims have not been independently verified.
MITRE ATT&CK
T1070.001 · Clear Windows Event LogsThe post claims the ransomware clears Windows event logs and other forensic artifacts; this capability is unverified.T1490 · Inhibit System RecoveryThe operator claims the malware removes or disables recovery-related components; this capability is unverified.T1547.001 · Registry Run Keys / Startup FolderThe supplied screenshot reportedly describes Registry Run/RunOnce and Startup Folder persistence; the capability is unverified.T1562.001 · Disable or Modify ToolsThe operator claims Beelzebub disables or interferes with security products, monitoring utilities, logging, and telemetry; these capabilities are unverified.