Chinese-Speaking Hackers Exploit WordPress and Other Flaws to Steal Government Data
Summary
GreyNoise linked a campaign to a Chinese-speaking actor associated with Red Heron. Researchers report breaches of at least 49 organizations and theft of 18,566 records from a Western government organization, alongside exploitation of ZyXEL and other platforms.
Key points
- Researchers say the actor exploited WordPress wp2shell flaws to breach at least 49 organizations across 29 countries.
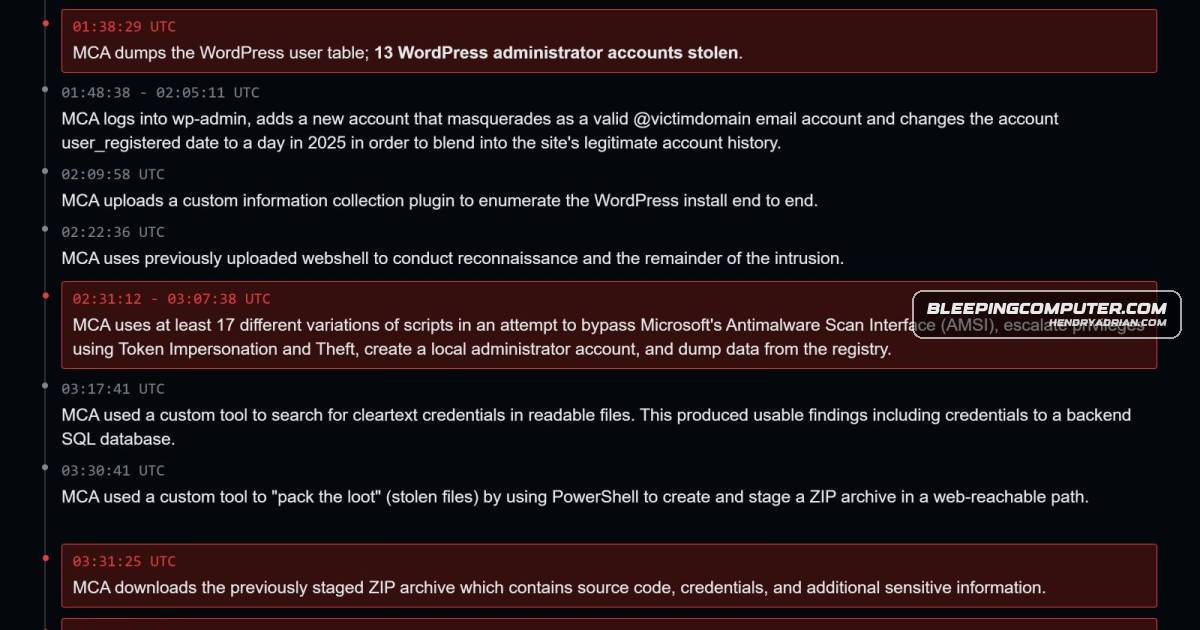
- In one intrusion at an unnamed Western government organization, attackers accessed a backend SQL server and stole at least 18,566 records, including accounts, plaintext passwords, and PII.
- GreyNoise reports the attackers conducted reconnaissance and tried 17 scripts to bypass AMSI, escalate privileges, create a local administrator, and extract registry data.
- The actor exploited a flaw in ZyXEL GS1900 switches, compromising 996 devices in 48 countries and extracting configurations, network information, and hashed root credentials.
- GreyNoise also observed targeting of Ubiquiti, PAN-OS GlobalProtect, FlowiseAI, Gitea, Nuclio, SENAITE LIMS, and Proxmox VE.
Article Details
- Event Type
- Cyber intrusion and data theft involving exploitation of vulnerabilities across multiple technologies
- Impact
- The activity breached at least 49 organizations in 29 countries using WordPress vulnerabilities. One government intrusion resulted in the theft of at least 18,566 records containing accounts, plaintext passwords, and personally identifiable information connected to government and law-enforcement agencies. The actor also compromised 996 ZyXEL devices, extracting configurations, network information, and hashed root credentials.
MITRE ATT&CK
T1012 · Query RegistryThe actor attempted to extract registry data.T1046 · Network Service DiscoveryThe actor checked listening ports and available services.T1082 · System Information DiscoveryThe actor checked system information during reconnaissance.T1087 · Account DiscoveryThe actor checked local accounts during reconnaissance.T1098 · Account ManipulationThe actor attempted to create a local administrator account.T1110.003 · Password SprayingThe actor used backend database credentials in a password-spraying attack against an internal SQL server.T1134 · Access Token ManipulationThe actor attempted privilege escalation through token impersonation or theft.T1190 · Exploit Public-Facing ApplicationThe actor exploited vulnerabilities in WordPress and other internet-facing technologies to gain access.T1518.001 · Security Software DiscoveryThe actor checked Microsoft Defender during security reconnaissance.
CVE
CVE-2022-0847targeting of PAN-OS GlobalProtect, FlowiseAI (CVE-2026-56271), the Linux kernel’s Dirty Pipe flaw (CVE-2022-0847), Gitea (CVE-2026-60004), Nuclio (CVE-2026-79756), SENAITE LIMS (CVE-2026-54569) and Proxmox VECVE-2023-54391Gitea (CVE-2026-60004), Nuclio (CVE-2026-79756), SENAITE LIMS (CVE-2026-54569) and Proxmox VE (CVE-2023-54391).CVE-2026-34908Additionally, the hackers attempted to chain the Ubiquiti UniFi OS vulnerabilities tracked as CVE-2026-34908, CVE-2026-34909, and CVE-2026-34910 to obtain root-level remote code execution.CVE-2026-34909Additionally, the hackers attempted to chain the Ubiquiti UniFi OS vulnerabilities tracked as CVE-2026-34908, CVE-2026-34909, and CVE-2026-34910 to obtain root-level remote code execution.CVE-2026-34910Additionally, the hackers attempted to chain the Ubiquiti UniFi OS vulnerabilities tracked as CVE-2026-34908, CVE-2026-34909, and CVE-2026-34910 to obtain root-level remote code execution.CVE-2026-54569Dirty Pipe flaw (CVE-2022-0847), Gitea (CVE-2026-60004), Nuclio (CVE-2026-79756), SENAITE LIMS (CVE-2026-54569) and Proxmox VE (CVE-2023-54391).CVE-2026-56271GreyNoise also confirmed targeting of PAN-OS GlobalProtect, FlowiseAI (CVE-2026-56271), the Linux kernel’s Dirty Pipe flaw (CVE-2022-0847), Gitea (CVE-2026-60004), Nuclio (CVE-2026-79756), SENAITE LIMS (CVE-2026-54569)CVE-2026-60004GlobalProtect, FlowiseAI (CVE-2026-56271), the Linux kernel’s Dirty Pipe flaw (CVE-2022-0847), Gitea (CVE-2026-60004), Nuclio (CVE-2026-79756), SENAITE LIMS (CVE-2026-54569) and Proxmox VE (CVE-2023-54391).CVE-2026-60137According to the researchers, the threat actor leveraged the wp2shell vulnerabilities (CVE-2026-63030 and CVE-2026-60137) in the WordPress Core component to breach at least 49 organizations in 29 countries.CVE-2026-63030According to the researchers, the threat actor leveraged the wp2shell vulnerabilities (CVE-2026-63030 and CVE-2026-60137) in the WordPress Core component to breach at least 49 organizations in 29 countries.CVE-2026-7273On August 17, the threat actor started to exploit a high-severity flaw (CVE-2026-7273) in ZyXEL GS1900 Smart Managed Switches and compromised 996 devives in 48 countries to extract device configurations, networkCVE-2026-79756(CVE-2026-56271), the Linux kernel’s Dirty Pipe flaw (CVE-2022-0847), Gitea (CVE-2026-60004), Nuclio (CVE-2026-79756), SENAITE LIMS (CVE-2026-54569) and Proxmox VE (CVE-2023-54391).
Threat Actors
Products
FlowiseAIGreyNoise observed targeting of Ubiquiti, PAN-OS GlobalProtect, FlowiseAI, Gitea, Nuclio, SENAITE LIMS, and Proxmox VE.GiteaGreyNoise observed targeting of Ubiquiti, PAN-OS GlobalProtect, FlowiseAI, Gitea, Nuclio, SENAITE LIMS, and Proxmox VE.NuclioGreyNoise observed targeting of Ubiquiti, PAN-OS GlobalProtect, FlowiseAI, Gitea, Nuclio, SENAITE LIMS, and Proxmox VE.PAN-OS GlobalProtectGreyNoise observed attacks against ZyXEL GS1900 switches, Ubiquiti, PAN-OS GlobalProtect, and several other platforms, including intrusions that exposed credentials, PII, and backend database records.Proxmox Virtual EnvironmentGreyNoise observed targeting of Ubiquiti, PAN-OS GlobalProtect, FlowiseAI, Gitea, Nuclio, SENAITE LIMS, and Proxmox VE.SenaiteGreyNoise observed targeting of Ubiquiti, PAN-OS GlobalProtect, FlowiseAI, Gitea, Nuclio, SENAITE LIMS, and Proxmox VE.Ubiquiti UniFi OSAdditionally, the hackers attempted to chain the Ubiquiti UniFi OS vulnerabilities tracked as CVE-2026-34908, CVE-2026-34909, and CVE-2026-34910 to obtain root-level remote code execution.WordPressA Chinese-speaking threat actor linked to the Red Heron group exploited WordPress wp2shell flaws and other vulnerabilities to steal sensitive data from organizations across dozens of countries.Zyxel GS1900 series switchesA Chinese-speaking threat actor has been exploiting vulnerabilities in ZyXEL GS1900 Smart Managed Switches and WordPress to steal sensitive data from 996 devices and more than 18,500 records stored in backend databases.