FedRAMP’s New VDR and VER Rules Require More Frequent Scans and Continuous Validation
Summary
FedRAMP’s VDR and VER rules take effect December 7, 2026, requiring more frequent scans, tiered remediation deadlines, and ongoing validation. The article explains how the rules fit into FedRAMP’s broader transition to continuous, evidence-based compliance.
Key points
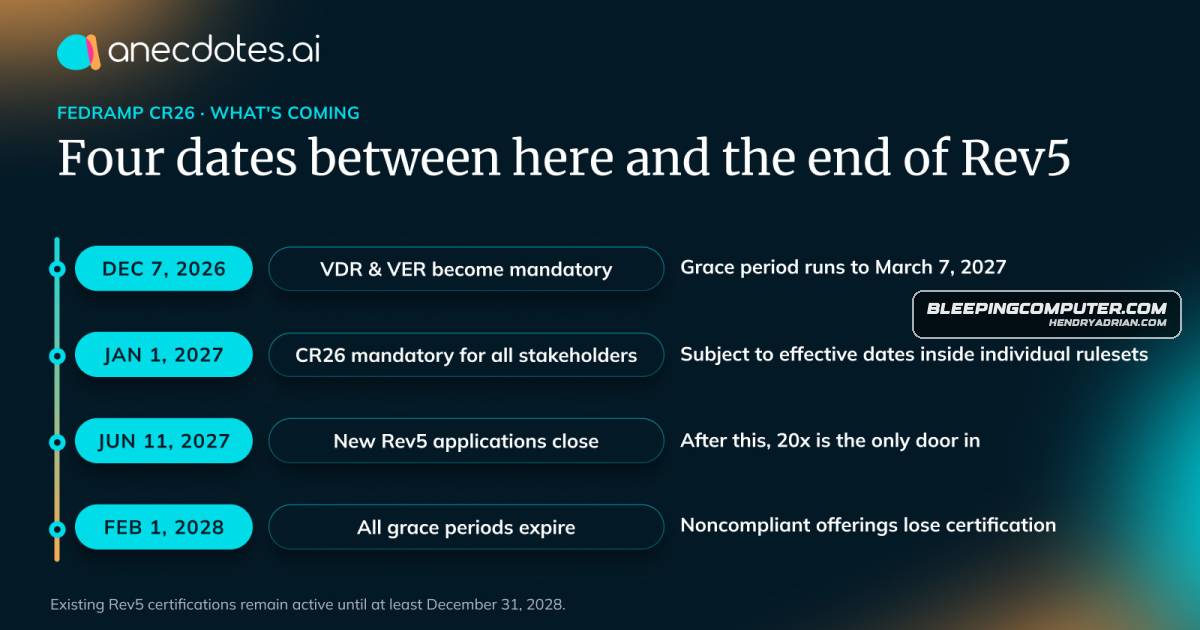
- VDR and VER requirements become mandatory for covered FedRAMP offerings on December 7, 2026; a grace period through March 7, 2027 applies to offerings under a corrective action plan.
- Scanning frequency varies by certification class, from at least every 14 days for Class A machine-based resources to daily for Class D.
- Remediation deadlines depend on vulnerability severity and exploitability, ranging from 192 days to 12 hours in the described cases.
- Providers are expected to assume exploits are automatable unless they have evidence to the contrary, and failures in vulnerability-response processes must themselves be treated as vulnerabilities.
- FedRAMP’s broader transition replaces several document-based processes with ongoing certification and automated, current evidence; new Rev5 applications will no longer be accepted after June 11, 2027.
- The sponsored article recommends building continuous validation from operational systems and assigning ownership for failed validations and changing evidence sources.
Article Details
- Event Type
- FedRAMP regulatory requirements update
- Impact
- FedRAMP’s Vulnerability Detection and Response (VDR) and Vulnerability Enumeration and Reporting (VER) requirements establish more frequent vulnerability scanning, tiered remediation deadlines, a default assumption that exploits are automatable, and a requirement to treat failures in vulnerability detection and response processes as vulnerabilities. The changes require providers to produce persistent, machine-readable evidence of security posture and are part of the transition from Rev5 to FedRAMP 20x.
Vendors
Products
FedRAMP 20xFedRAMP describes it as "a legacy FedRAMP Certification process that is being replaced entirely by FedRAMP 20x," and says providers "are expected to follow new rules and adopt new FedRAMP Practices from FedRAMP 20xFedRAMP Rev5"are expected to follow new rules and adopt new FedRAMP Practices from FedRAMP 20x into their FedRAMP Rev5 Certified cloud service offerings."SOC 2The identity evidence satisfying a FedRAMP indicator is the same evidence a SOC 2 auditor wants and the same evidence a large customer's diligence team asks for.