ASOS Confirms Data Breach After Hackers Send Unauthorized App Alerts
Summary
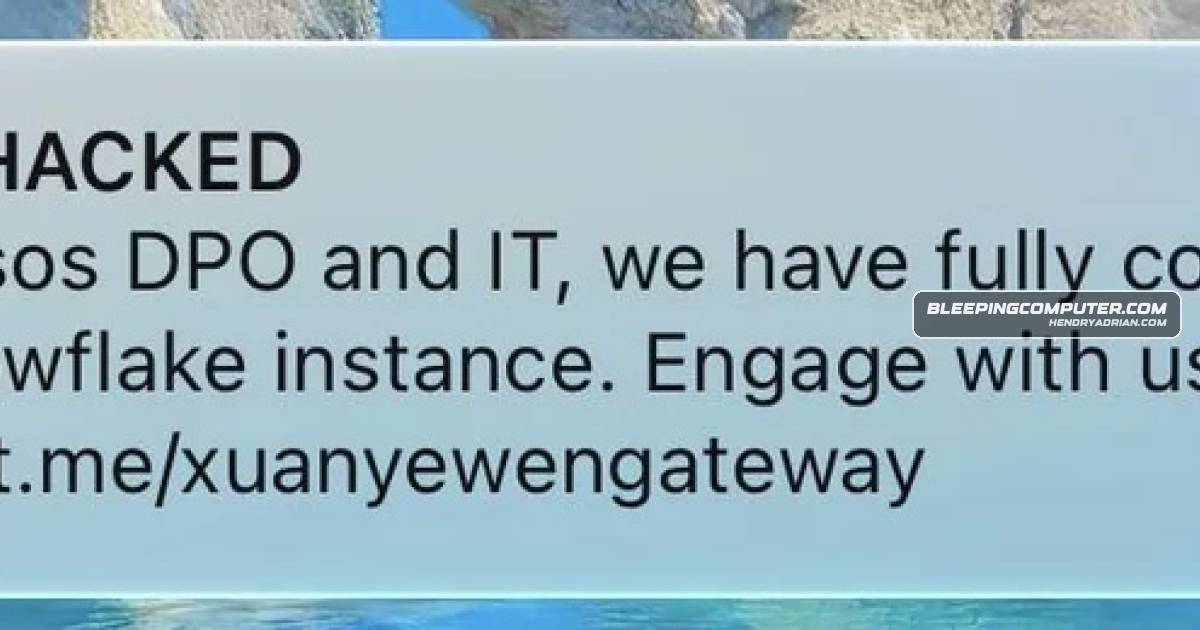
ASOS says attackers accessed third-party customer communication platforms and basic personal information may have been exposed. The company has not confirmed claims that its Snowflake environment was compromised.
Key points
- Hackers sent unauthorized push notifications through ASOS’s mobile app, directing the retailer to a Telegram channel.
- ASOS confirmed unauthorized access to third-party platforms used to communicate with customers.
- Names and contact details may have been exposed; the number of affected customers is unknown.
- The Xuanye group claimed it compromised ASOS’s Snowflake environment and stole customer information, but provided no evidence.
- ASOS says it does not believe payment-card information or account passwords were affected.
- The company is warning app users to ignore the unauthorized alert and avoid its external link.
Article Details
- Victim Organization
- ASOS
- Incident Type
- Unauthorized access to customer-communications platforms and distribution of unauthorized mobile-app push notifications; theft of customer data and compromise of the Snowflake environment are unverified claims.
- Incident Date
- 2026-10-06
- Disclosure Date
- 2026-10-06
- Data Types Exposed
- Names (potentially exposed)
- Contact details (potentially exposed)
- Affected Records
- Not disclosed
- Operational Impact
- Unauthorized push notifications reached ASOS mobile-app users. ASOS displayed an in-app warning advising customers to disregard the notification and avoid its external link. No service outage was reported.
- Ransom Or Extortion
- The notification threatened to leak data unless ASOS engaged with the attackers. No ransom demand or confirmed data leak was reported.
- Claim Status
- confirmed