ShinyHunters Uses URL-Encoding Trick to Bypass WAFs in Oracle PeopleSoft Attacks
Summary
Google says ShinyHunters is encoding PeopleSoft endpoint paths to bypass WAF rules and exploit unpatched CVE-2026-35273 servers, deploying web shells and backdoors. Mandiant urges patching and checking logs for encoded requests.
Key points
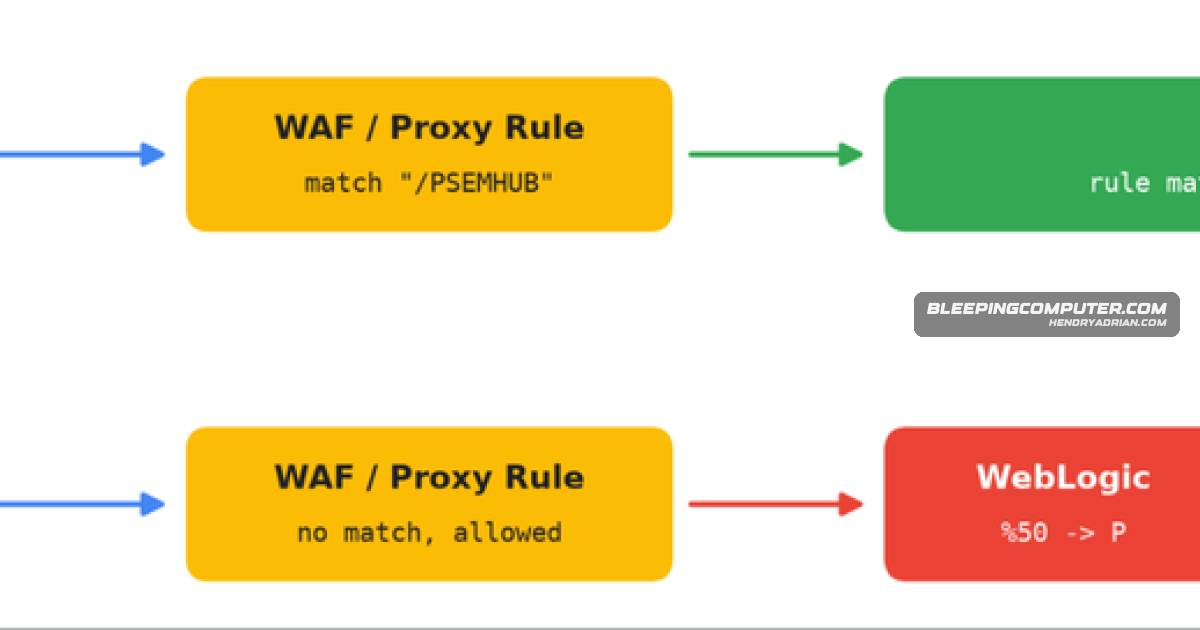
- Google says ShinyHunters, tracked as UNC6240, is using encoded paths such as `/%50SEMHUB/` to bypass WAF rules blocking `/PSEMHUB/`.
- The group is exploiting unpatched Oracle PeopleSoft servers vulnerable to CVE-2026-35273, an unauthenticated remote code execution flaw.
- Mandiant says attackers first send serialized Java objects in POST requests to assess vulnerable systems, then execute commands or deploy JSP web shells.
- On Windows systems, attackers used the shells to deploy SIDEEYE, a backdoor used for credential theft, file and process management, reverse shells, and proxying.
- Attackers also deployed Neo-reGeorg for tunneling and MeshAgent to maintain access to compromised Linux systems.
- Google reports web shells on dozens of systems across sectors including education, technology, healthcare, agriculture, transportation, and government.
- Mandiant recommends installing the latest security update and checking WebLogic access logs for requests to `/PSEMHUB/` and encoded variants.
Article Details
- Attack Vectors
- ShinyHunters bypasses WAF rules by requesting the vulnerable PeopleSoft endpoint with percent-encoded paths such as /%50SEMHUB/ and /%50SEMHUB/hub.
- Before exploitation, the attackers send five to 15 POST requests containing serialized Java objects to assess vulnerable systems.
- The attackers exploit CVE-2026-35273 to execute commands in memory or deploy JSP web shells, including x.jsp, u.jsp, and u2.jsp.
- On compromised Windows servers, Ple64.exe installs the SIDEEYE backdoor; Neo-reGeorg tunnels SOCKS5 traffic over HTTP and HTTPS for lateral movement.
- The attackers used MeshAgent on compromised Linux systems to maintain access.
- Defensive Notes
- Install the latest Oracle PeopleSoft security update for CVE-2026-35273 rather than relying on WAF rules.
- Search WebLogic access logs for requests to /PSEMHUB/ and encoded variants such as /%50SEMHUB/.
- Review exposed PeopleSoft systems for exploitation, web shells, SIDEEYE, Neo-reGeorg, and unauthorized MeshAgent use.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| HOSTNAME | ple64[.]exe | Executable deployed on compromised Windows servers that installs the SIDEEYE backdoor. |
| HOSTNAME | tunnel[.]jsp | File used to deploy the Neo-reGeorg tunneling toolkit on compromised systems. |
| HOSTNAME | tunnel[.]jspx | File used to deploy the Neo-reGeorg tunneling toolkit on compromised systems. |
| HOSTNAME | u[.]jsp | JSP shell deployed to upload larger files. |
| HOSTNAME | u2[.]jsp | JSP shell deployed to upload larger files. |
| HOSTNAME | x[.]jsp | JSP web shell deployed for command execution on compromised systems. |
MITRE ATT&CK
T1059 · Command and Scripting InterpreterThe attackers use deployed JSP web shells to execute commands on compromised servers.T1071.001 · Web ProtocolsNeo-reGeorg tunnels SOCKS5 proxy traffic over HTTP and HTTPS connections.T1078 · Valid AccountsSIDEEYE is used to steal credentials from compromised systems.T1090 · ProxyNeo-reGeorg provides proxy tunneling through compromised PeopleSoft servers for lateral movement.T1105 · Ingress Tool TransferThe attackers use u.jsp and u2.jsp shells to upload larger files, including the Ple64.exe executable.T1190 · Exploit Public-Facing ApplicationShinyHunters exploits the internet-facing Oracle PeopleSoft CVE-2026-35273 vulnerability through the PSEMHUB endpoint.T1505.003 · Web ShellThe attackers deploy JSP web shells, including x.jsp, u.jsp, and u2.jsp.
CVE
People
Threat Actors
Malware
Vendors
Products
AWS GovCloudcode execution and was used to access the FBI Jobs platform, then spread laterally into the FBI’s AWS GovCloud infrastructure.Oracle PeopleSoftShinyHunters is using a URL-encoding trick to bypass WAF rules and keep exploiting Oracle PeopleSoft CVE-2026-35273 on unpatched servers.Oracle WebLogicOracle WebLogic, on the other hand, decodes the encoded ‘P’ and routes the request to the vulnerable endpoint, bypassing the WAF rule.
Tools
Industries
AgricultureGoogle says the new wave of attacks has deployed web shells on dozens of systems worldwide within higher education, technology, IT services, healthcare, agriculture, transportation, and government organizations.GovernmentThe group is deploying web shells and backdoors to steal data, move laterally, and maintain access across multiple sectors, including higher education and government.HealthcareGoogle says the attacks are hitting education, technology, healthcare, and government targets.Higher EducationThe group is deploying web shells and backdoors to steal data, move laterally, and maintain access across multiple sectors, including higher education and government.IT servicesGoogle says the new wave of attacks has deployed web shells on dozens of systems worldwide within higher education, technology, IT services, healthcare, agriculture, transportation, and government organizations.TechnologyGoogle says the attacks are hitting education, technology, healthcare, and government targets.TransportationGoogle says the new wave of attacks has deployed web shells on dozens of systems worldwide within higher education, technology, IT services, healthcare, agriculture, transportation, and government organizations.