
Two Compromised GitHub Actions Re-Enabled With Malicious Payloads for Over a Week
Summary
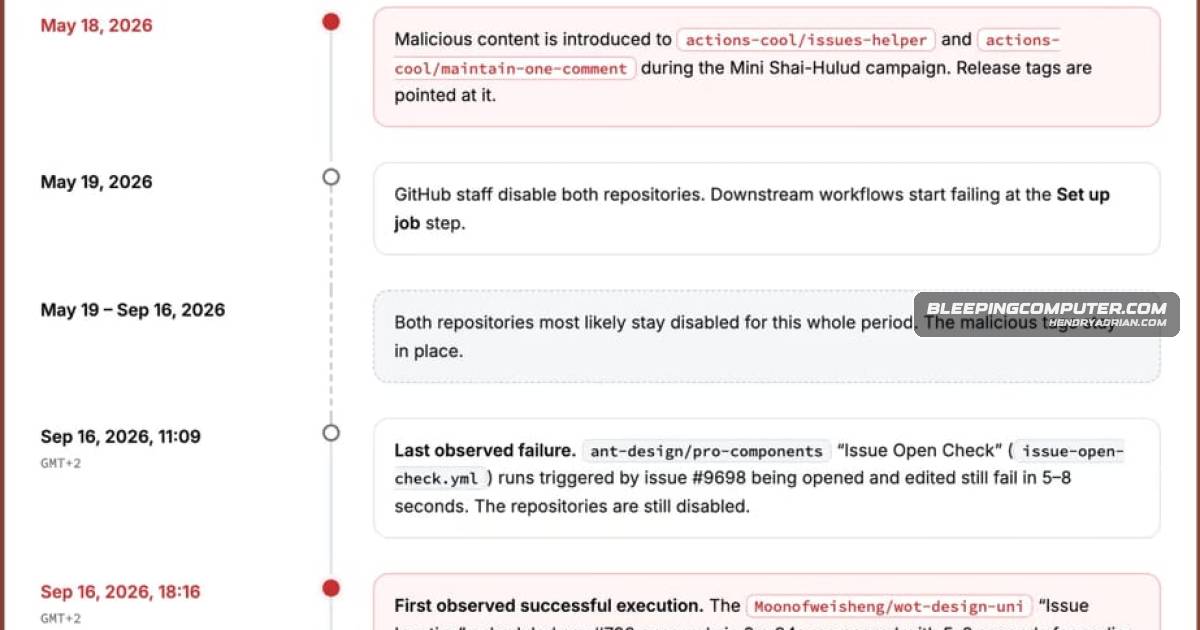
Two GitHub Actions compromised in the Mini Shai-Hulud campaign were re-enabled from September 16 to 25, 2026, with malicious tags still active. Socket advised removing or pinning them, reviewing workflow runs, and rotating exposed secrets.
Key points
- The actions-cool/issues-helper and actions-cool/maintain-one-comment repositories were re-enabled with release tags still pointing to malicious code introduced on May 18.
- From September 16 through September 25, workflows referencing either action by a version tag could download and run the payload; the number of affected workflows is unknown.
- The payload was in an obfuscated index.js file. The malware targeted developer tokens, credentials, and CI/CD secrets.
- Socket said GitHub’s dependency graph listed about 15,000 repositories depending on issues-helper, but that does not mean they were compromised.
- GitHub disabled both actions again on September 25, causing workflows referencing them to fail rather than run the payload.
- Socket advised finding references to both actions, removing them or pinning a verified clean commit, reviewing workflow runs since September 16, and rotating secrets accessible to affected runs.
Article Details
- Event Type
- Supply-chain security incident involving two compromised GitHub Actions that were re-enabled while their release tags still pointed to malicious code.
- Impact
- From September 16 to September 25, 2026, workflows referencing actions-cool/issues-helper or actions-cool/maintain-one-comment by mutable release tag could download and execute the Mini Shai-Hulud payload. Developer tokens, credentials, and CI/CD secrets accessible to those workflows were at risk; the number of affected workflows or compromised developers was not established.
Malware
Vendors
Products
GitHub ActionsTwo GitHub Actions, actions-cool/issues-helper and actions-cool/maintain-one-comment, were re-enabled after a Mini Shai-Hulud compromise and continued serving malicious code for more than a week.npmThe original Mini Shai-Hulud campaign affected 323 npm packages and 639 package versions.