
BYOD Claims Trump Mobile Customer Data Breach Exposed 3,615 People
Summary
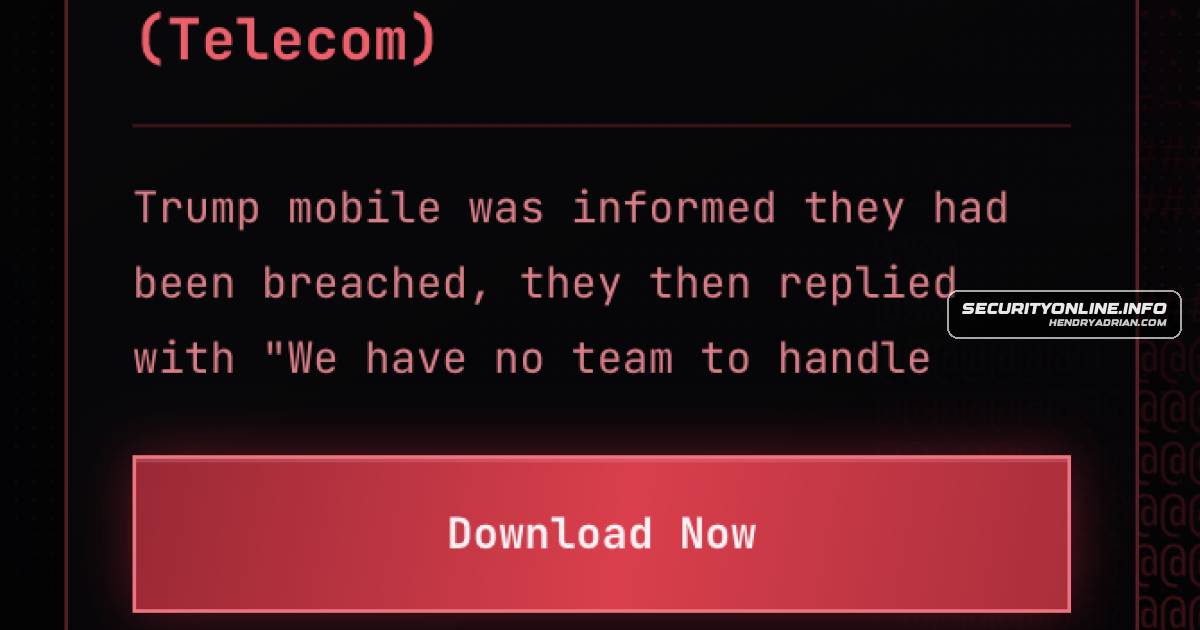
The BYOD gang claims it published data on 3,615 Trump Mobile customers, including contact details, home addresses and order information. Reporters verified some records; Trump Mobile has not confirmed the breach.
Key points
- BYOD claims 3,615 customers were affected; reporters say some people listed confirmed their details, but the full count has not been verified.
- The published data reportedly includes names, email addresses, phone numbers, home addresses and order details.
- BYOD alleges it reached Trump Mobile systems after infecting a Liberty Mobile employee with an infostealer; the account has not been independently confirmed.
- The attackers also claim neither company used MFA and that they still have access to Trump Mobile’s backend; these claims are unverified.
- Trump Mobile has not publicly confirmed the breach or responded to a reporter before publication.
- Affected customers are advised to watch for targeted phishing and SIM-swap attempts, add a carrier account PIN, and enable MFA on email and carrier accounts.
Article Details
- Victim Organization
- Trump Mobile
- Incident Type
- Alleged unauthorized access through a partner employee's infostealer infection, followed by publication of customer data
- Data Types Exposed
- Names
- Email addresses
- Phone numbers
- Home addresses
- Order details
- Telecom details, according to BYOD
- Affected Records
- 3,615 customers claimed by BYOD; reporters corroborated details for some people in the data, but the full count was not verified.
- Operational Impact
- BYOD claims it still has access to Trump Mobile's backend; this has not been independently confirmed. No service disruption was reported.
- Ransom Or Extortion
- BYOD published customer data on its leak site. No ransom demand was reported.
- Claim Status
- claimed
People
Bo LoudonInfluencer named by International Cyber Digest as appearing in the leaked customer data.Charlie ErgenEchoStar cofounder named by International Cyber Digest as appearing in the leaked customer data.Jason MillerAdviser named by International Cyber Digest as appearing in the leaked customer data.Larry GatlinSinger named by International Cyber Digest as appearing in the leaked customer data.Mike KellyCongressman named by International Cyber Digest as appearing in the leaked customer data.