
CISA Orders Federal Agencies to Patch Actively Exploited Citrix NetScaler Flaws
Summary
CISA ordered U.S. federal agencies to secure NetScaler systems affected by two actively exploited flaws that can enable unauthenticated remote code execution. Citrix urged immediate patching and compromise checks before updates.
Key points
- Citrix confirmed zero-day exploitation of CVE-2026-88771 and CVE-2026-88772 in unmitigated NetScaler deployments.
- Both flaws can allow unauthenticated remote code execution; one affects default configurations, while the other requires DTLS to be enabled.
- Citrix released security updates and urged affected customers to patch promptly.
- CISA added both flaws to its KEV Catalog and directed federal civilian agencies to secure vulnerable appliances by September 30 under BOD 26-04.
- Citrix and CISA advised checking for compromise and preserving forensic evidence before patching; Citrix cautioned that its generic indicators may have limited forensic value.
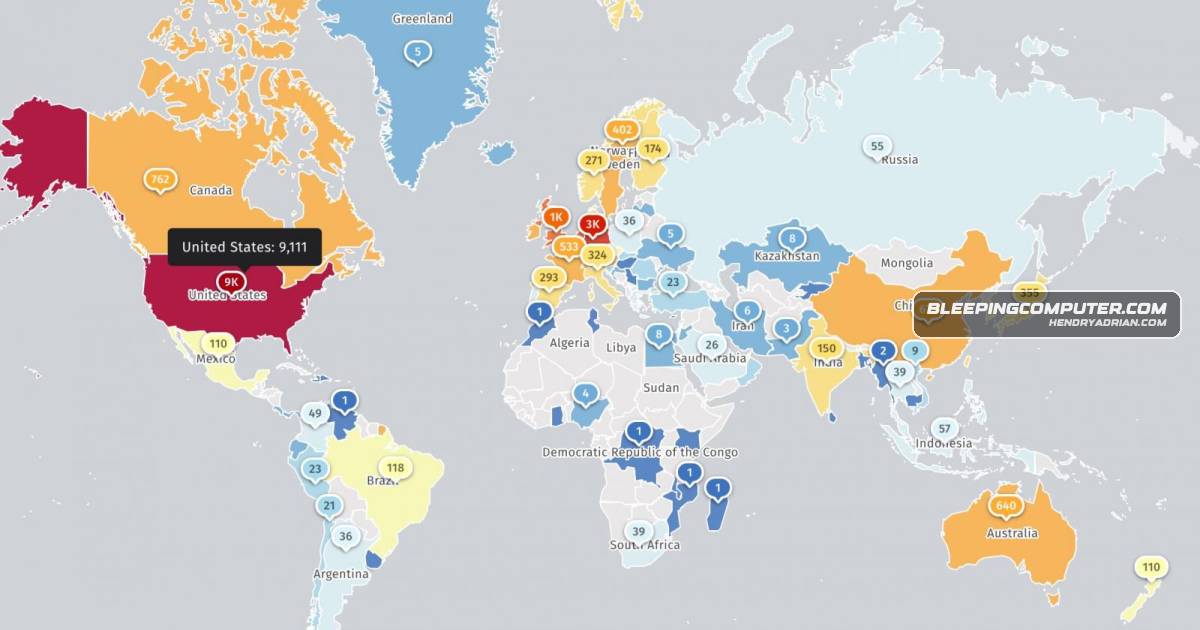
- Shadowserver tracked more than 23,000 internet-exposed NetScaler IP addresses, but the article notes that the number of vulnerable systems is unknown.
Article Details
- Vulnerability Types
- Unauthenticated remote code execution
- Severity
- Critical
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
CVE
CVE-2026-88771Citrix NetScaler · ADC; Citrix NetScaler · Gatewayfederal agencies to secure vulnerable Citrix NetScaler systems after active exploitation of two critical flaws, CVE-2026-88771 and CVE-2026-88772.CVE-2026-88772Citrix NetScaler · ADC; Citrix NetScaler · Gatewayfederal agencies to secure vulnerable Citrix NetScaler systems after active exploitation of two critical flaws, CVE-2026-88771 and CVE-2026-88772.
Vendors
Products
NetScaler ADCThe first affects all NetScaler ADC and NetScaler Gateway deployments with default configurations, while the second requires DTLS to be enabled (Citrix noted that DTLS is toggled on by default on VPN virtual servers).NetScaler GatewayThe first affects all NetScaler ADC and NetScaler Gateway deployments with default configurations, while the second requires DTLS to be enabled (Citrix noted that DTLS is toggled on by default on VPN virtual servers).