Misconfigured Supabase Databases Exposed Sensitive Data at More Than 16,000 Sites
Summary
UpGuard found more than 16,000 misconfigured Supabase databases exposing sensitive data. Reported cases included customer records, plaintext passwords, private messages and SMS; researchers linked the exposures to configuration errors but said scans did not prove AI use
Key points
- UpGuard identified more than 16,000 misconfigured Supabase databases exposing readable tables after analyzing about 300,000 domains.
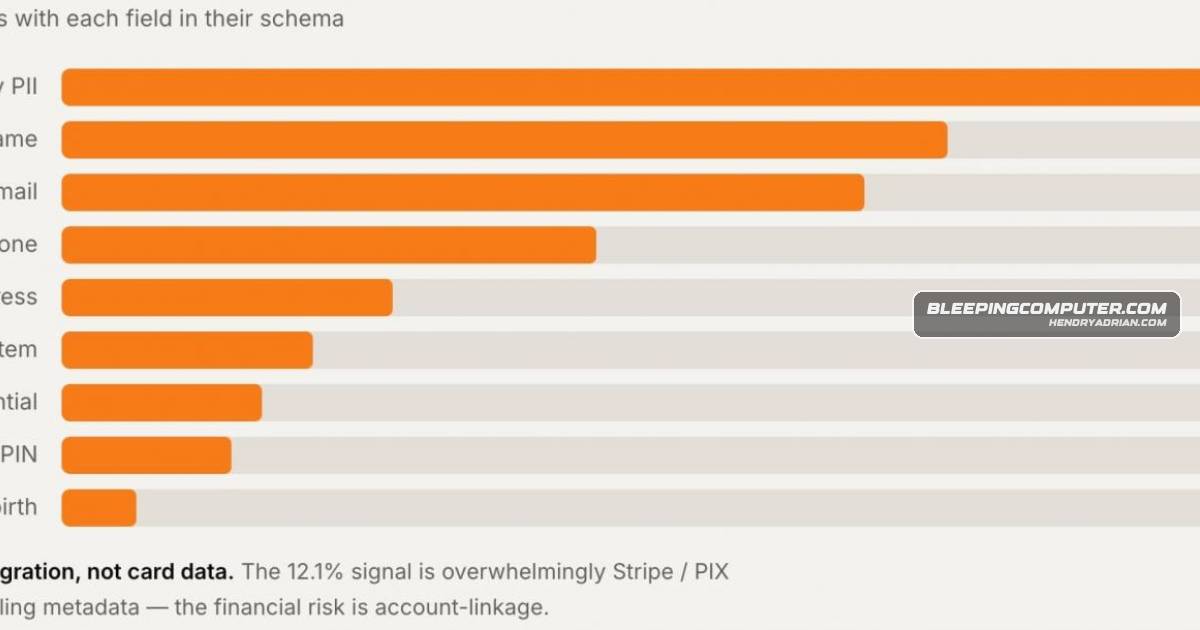
- Exposed data included PII, passwords and authentication tokens; researchers inferred that a small subset of exposed information included credit card data.
- Reported cases included a U.S. valet service with over 100,000 customer records and a Canadian immigration service with nearly 5,000 user records, including 884 plaintext passwords.
- Other reported exposures included private messages and identity and payment information at an India-based adult creator platform, SMS records at a Philippines-based OTP service, and records belonging to 25,000 people at an African government consulate.
- UpGuard attributed the exposures to weak application security configuration, including missing or ineffective row-level security and misuse of public keys.
- Researchers said the scans did not establish that every affected site was built using AI coding agents. UpGuard said it notified owners when deeper analysis identified significant exposure.
- Supabase users were advised to review the platform's security documentation, advisors and API security guide.
Article Details
- Victim Organization
- Multiple application owners using Supabase
- Incident Type
- Exposure of data from misconfigured Supabase databases
- Data Types Exposed
- Personally identifiable information
- Passwords, including plaintext passwords
- Authentication tokens
- Credit card information in a very small subset
- Contact details
- License plates
- Visit history
- Private messages
- SMS messages
- Addresses
- Emergency housing locations
- Affected Records
- More than 16,000 databases were found misconfigured. Specific reported exposures included more than 100,000 customer records at a U.S. valet service, nearly 5,000 user records at a Canadian immigration service, more than 2,000 users at a Philippines-based OTP service, and records belonging to 25,000 people at an African government consulate. UpGuard also reported 100,000 private messages at an India-based adult creator platform and 100,000 SMS messages at the Philippines-based service.
- Operational Impact
- Readable database tables exposed sensitive information. No service disruption was reported.
- Ransom Or Extortion
- None reported
- Claim Status
- confirmed
Vendors
SupabaseResearchers found more than 16,000 misconfigured Supabase databases exposing readable tables with sensitive data such as PII, passwords, authentication tokens, and in some cases credit card information.UpGuardUpGuard linked the exposure to weak configuration practices in AI-assisted app development and advised users to review Supabase security controls to reduce risk.