
ThreeAM Claims Ransomware Attack on Colombia’s Coosalud Health Entity
Summary
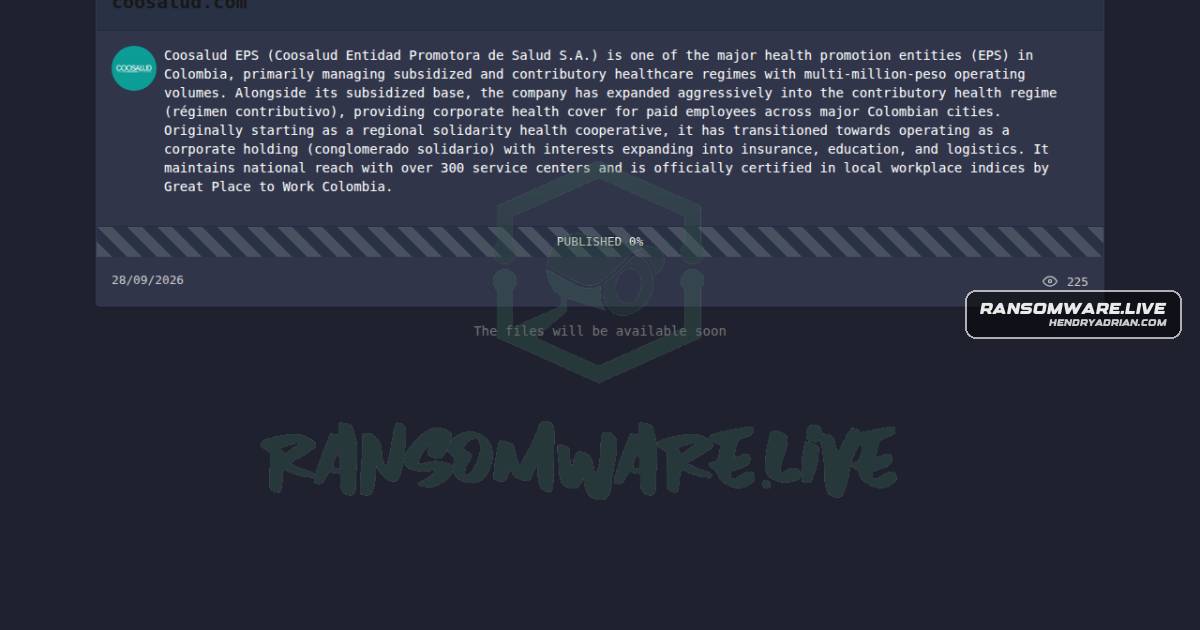
Ransomware.live records a ThreeAM ransomware claim involving Colombia’s Coosalud health entity and says the attack disrupted healthcare operations. The post says the claim is unconfirmed.
Key points
- The post identifies Coosalud EPS in Colombia as the claimed victim and ThreeAM as the actor.
- The post says the attack disrupted the organization’s healthcare operations, but attributes this to public claims by the ransomware group.
- The claim was published and discovered on September 28, 2026, according to the record.
- The post provides a ThreeAM claim link: hxxp://threeamkelxicjsaf2czjyz2lc4q3ngqkxhhlexyfcp2o6raw4rphyad[.]onion/detail/g1gj1po6yas5yjoct7hzsljghcw6ux.
- The post says it cannot confirm the claim’s accuracy and invites an official statement from Coosalud.
Article Details
- Victim
- Coosalud EPS (Coosalud Entidad Promotora de Salud S.A.)
- Victim Domain
- coosalud.com
- Claim Date
- 2026-09-28
- Encryption Status
- Unknown; the source does not confirm encryption.
- Exfiltration Status
- Unknown; the source does not confirm exfiltration.
- Leak Status
- The source reports a public ransomware-group claim but says it cannot confirm the claim's accuracy.