Microsoft and Partners Disrupt Three Phishing Kits Linked to Over 1 Billion Messages
Summary
Microsoft and partners announced a court-authorized disruption of CoGUI, Haozi and Iron Man System. Microsoft says operators behind the kits facilitated more than 1 billion phishing emails and SMS messages since January 2026.
Key points
- Microsoft, Health-ISAC, JC3 and private-sector partners announced the disruption after an investigation that began in late 2025 following phishing campaigns targeting people in Japan.
- Microsoft says the kits' operators facilitated more than 1 billion phishing emails and SMS messages to over 75,000 organizations since January 2026.
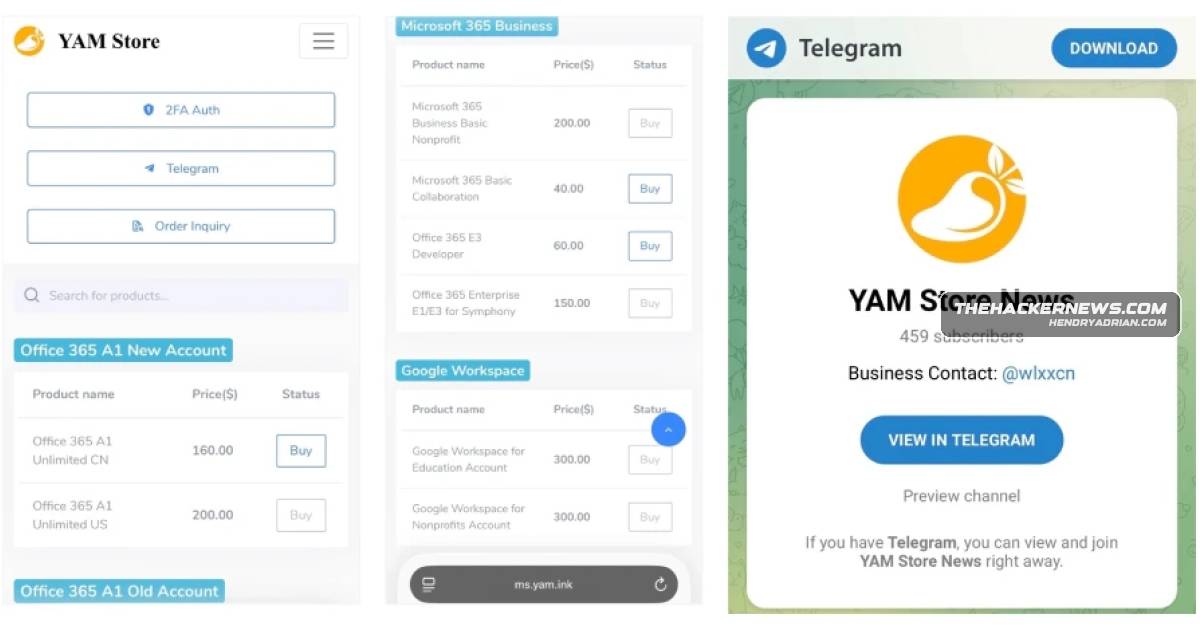
- The kits were advertised through YAM Store, which Microsoft tracks as Storm-3119; Microsoft tracks the developers as Storm-2990.
- The kits impersonated brands and organizations across sectors and countries, and were used to steal credentials and financial information.
- Iron Man System reportedly offered thousands of phishing templates. Resecurity said its lab analysis found the kit depended on regular contact with a licensing server, which could give defenders a disruption opportunity.
- Reported evasion features included fake CAPTCHA checks, IP-based filtering and Telegram alerts; captured information was sent over WebSocket.
Article Details
- Event Type
- Court-authorized disruption of three phishing kits and associated criminal infrastructure.
- Impact
- Microsoft and partners said the operators behind the kits facilitated more than one billion phishing emails and SMS messages targeting over 75,000 organizations since January 2026. The kits were used to steal credentials and financial information from targets worldwide, including organizations in healthcare, financial services, wholesale distribution, and IT.
People
Threat Actors
Vendors
CloudflareJapan Cybercrime Control Center (JC3) and a coalition of private sector companies, such as Resecurity, Cloudflare, Oracle, Proofpoint, and TRM Labs, announced the disruption of three phishing kits, CoGUI (aka NX orHealth-ISACMicrosoft and Health-ISAC, along with the Japan Cybercrime Control Center (JC3) and a coalition of private sector companies, such as Resecurity, Cloudflare, Oracle, Proofpoint, and TRM Labs, announced the disruption ofMicrosoftMicrosoft and Health-ISAC, along with the Japan Cybercrime Control Center (JC3) and a coalition of private sector companies, such as Resecurity, Cloudflare, Oracle, Proofpoint, and TRM Labs, announced the disruption ofOracleControl Center (JC3) and a coalition of private sector companies, such as Resecurity, Cloudflare, Oracle, Proofpoint, and TRM Labs, announced the disruption of three phishing kits, CoGUI (aka NX or FA), HaoziProofpointCenter (JC3) and a coalition of private sector companies, such as Resecurity, Cloudflare, Oracle, Proofpoint, and TRM Labs, announced the disruption of three phishing kits, CoGUI (aka NX or FA), Haozi (akaResecuritywith the Japan Cybercrime Control Center (JC3) and a coalition of private sector companies, such as Resecurity, Cloudflare, Oracle, Proofpoint, and TRM Labs, announced the disruption of three phishing kits, CoGUITRM Labsand a coalition of private sector companies, such as Resecurity, Cloudflare, Oracle, Proofpoint, and TRM Labs, announced the disruption of three phishing kits, CoGUI (aka NX or FA), Haozi (aka Phoenix), and Iron
Tools
CoGUICloudflare, Oracle, Proofpoint, and TRM Labs, announced the disruption of three phishing kits, CoGUI (aka NX or FA), Haozi (aka Phoenix), and Iron Man System.HaoziOracle, Proofpoint, and TRM Labs, announced the disruption of three phishing kits, CoGUI (aka NX or FA), Haozi (aka Phoenix), and Iron Man System.Iron Man Systemannounced the disruption of three phishing kits, CoGUI (aka NX or FA), Haozi (aka Phoenix), and Iron Man System.
Countries
Australiafinancial services, wholesale distribution, and information technology (IT) sectors in Japan, the U.S., Australia, and India.Indiawholesale distribution, and information technology (IT) sectors in Japan, the U.S., Australia, and India.JapanMicrosoft and Health-ISAC, along with the Japan Cybercrime Control Center (JC3) and a coalition of private sector companies, such as Resecurity, Cloudflare, Oracle, Proofpoint, and TRM Labs, announced the disruption ofUnited Statesfinancial services, wholesale distribution, and information technology (IT) sectors in Japan, the U.S., Australia, and India.
Industries
Financial Servicesfraudulent Microsoft or Google cloud environments, to target organizations across the healthcare, financial services, wholesale distribution, and information technology (IT) sectors in Japan, the U.S., Australia, andHealthcare"These messages have been used to target consumers, healthcare organizations, financial institutions, and other businesses in more than 150 countries, generating tens of millions of dollars for their operators,"Information Technologyto target organizations across the healthcare, financial services, wholesale distribution, and information technology (IT) sectors in Japan, the U.S., Australia, and India.Wholesale distributionor Google cloud environments, to target organizations across the healthcare, financial services, wholesale distribution, and information technology (IT) sectors in Japan, the U.S., Australia, and India.