
Study Finds 543,699 Valid Credentials Exposed in Public GitHub Repositories
Summary
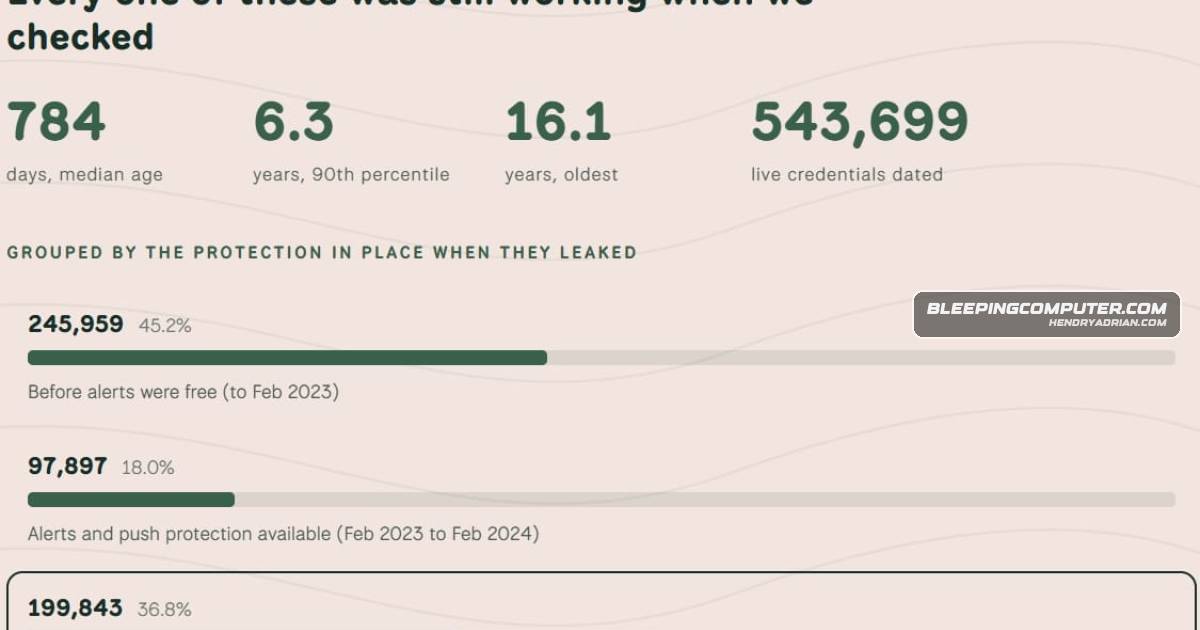
Truffle Security found 543,699 valid credentials in public GitHub repositories. Many remained exposed for years; over half fell outside GitHub Push Protection’s default coverage, though protected credential types saw fewer exposures.
Key points
- Researchers found 543,699 unique valid credentials across more than 1.1 million files and repositories, from a crawl of 224 million repositories and over 58 billion files.
- The median exposure period was 784 days; about 10% of working credentials were more than 6.3 years old, and the oldest dated to 2009.
- Some 199,843 credentials, or 36.8% of the total, were exposed after GitHub enabled Push Protection by default in February 2024.
- A total of 51.8% of live credentials were types not blocked by default Push Protection, including database connection strings and Google API keys.
- For credential types covered by the safeguard, exposure rates fell 53% after it was enabled by default.
- Researchers recommend rotating exposed credentials, cleaning repositories, scanning repository history, and setting automatic expiration for active secrets.
- The study does not establish what proportion of the exposed credentials were stolen or abused.
Article Details
- Publisher
- BleepingComputer
- Report Period
- July 2025; dataset crawl closed on 2025-08-07
- Scope
- Valid credentials exposed in public GitHub repositories.
- Sample Size
- 224 million repositories and more than 58 billion files scanned.
- Key Statistics
- 543,699 unique valid credentials were identified across more than 1.1 million files and repositories, including copies in forks.
- The median time a unique credential remained publicly accessible was 784 days.
- 199,843 credentials (about 36.8% of the total) were exposed after Push Protection was enabled by default.
- 51.8% of live credentials were types not blocked by default Push Protection.
- About 10% of working credentials were older than 6.3 years; the oldest dated to 2009.
- Recommendations
- Immediately rotate exposed credentials.
- Clean up repositories containing exposed credentials.
- Scan repository history for exposed credentials.
- Set automatic expiration for active secrets.
Vendors
Products
Google CloudIn contrast, out of 126,963 exposed Google Cloud service account credentials, 69,041 were still valid and working at the time of the analysis.Push ProtectionThe study shows that Push Protection reduced some exposures, but many live secrets still fall outside its coverage, including database strings and Google API keys.