
Bitget Says Third-Party Zero-Day Enabled $387.5 Million Wallet Theft
Summary
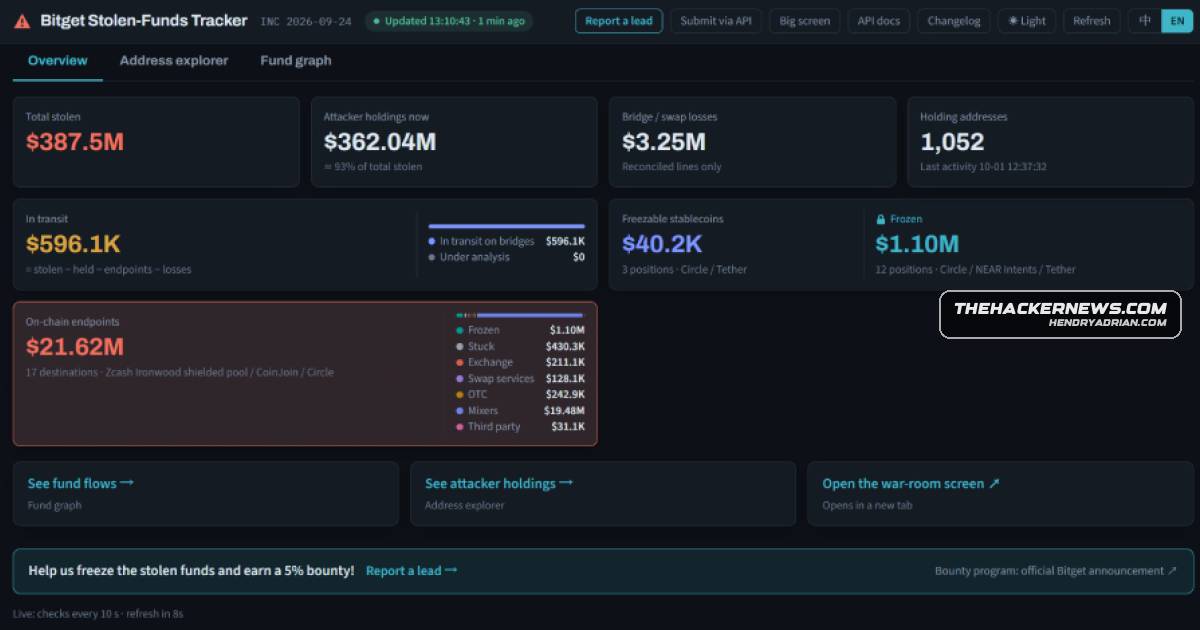
Bitget says attackers exploited a zero-day in third-party security products to access its wallet environment and steal $387.5 million across 11 blockchains. The exchange disabled affected functionality; some assets were frozen.
Key points
- Attackers made unauthorized withdrawals totaling $387.5 million from Bitget’s hot and warm wallets.
- Investigators say a zero-day in third-party security products enabled access, credential theft, and lateral movement into Bitget’s wallet environment.
- SlowMist traced malicious activity to August 31, 2026, and found a custom tool tailored to the wallet system’s withdrawal logic.
- The theft affected assets across 11 blockchains, including Ethereum, XRP Ledger, TRON, and BNB Smart Chain.
- Bitget and Mandiant linked the operation to North Korean threat actors.
- Bitget disabled the affected functionality pending a fix; Circle, Tether, and NEAR Intents froze about $632,700 in assets.
Article Details
- Victim Organization
- Bitget
- Incident Type
- Zero-day exploitation of third-party security products, followed by lateral movement into Bitget’s wallet environment and cryptocurrency theft.
- Incident Date
- 2026-09-25
- Disclosure Date
- 2026-09-24
- Operational Impact
- Attackers stole $387.5 million in cryptocurrency from Bitget’s hot and warm wallets. Bitget temporarily halted withdrawals. Approximately $632,700 in cryptocurrency assets were frozen by Circle, Tether, and NEAR Intents.
- Ransom Or Extortion
- None reported; the incident involved cryptocurrency theft.
- Claim Status
- confirmed