Silent Push 6.2 Adds Granular Access Controls and Threat-Intelligence Integrations
Summary
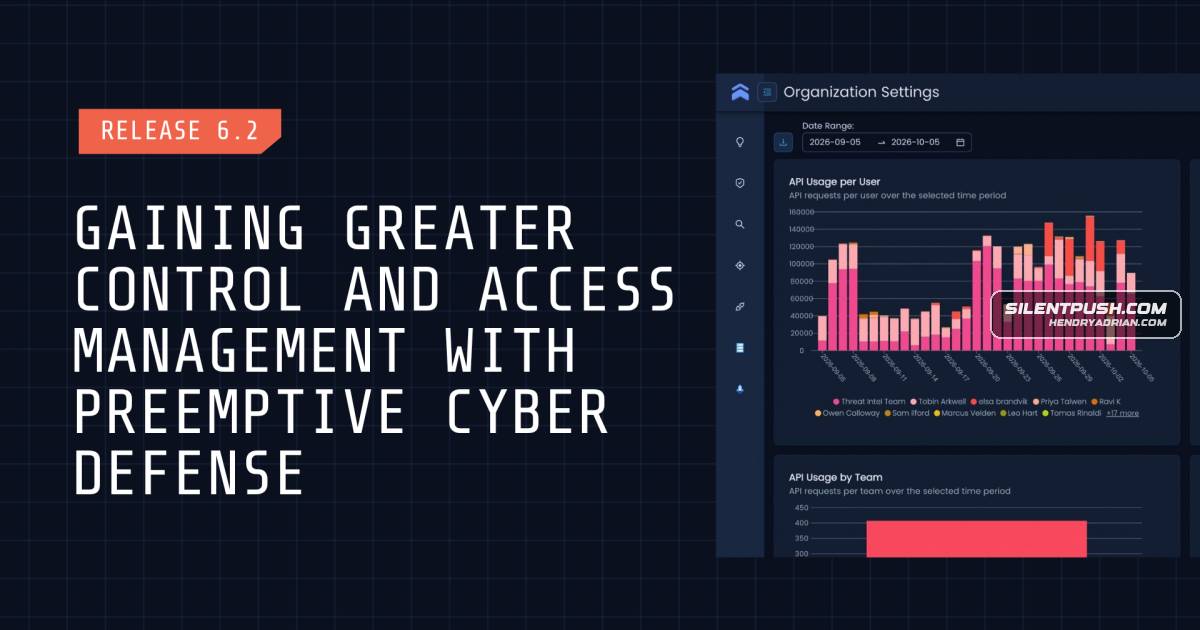
Silent Push 6.2 adds team-based module permissions and per-user API limits, and brings its IOFA and Traffic Origin intelligence checks to ThreatConnect, Microsoft Sentinel, and Palo Alto Cortex XSOAR.
Key points
- Administrators can create teams, assign users, grant module access, and set daily and monthly API limits per user.
- Managers can view their own team’s users and API keys; members can view only their own keys.
- IOFA Threat Check identifies IPs or domains linked to infrastructure Silent Push flags as potential future threats.
- Traffic Origin Threat Check provides source IP, geographic, and traffic-pattern context for internet-facing infrastructure.
- The release adds or updates integrations for ThreatConnect, Microsoft Sentinel via a connector and Logic Apps app, and Palo Alto Cortex XSOAR.
- The XSOAR integration adds Traffic Origin support and an API for finding and retrieving available TLP Amber reports.
Article Details
- Event Type
- Product release and security-platform integration update
- Impact
- Silent Push says version 6.2 gives administrators centralized control over user access, module permissions, and API usage limits. Its updated integrations let analysts access threat intelligence within existing investigation and response workflows.
People
Vendors
MicrosoftSilent Push 6.2 lets admins easily select users, usage, and defensive intelligence levels from a single page and deploys the platform within ThreatConnect, Microsoft Sentinel, and Palo Alto Cortex XSOAR.Silent PushSilent Push 6.2 lets admins easily select users, usage, and defensive intelligence levels from a single page and deploys the platform within ThreatConnect, Microsoft Sentinel, and Palo Alto Cortex XSOAR.
Products
Microsoft Logic AppsThrough Microsoft Logic Apps, analysts call Silent Push APIs to enrich indicators, speed investigations, and automate security workflows.Microsoft SentinelSilent Push 6.2 lets admins easily select users, usage, and defensive intelligence levels from a single page and deploys the platform within ThreatConnect, Microsoft Sentinel, and Palo Alto Cortex XSOAR.Palo Alto Cortex XSOARSilent Push 6.2 lets admins easily select users, usage, and defensive intelligence levels from a single page and deploys the platform within ThreatConnect, Microsoft Sentinel, and Palo Alto Cortex XSOAR.Silent Push PlatformSilent Push Platform, version 6.2, Organization SettingsThreatConnectSilent Push 6.2 lets admins easily select users, usage, and defensive intelligence levels from a single page and deploys the platform within ThreatConnect, Microsoft Sentinel, and Palo Alto Cortex XSOAR.