Attackers Used a Compromised Terminal Server to Stage a Boots Phishing Campaign
Summary
Huntress traced attackers’ use of stolen credentials to access an exposed terminal server, stage bulk-mail software and 8.9 million addresses, and run a Boots phishing campaign hosted on a compromised Bolivian government site.
Key points
- Attackers accessed an internet-facing RDWeb portal using a valid domain credential; the server had no MFA, and logs showed successful logins from Romanian IPs.
- The server held Gammadyne Mailer, a campaign file, and six recipient lists totaling 8,894,920 email addresses.
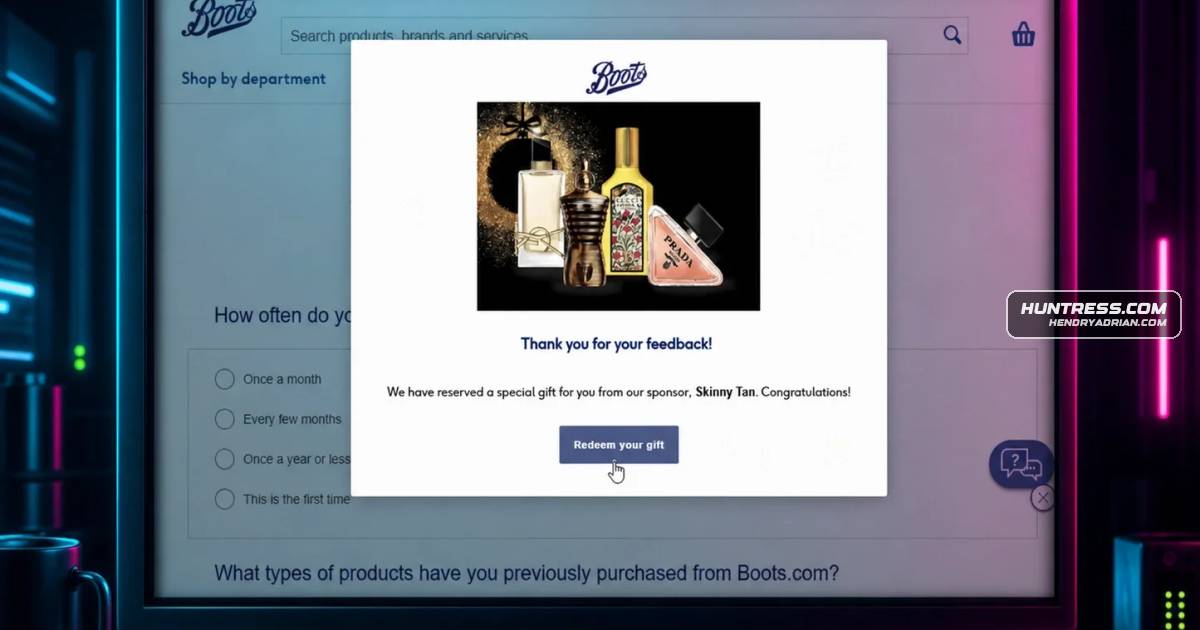
- The phishing campaign impersonated UK retailer Boots and used a fake survey and free-gift offer to solicit personal details and payment-card information.
- The phishing kit was hosted at hxxps://ipelc.gob[.]bo/boots_store/ on a compromised Bolivian government website; Huntress notified Bolivia’s national CSIRT.
- The mailer was configured for direct-to-MX delivery, bypassing the customer’s mail tenant and sending from the compromised server’s IP.
- After isolation, security controls blocked 29,954 outbound SMTP connection attempts in 104 seconds; earlier sending could not be quantified.
- Huntress isolated all 25 endpoints, severed the RDP session, and advised resetting the compromised credentials.
Article Details
- Attack Vectors
- The operator used a valid domain credential to access an internet-facing RDWeb portal and reconnect through the RD Gateway to an existing RDP session.
- A separate, opportunistic source repeatedly attempted logins against the RDWeb portal; one attempt validated the published credential but did not proceed to open a session.
- The operator staged Gammadyne Mailer and recipient lists on the compromised terminal server to send a Boots-impersonation phishing campaign.
- Phishing emails linked to a Boots-branded survey and checkout kit hosted in a subdirectory of a compromised Bolivian government website.
- Gammadyne Mailer was configured for direct-to-MX delivery, attempting outbound SMTP connections from the compromised terminal server.
- Defensive Notes
- Huntress isolated all 25 endpoints, severed the RDP session, and blocked further inbound connections and outbound SMTP attempts.
- The compromised account was flagged for credential reset at the domain controller.
- The article identifies the absence of MFA on the internet-facing remote-access portal as a material risk.
- Huntress notified Bolivia's national CSIRT that the government website had been compromised and was serving a phishing kit.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 212[.]93[.]152[.]37 | Operator source IP used for RDWeb login and RDP session access to the compromised terminal server. |
| IPV4 | 216[.]152[.]151[.]168 | Separate opportunistic source that brute-forced the RDWeb portal and validated the credential once. |
| IPV4 | 80[.]94[.]95[.]37 | Earlier operator source IP used to log in to RDWeb and access the published RDP session. |
| IPV4 | 87[.]251[.]64[.]134 | High-volume source of brute-force requests against the RDWeb portal. |
| SHA256 | 13ac78f8f2ed76a03c85f0cdef07e5463aa64458303c0949090fcd81868ba8ca | Hash of milk (5).txt, a recipient list staged for the phishing campaign. |
| SHA256 | 375c2c84e2ca022c565507523b75c9c08a455479861ea41fc9b9ff74b3453445 | Hash of milk (6).txt, a recipient list staged for the phishing campaign. |
| SHA256 | 5d2ad1795b0dfc4a58424b2fa2f002246f653b119d362954ae270b6998e9d575 | Hash of milk (1).txt, a recipient list staged for the phishing campaign. |
| SHA256 | 6c428acbd91be85fedf9cbb334457ddea08ff624d4de88041749578e968d62a8 | Hash of milk (3).txt, a recipient list staged for the phishing campaign. |
| SHA256 | 7fda5f10a2bc212daaa467484c56eb8abf3f3681f6405c5c2fac16d4124e44ca | Hash of milk (4).txt, a recipient list staged for the phishing campaign. |
| SHA256 | 95fc58dc321b07ecc99d95359bcdee08a5beb519ead8e70e40f33928533a1b14 | Hash of dracii.mmp, the Gammadyne project file containing the campaign configuration. |
| SHA256 | c5ec55270af084d3c07d2918098d598bc2c5ca42f4189d69cdfcae2c958e5ec7 | Hash of milk (2).txt, a recipient list staged for the phishing campaign. |
| SHA256 | dc8a31a104df44b76a05c3e6d4fbe85be243cc6db0ff25e298e25cc469715046 | Hash of gm.exe, the legitimate Gammadyne Mailer application staged and abused for the campaign. |
| URL | hxxps[:]//ipelc[.]gob[.]bo/boots_store/ | Phishing kit URL hosted in a subdirectory of a compromised Bolivian government website. |
MITRE ATT&CK
T1021.001 · Remote Desktop ProtocolThe operator used the published RDP connection through the RD Gateway and reconnected to an existing remote session.T1078 · Valid AccountsThe operator used a valid domain credential to access the RDWeb portal and the terminal server.T1110.001 · Password GuessingThe separate source at 216.152.151[.]168 made repeated RDWeb login attempts, including 127 failed POSTs before one credential validation.T1566.002 · Spearphishing LinkThe mass email campaign impersonated Boots and directed recipients through a survey link to a phishing checkout kit.T1584.004 · ServerThe operator compromised the IPELC government website and placed the phishing kit in its /boots_store/ subdirectory.
Vendors
Products
IISIt also hosted a public Microsoft IIS RDWeb Access portal (the web login page for remote desktop access), and it ran the RD Gateway role (essentially a middleman between the internet and internal terminal servers).Windows ServerThe host itself is a Remote Desktop (RD) Session Host server (also known as a terminal server), a Windows Server that hosts multiple users' remote desktop sessions simultaneously.
Tools
ChainsawHowever, the Terminal Services operational logs did, so we parsed them with Chainsaw.Gammadyne MailerWe recovered their full staging directory, including a legitimate bulk email software application (Gammadyne Mailer), a project file named dracii.mmp (Romanian for "the devils"), and six target lists (text files that
Countries
Industries
GovernmentThe payload it pointed victims at was hosted on a compromised Bolivian government website, ipelc.gob[.]bo.RetailFrom what we reconstructed, this is one operator working a rotation of UK-facing themes, retail, tax and cryptocurrency, and the Boots set was simply the job loaded the morning we were watching.