Suspected ShinyHunters Member Reportedly Detained in Jordan, Cooperating With FBI
Summary
A suspected ShinyHunters member identified as Saif al-Din Khader was reportedly detained in Jordan and is helping the FBI identify group members. The group’s leak site went offline before a new site appeared.
Key points
- Reuters sources reportedly said Jordanian authorities detained Khader, known online as “Rey,” and that he is cooperating with the FBI and other law enforcement agencies.
- Khader is reportedly helping investigators review his devices and communications to identify alleged co-conspirators.
- The reported detention follows an FBI investigation into ShinyHunters’ claims that it breached bureau systems; the alleged breach and stolen-data volume have not been independently verified.
- ShinyHunters’ leak site and some related communications went offline around the reported detention, but a new leak site later appeared.
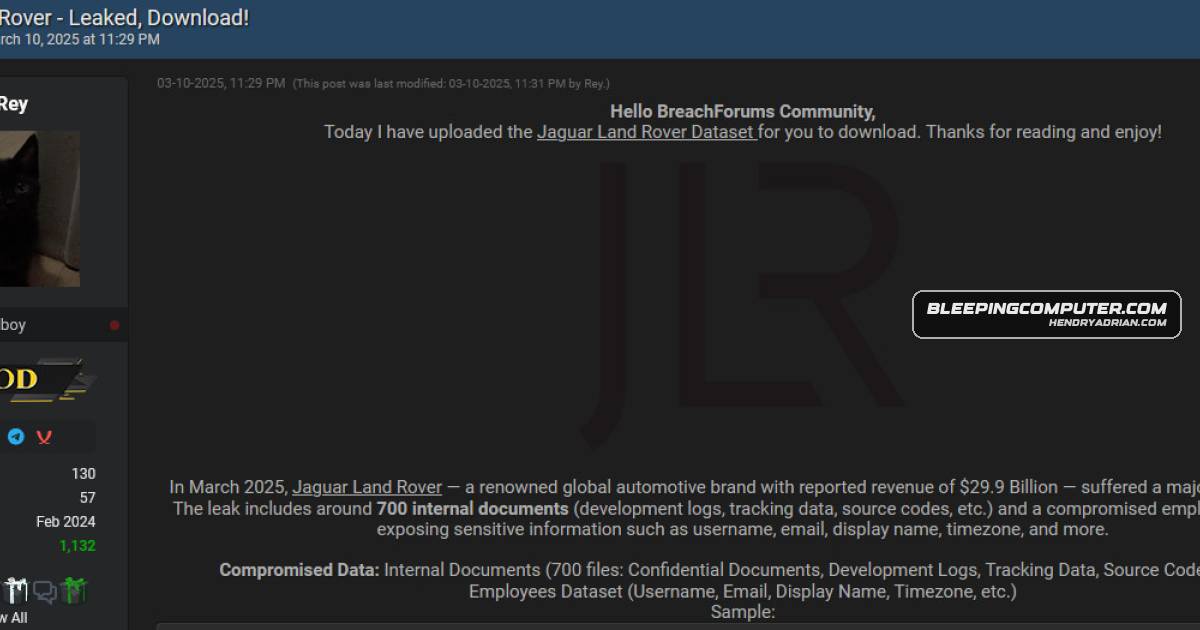
- The article says Rey has been linked to previous data-theft and extortion attacks, including breaches involving Orange and Jaguar Land Rover.
Article Details
- Event Type
- Reported detention of a suspected ShinyHunters member in Jordan and reported cooperation with law enforcement.
- Impact
- Saif al-Din Khader, known online as Rey, was reportedly detained and is helping the FBI and other law enforcement agencies identify other ShinyHunters members. The report says he is reviewing devices and communications with investigators. The detention follows a crackdown after ShinyHunters claimed to have breached FBI systems; those breach claims and the alleged theft of 2TB to 3TB of data have not been independently verified, and the FBI confirmed an investigation but did not confirm data theft.
People
Brett LeathermanFBI Cyber Division Assistant Director who publicly urged ShinyHunters members to turn themselves in.Brian KrebsSecurity journalist who reported Khader's identity after analyzing infostealer-log information and speaking with him; he could not verify Khader's claims about prior law-enforcement cooperation.Pepijn van der StapIdentified by KrebsOnSecurity and DataBreaches as a suspect arrested in Amsterdam in an investigation into ShinyHunters; previously used the online alias Umbreon.Saif al-Din KhaderIdentified in the report as the suspected ShinyHunters member known online as Rey; reportedly detained in Jordan and cooperating with law enforcement.
Threat Actors
ClopRansomware group whose data breach was mentioned in connection with an alleged ShinyHunters affiliate.HellcatRansomware operation to which Rey and two other attackers were previously reported to belong; Rey later said he was a member when discussing the Orange breach.LAPSUS$Cybercrime group whose former members were claimed to be part of Scattered Lapsus$ Hunters.Scattered LAPSUS$ HuntersCybercrime group that claimed to consist of former members of Lapsus$, Scattered Spider, and ShinyHunters; Rey was seen with administrative privileges in its Telegram channels.Scattered SpiderCybercrime group whose former members were claimed to be part of Scattered Lapsus$ Hunters.ShinyHuntersExtortion group linked to data-theft attacks; it claimed to have breached FBI systems, a claim not independently verified in the report.
Products
AWS GovCloudIn September, ShinyHunters told BleepingComputer that it breached FBI systems using an alleged Oracle PeopleSoft zero-day vulnerability before spreading laterally into FBI-managed AWS GovCloud systems.Instructure CanvasThe extortion gang was also behind a massive data-theft attack on Instructure Canvas in May that caused significant platform outages.Jira2025, Rey was one of four threat actors who claimed responsibility for a breach of Telefónica’s internal Jira ticketing system, where approximately 2.3GB of documents, tickets, and other data were allegedly stolen.Oracle PeopleSoftIn September, ShinyHunters told BleepingComputer that it breached FBI systems using an alleged Oracle PeopleSoft zero-day vulnerability before spreading laterally into FBI-managed AWS GovCloud systems.SalesforceIn recent years, the extortion gang has focused on Salesforce and other cloud SaaS environments, with campaigns linked to breaches at Google, Cisco, and PornHub.