Microsoft Outlines Five Priorities for Government Cyber Resilience
Summary
Microsoft says government agencies were the sector most affected by cyber threats in 2026 and urges governments to strengthen resilience through faster coordination, secure AI adoption, incident planning, information sharing, and exercises for essential services.
Key points
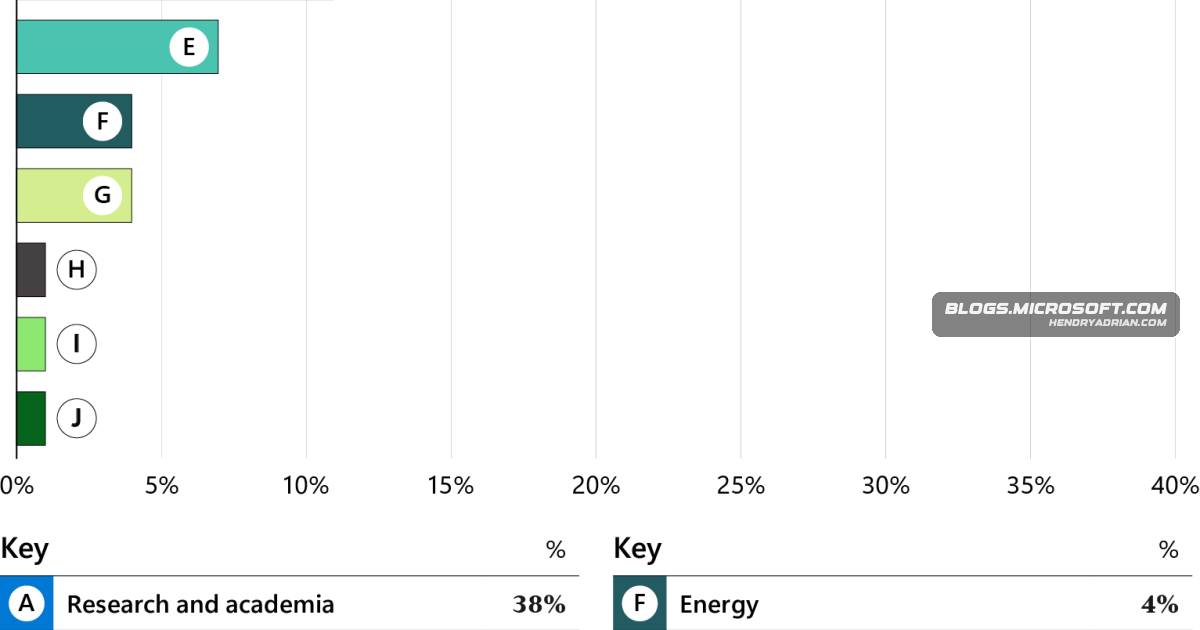
- Microsoft’s Digital Defense Report says government agencies and services accounted for 27% of observed cyber activity in 2026, up from 17% in 2025.
- Phishing accounted for 23% of observed intrusions, compared with 7% in 2025; the article also notes that attackers often use compromised identities and legitimate activity to evade detection.
- Microsoft recommends improving crisis readiness so governments can assess threats, coordinate across institutions, and respond quickly.
- It urges governments to integrate secure-by-design practices, testing, supply-chain protections, transparency, and accountability into the AI ecosystem.
- The article says valid-account intrusions resulted in additional credential theft in 52.2% of cases, and advises planning for incidents to spread across organizations and services.
- Microsoft calls for timely, two-way public-private threat information sharing and regular cross-sector exercises to help essential services continue operating during disruption.
Article Details
- Topic
- Government cyber resilience amid faster, interconnected threats and AI adoption