N0n Claims Chibitek Data Exposure, Including Client Records and Network Credentials
Summary
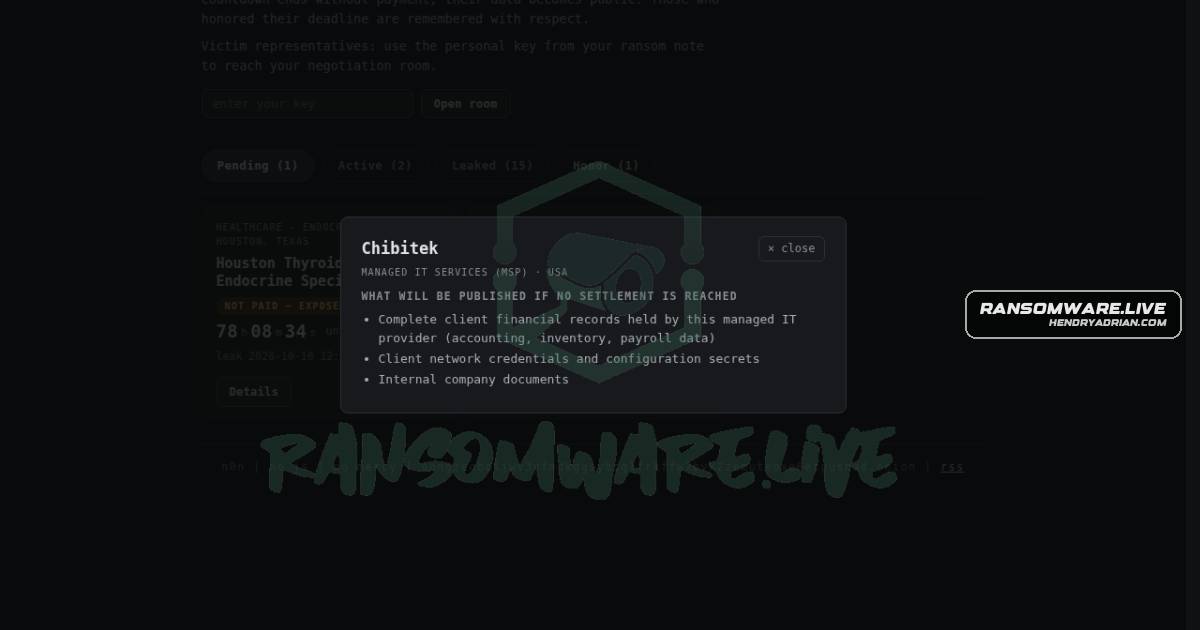
Ransomware group N0n claims it compromised managed IT provider Chibitek and exposed client financial records, network credentials, configuration secrets, and internal documents. The claim is unverified.
Key points
- The ransomware group N0n claims it compromised Chibitek, a US technology-sector managed IT provider.
- The alleged stolen data includes client accounting, inventory, and payroll records, plus network credentials, configuration secrets, and internal documents.
- The listing says Chibitek did not pay and gives an exposure date of October 11, 2026.
- The post states the claims are based on public statements by N0n and have not been independently confirmed.
Article Details
- Victim
- Chibitek
- Claim Date
- 2026-10-07
- Encryption Status
- Unknown
- Exfiltration Status
- Claimed by N0n; not independently confirmed
- Exfiltrated Data
- N0n claims it obtained client financial records, including accounting, inventory, and payroll data, client network credentials and configuration secrets, and internal company documents.
- Ransom Demand
- Not disclosed; the listing says “NOT PAID,” but no demand amount is reported.
- Leak Status
- The listing labels the data “EXPOSED” and gives a leak date of 2026-10-11 04:43 UTC. The claim and data authenticity are unconfirmed.